





"injecting the Frida Gadget into the app by using the patchapk command of Objection" - Cool!

Decrypting and Analyzing HTTPS Traffic without MiTM blog.silentsignal.eu/2020/05…


My attempt to describe the procedure of analyzing and cloning the remote control of a 433MHz RC-switch using an Arduino Nano and a TI CC1101 module
grspy.com/cloning-the-remote…
An Android app to read and write MIFARE Ultralight EV1 tags github.com/grspy/ulev1plus
#NFC #Android


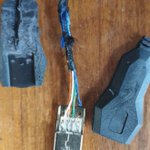
Well, look what you did @mame82 @LucaBongiorni! You made me even more paranoid than before, so I had to change that larger USB connector just to be sure... 🧐


GrSpy retweeted

1995: Mudge published "How to Write Buffer Overflows", one of the first papers about buffer overflow exploitation. Then @dotMudge sent a copy to @aleph_one, who wrote "Smashing the Stack For Fun and Profit" in 1996. Seminal paper to seminal paper. Mudge's: insecure.org/stf/mudge_buffe…

GrSpy retweeted

Side channel analysis of RF emission using #MachineLearning and #TensorFlow to steal PIN numbers from thin air. This is really impressive work… and also deeply scary. HT @LargeCardinal leveldown.de/blog/tensorflow…

GrSpy retweeted

[sic] – Encode JS with 2 different symbols only
⟶ aem1k.com/sic/
A super tiny library to inject self-executing JavaScript code. The obfuscated code contains nothing but a sequence of square brackets!
[][[][[]]][[]][[]][[][[]]][[][[]]][[][[]]][[][[]]][[]][…

GrSpy retweeted

Quick proof of concept.
Do you need an entire Bluetooth module just to wirelessly trigger 2 static payloads on a dinky ATTiny chip? Nope!
I took a DemonSeed build kit, added just 1 resistor & some patch wires. Now it has wireless control of as many payloads as you want!

A simple command line utility I put together from the #proxmark client, to quickly list the annotated ISO14443A trace of a .trc file, which was saved using AndProx.
gist.github.com/grspy/62db63…


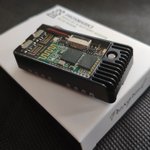
Yay! It's finally here and it's awesome! Many thanks @herrmann1001 @RfidGroup @Lab_401 :)
#proxmark #rdv4 #blueshark


