

Proactive runtime enforcement for cloud and AI
Runtime
Joined July 2023
- Tweets221
- Following134
- Followers112
- Likes45



🎊 Virtual Patching is live.
🐝 Now you can protect a running applications from a specific vulnerability in one click - while engineering takes the time it needs to fix it.
Read → hubs.li/Q04BMcMF0
#RuntimeSecurity #VirtualPatching #AISecurity #CloudSecurity

🚀 We’re now part of @Anthropic's Cyber Verification Program, with access to Claude Mythos for attack validation.
If attackers are going to have that capability, defenders need it too. 💪
#AISecurity #RuntimeSecurity #CyberSecurity #Anthropic
Attackers have AI. Defenders have home advantage. 🐝
Our CEO Dror Kashti writes in @Calcalistech about turning deep runtime context into an advantage: proving real attack paths, fixing exposure and stopping harmful behavior as it happens. Read the piece: hubs.li/Q04BpyYc0
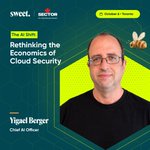
Cloud security’s math is changing. 🍬 Sweet’s Chief AI Officer, Yigael Berger, is taking the stage at Toronto’s AI x Cloud Security Summit to unpack how AI changes the cost and speed of finding, exploiting and fixing vulnerabilities. At #SECTOR26? Come say hi!

ALT Yigael_Berger_Sweet_SecTor
We're excited to share that Sweet Security has been recognized by Gartner® as a Sample Vendor for Application Detection and Response in the 2026 Gartner® Hype Cycle™ for Application Security!
#ApplicationSecurity #ADR #CloudSecurity #AISecurity #RuntimeSecurity #CyberSecurity

Black Hat's a grind.
This is the good kind. ☕
Watch reality change in real time, get caught in the act, and walk out with the shirt in one hand and a coffee in the other.
👉 Come see what we’ve been brewing hubs.li/Q04qb28Y0 #BlackHat #BHUS

ALT Sweet Autonomous Experience BHUS 26
We're bringing The Sweet Stop to Black Hat ☕
Aug 5–6 🍭 Mandalay Bay 🍭 Booth 5721
Barista-made coffee, live runtime demos & a first look at how Sweet stops bad behavior in runtime.
👉 Coffee's on us - reserve your 20-min session: hubs.li/Q04p2qcM0

🇺🇸 Happy 4th of July - 250 years of American independence!
To our US team, customers, partners, and the security community: thank you for being part of our journey. Wishing you a safe and joyful holiday from all of us at Sweet! 🎆
#America250 #FourthOfJuly

🎙️ Our CEO & co-founder Dror Kashti joined @avivfrenkel podcast @calcalist. It's in Hebrew, but the themes translate 👇
30+ years in Israel's cyber establishment, why "agentic" isn't a dirty word & why he's happy to spend on AI tokens.
🎧 hubs.li/Q04mYWGk0
The gap between granted access and used access is where most identity risk hides.
Introducing Sweet Entitlements: runtime-powered visibility into permissions, identities, and access paths.
Read more: hubs.li/Q04lHM-y0

Big milestone for Sweet Security: we're expanding into the U.S. federal market and pursuing FedRAMP Moderate authorization, with @Coalfire supporting our journey.
Learn more: hubs.li/Q04kSG320
#FedRAMP #CloudSecurity

Another read on Sweet Attack. 📰
TechDay US gets to the core of why we built it: fewer theoretical findings, more proof of which attack paths work.
Sweet Attack exposes attack chains with evidence and remediation paths.
Read more: hubs.li/Q04gGjYC0
#AISecurity

Sweet Attack is already making headlines. 🗞️
SecurityWeek covers the shift behind our launch: AI red teaming only works when the agent understands the real environment.
Sweet Attack validates the paths attackers would actually take.
Read the coverage: hubs.li/Q04gpp340

Attackers rarely move one finding at a time.
They chain vulnerabilities, identities, APIs, permissions, and runtime behavior into usable paths.
Sweet Attack validates exploitable attack paths, so teams know what to fix first.
See how: hubs.li/Q04gshnS0
#RedTeam #Mythos

Mythos meets its match.
Introducing Sweet Attack 🤖: the AI red-team agent powered by Sweet’s runtime intelligence to validate real attack paths in production.
The myth is that defenders can’t keep up. Sweet Attack debunks it.
Read now: hubs.li/Q04gpSTk0
#RedTeam #Mythos


Twelve consecutive years of clean red-team reports. Three days into our engagement: fully exploitable attack chains.
On Wednesday — May 13 — we'll tell you how. Announcing soon.

Mythos forced every board into a new question. On Wednesday — May 13 — we share our answer.
Coming soon.

