

Continuous Security Testing - Reduce exposure time & prevent breaches using proven human-driven testing methodologies.
Madison, WI
Joined April 2016
- Tweets1.4K
- Following204
- Followers1K
- Likes246




Hot take: AI won't replace pentesters. Not because of capability, because of context.
Two findings that prove it:
1. Caption encoder, unauthenticated access - only found because a tester checked the broadcast schedule before retesting
2. Source code monorepo compromise - started with one suspicious VM timestamp a human noticed while reading script output line by line
Full breakdown on the blog →
hubs.la/Q04l4yQS0

Join us on June 12 at 12pm CDT for Hacking in the Age of AI: AI as the Attacker’s Toolkit.
AI is changing how attackers move, but it’s also changing how our pentesters test. In this Hacker Happy Hour, Nick Aures, Nate Fair, Stephen Naragon, and Nick Berrie will dig into how AI is being used for faster recon, custom payloads, vulnerability discovery, social engineering, and AI red teaming.
If your adversaries are using AI to move faster, are you testing like they attack?
Register here: hubs.la/Q04kl11R0
#aitesting #webinar #pentesting
Tenant enumeration is dead.
Microsoft has now patched both techniques that allowed full tenant domain discovery from a single unauthenticated request.
That changes recon against M365 environments significantly.
The signals still exist, tenant IDs, MOERA prefixes, brand metadata, but no single query gives you the full picture anymore. Effective enumeration now means chaining techniques together, validating against large datasets, and in some cases requiring authentication.
Juan Pablo Gomes Postigo breaks down:
• what the original technique was
• what still works today
• how we updated hubs.la/Q04hDQ9f0 going forward
hubs.la/Q04hGhk50
#CyberSecurity #Pentesting #IdentitySecurity #SecurityResearch

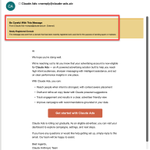
🚨 You got bait! We recently spotted a phishing email announcing access to “Claude Ads” - supposedly a new ad platform for Anthropic’s Claude AI.
There’s just one problem: Claude Ads doesn’t exist.
The scary part? The email looked incredibly believable.
The attackers replicated Anthropic’s branding almost perfectly polished design, AI buzzwords, realistic product language, and even a newly registered domain: claude-ads dot ai
It looked exactly like the kind of AI product launch you’d expect to see today.
Always verify the sender and domain before clicking.
Have you seen similar AI-themed phishing emails lately?
#YouGotBait #CyberSecurity #Phishing #SocialEngineering #CyberAwareness

Your AI tools have an attack surface, but has anyone tested it? Join our team on April 24th for "AI as the New Attack Surface" to hear what they're finding when AI tools are in scope.
🔗Register: hubs.la/Q04bcj-T0

Sprocket Security wins Best Solution in Offensive Security at the Global InfoSec Awards during #RSAC 2026 🎉
Recognition is great, but what matters more is the shift: continuous testing that keeps up with real-world change
Read more: hubs.la/Q048ppc20
#cybersecurity #infosec

Your e-commerce API isn’t protecting customers. Your cart token is.
One leaked cart ID can expose addresses, phone numbers, and order history and most platforms treat it like a session cookie.
How we actually pentest commerce workflows (not just endpoints):
hubs.ly/Q044VsWx0
#apisecurity #appsec #pentesting

Small Vite misconfig → full CI/CD compromise. No zero-days - just exposed secrets in JavaScript and chained weaknesses.
Attackers don’t break in, they connect what’s already there.
hubs.la/Q043CP1V0
#AppSec #Pentest #secrets #javascript

Last call - join us tomorrow for Hacker Happy Hour: Hype vs. Real 🍻
We’re spinning the wheel and debating what’s actually real in offensive security for 2026 from AI attacks to continuous testing and emerging threat paths.
Save your seat:
hubs.la/Q042YjFK0
#OffSec #Infosec #Pentesting #ThreatHunting

Nicholas Aures breaks down a real-world case where public registration ≠ low risk. A simple signup flow + permissive JWT + open OData queries = millions of records exposed.
Worth a read for anyone building public-facing apps:
hubs.ly/Q042xF900
#AppSec #APISecurity #WebSecurity #Auth #ContinuousPentesting

Did you know Sprocket is an Outperformer in the GigaOm's PTaaS Radar? Explore their latest report for an in-depth look at top providers' innovation and real-world testing capabilities.
hubs.la/Q0426cwt0
#ptaas #pentesting

New feature release
The Sprocket Security Platform can now be integrated with Slack to close the gap between exposure discovery and action. With this, critical alerts are delivered directly into the workflows your teams already use.
hubs.la/Q0425pNR0

Point-in-time pentests keep missing modern threats. Our testers share what’s actually defining 2026, from identity misconfigs to chained low-severity bugs.
Quick read:
hubs.la/Q03_Pk520
#cybersecurity #pentesting #infosec

Hacker Happy Hour: Hype vs. Real. Our pentesters spin the wheel and have 5 minutes to argue if it’s hype… or the real deal.
📅 Feb 13 | 🕛 12pm CDT
🎙️ Live webcast
Register: hubs.la/Q03_Lb__0
#CyberSecurity #Pentesting #InfoSec #HackerHappyHour
PTaaS is better than annual pentests, but it’s still not continuous security testing.
Fixed scopes + engagement windows can’t keep up with modern, fast-changing environments. The real risk often lives between tests.
Why that matters 👇
hubs.la/Q03_98xY0
#PTaaS #Cybersecurity #AppSec #DevSecOps

Our night cleaners claim this is standard maintenance...should we be worried? 🤔
Office status: swept, mapped...compromised?! 🤖


What does security look like inside one of the world’s largest financial institutions? 🤔 In the latest Ahead of the Breach, Citi’s Ryan Hays shares how risk, resilience, and strategic thinking come together at scale with lessons that matter for teams of all sizes.
Check it out
hubs.la/Q03-3Fbx0
#CyberSecurity #OffensiveSecurity #RiskManagement #ThreatModeling #SecurityLeadership

The ROI problem in #ASM is about tracking meaningful outcomes.
Read more for better ways to measure👇
📊 Time to ownership
🔐 Reduction in risky endpoints
🗑️ Decommission timing

Attack Surface Management usually proves visibility, not safety.
Teams count assets and alerts, but can’t show reduced exposure.
ROI only appears when risky assets get owned and fixed faster, not when inventories grow.
🔗 Why ASM feels busy but ineffective → thehackernews.com/2026/01/th…

🎉 Happy New Year from all of us at Sprocket Security! 🎉
As we step into 2026, we’re grateful for our incredible customers, partners, and employees who make everything we do possible. Here’s to a year filled with success, innovation, and stronger security for all. Let’s continue building a safer future together!
Wishing everyone health, happiness, and prosperity in the year ahead. 🥂
#HappyNewYear hashtag#SprocketSecurity #2026
