

Proactive defense starts with bite-sized #threatintel from the @DomainTools Security Research team. #SnackThePlanet #infosec
A Garbage File On The Gibson
Joined March 2021
- Tweets235
- Following134
- Followers870
- Likes49


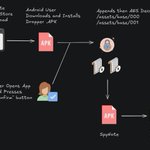



DTI finds an actor using the Google Play Store to install malware delivery sites disguised as legitimate payment and government identity applications for users in Southeast Asia. Read the post at the link below ⬇️
dti.domaintools.com/banker-t…
#Cybersecurity #ThreatIntel #Cybercrime

New research raises questions about PoisonSeed using TTPs similar to SCATTERED SPIDER. The DTI team identified 21 new malicious domains spoofing SendGrid & using fake Cloudflare CAPTCHAs to harvest credentials:
dti.domaintools.com/newly-id…
#ThreatIntel #PoisonSeed #SCATTEREDSPIDER

ALT Image displaying a list of internet IP addresses followed by various domain names, including well-known entities like Amazon AWS and SendGrid. These 21 domains are PoisonSeed Domains Registered Since 1 June 2025.
🚨 Threat intel goldmine 🚨
The "Kim" leak exposes a DPRK APT expanding operations into Taiwan and targeting identity systems. Our analysis provides IOCs and defensive guidance for nation-state analysts and SOC teams: dti.domaintools.com/inside-t…
#ThreatIntelligence #Kimsuky

ALT Diagram showing web domains and their connections: koala-app[.]com linked to mofa.go[.]kr, webcloud-notice.com linked to spo.go[.]kr, nid-security[.]com linked to dcc.mil[.]kr, and jeder97271@wuzak[.]com linked to wuzak[.]com.
A new #SpyNote report is out! 🚨 Dive into the tactics of this Android RAT campaign, from dynamic payload decryption to new obfuscation methods. Learn how threat actors are using deceptive Google Play Store clones to target users:
dti.domaintools.com/spynote-…

Recent DTI research tracked a trojan using hosted PowerShell scripts, uncovering bulletproof hosting services and how #LummaStealer remains a threat.
Read the full report: dti.domaintools.com/hunting-…
#Cybersecurity #ThreatIntel #Malware #BlueTeam

DPRK IT workers infiltrate global remote companies via forged identities, siphoning millions to fund North Korea's weapons. A critical insider threat risking IP theft & espionage. Get essential intel:
dti.domaintools.com/from-lap…
#threatintelligence #cybersecurity #infosec

ICYMI: Skeleton Spider (FIN6) is using trusted cloud services like AWS to deliver malware via fake resumes & job lures. Social engineering meets stealthy infrastructure. Learn more here: dti.domaintools.com/skeleton…
"In a twist on typical hiring-related social engineering attacks, the FIN6 hacking group impersonates job seekers to target recruiters, using convincing resumes and phishing sites to deliver malware." Read more from @BleepinComputer here: bleepingcomputer.com/news/se…

"The financially motivated threat actor known as FIN6 has been observed leveraging fake resumes hosted on Amazon Web Services (AWS) infrastructure to deliver a malware family called More_eggs." Read more from @TheHackersNews here: thehackernews.com/2025/06/fi…

SecuritySnacks retweeted

FIN6 hackers pose as job seekers to backdoor recruiters’ devices - @billtoulas
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…
FIN6 (Skeleton Spider) is using AWS & fake resumes to deliver malware via trusted job platforms.
⚠️ Realistic lures
🕵️♂️ Cloud-hosted phishing
🥚 More_eggs backdoor
Read the full analysis here: dti.domaintools.com/skeleton…

SecuritySnacks retweeted

🚨 Watch your clipboard!
A fake DocuSign site tricks users into running malware with a sneaky PowerShell script—copied via CAPTCHA.
✔️ Clipboard poisoning
✔️ Fake Gitcode & DocuSign sites
✔️ NetSupport RAT deployed
👀 Learn how it works → thehackernews.com/2025/06/fa…
DomainTools Investigations’ (DTI) latest analysis uncovers a technically sophisticated malware campaign that uses fake CAPTCHAs and spoofed document verification pages to trick users into self-infecting their machines with the NetSupport RAT.
dti.domaintools.com/how-thre…

🎵 Newsletter No. 5 is here!
Daniel Schwalbe, CISO @DomainTools, shares the latest on:
🔹 VenomRAT via fake sites
🔹 Malicious Chrome extensions
🔹 Exploiting viral media events
Read the full scoop 👉 domaintools.com/resources/bl…

SecuritySnacks retweeted

What do cats have to do with Lumma C2 malware?
Some domains linked to the infostealer use a landing page titled “About Cats” 🐱
How many domains? Avg risk score? IOC overlaps?
🔗 Read more: domaintools.com/resources/bl…

ICYMI!
Ian Campbell's latest Recommended Reading list is out. This edition features @MaltegoHQ's Human Element Podcast hosted by @bapril!
Learn more and see Ian's other Recommended picks here: dti.domaintools.com/cybersec…

"The attackers used websites that mimicked popular brands to trick users into installing the apps that had been laced with malware designed to steal passwords and digital wallets." Read more from @Forbes here: forbes.com/sites/zakdoffman/…

SecuritySnacks retweeted
🚨 Hackers built a fake Bitdefender site to push Venom RAT—stealing passwords, crypto, and control.
Behind it? A stealthy combo of open-source tools, MFA bypass tricks, and real-time phishing tactics. You won’t believe what they’re exploiting now.
Read: thehackernews.com/2025/05/cy…

SecuritySnacks retweeted

@DomainTools Crooks use a fake #antivirus site to spread #Venom #RAT and a mix of malware
securityaffairs.com/178366/m…
#securityaffairs #hacking #malware
