

Practical Secure Coding Training for Developers, DevOps and QA engineers.
London, UK
Joined March 2020
- Tweets504
- Following7
- Followers325
- Likes84



Pinned Tweet
SecureFlag is the only 💯 Hands-On Secure Coding Training platform for Developers, DevOps & QA engineers.
Learn how to identify and remediate real security issues using familiar tools and technologies in an authentic development environment 📲bit.ly/3LXkMil
Our new SDLC Metrics feature matches each code commit with the author’s training records 📊
Teams can measure how much code comes from trained developers and where training coverage is lowest.
See how SDLC Metrics links training to shipped code 🔗
blog.secureflag.com/2026/10/…

Last week, we asked who is responsible for risk when AI agents help write and ship code. 100% said: the developer who ships it.
But when one person carries all the risk, accountability becomes a single point of failure. Vendors, security teams & orgs share the load.
#DevSecOps

Only one week left until we show you how to bring threat modeling up to speed with AI coding!
No bloated slide decks ❌
Just 45 minutes of live demos ✅
It’s live only, so register now: app.livestorm.co/secureflag/…
#ThreatModeling

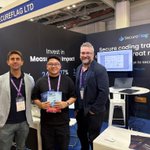
Hallo Amsterdam! The SecureFlag team is at the Cyber Security and Cloud Expo, part of TechEx Europe. Find us at Booth 108 today or tomorrow and we'll be happy to talk you through SecureFlag's secure coding training and threat modeling products.
#cybersecurity


Introducing our new citizen developer course on AI agent security 🤖
Over 80% of security teams lack full visibility into what business users build with AI agents. Hands-on training reduces the risk.
Help everyday employees use AI more securely 👇
blog.secureflag.com/2026/10/…

Compliance reqs are tightening, but proving you meet them shouldn't mean hunting by hand ⏱️
ISO 27001, SOC 2, PCI DSS, HIPAA & AI regs want proof your software is built securely. SecureFlag pulls it together automatically.
Generate audit-ready evidence 👇secureflag.com/solutions/mee…

SecureFlag has been named one of the UK’s Fastest-Growing Companies 2027, ranking 70th in the FT’s inaugural list! 🎊
Huge thanks to our incredible team and to every organization making secure development a priority.
See the full ranking: ft.com/content/92195205-ac56…
#FT150

AI-generated code fails security tests on nearly half of all tasks, and it's not improving as models get smarter* ⚠️
AI optimizes for code that works, blind to your threat context—so it can pass tests and still ship vulnerabilities.
See more: secureflag.com/solutions/ai-…
*Veracode

Next Monday, SecureFlag will be at the Cyber Security & Cloud Expo in Amsterdam! Our team is excited to chat about how our platform can enable the future of secure, connected enterprises. Find us at Booth 108!
#Cybersecurity #AppSec #DevSecOps #SecureCoding
A threat modeling tool works best when the developers on your team can use it 🧑💻
Some tools use diagrams, others use code, and others automate the process.
Compare free and commercial tools in our guide: blog.secureflag.com/2026/10/…
#ThreatModeling #AppSec

A smashing first day at GovWare Singapore, Asia's Premier Cyber Week! You can still catch us on Wednesday and Thursday. Come by booth H46 and our team will be happy to chat you through our secure coding training and threat modeling products!
#securecoding #cybersecurity


Security works when it fits inside the developer workflow.
That's why SecureFlag integrates with GitHub, GitLab, Jira, Azure DevOps, CI/CD pipelines, and MCP agents—bringing security closer to the work.
See the full catalog 👇
secureflag.com/integrations/…

What changed in the 2026 OWASP Top 10 for LLM Applications? 📋
Excessive Agency and Unbounded Consumption moved up the most.
See the full list and how SecureFlag helps teams address these risks 👇 blog.secureflag.com/2026/10/…

The cheapest vulnerabilities to fix are ones that never get coded in the first place 💡
Secure-by-design means spotting how features could be misused at design stage then defining the controls before development starts.
See it in action: secureflag.com/solutions/ena…
#SecureByDesign

Hold your horses! SecureFlag is heading to LASCON in Austin in three weeks. It is a gathering of security leaders and architects sharing cutting-edge advancements. We also will be hosting the conference's Capture the Flag, catch us there!
#cybersecurity #securecoding

Security training slides don’t secure software. Developers need to practice finding and fixing vulnerabilities in the environments they use every day 💻
Our hands-on training covers 75+ languages and frameworks.
Explore SecureFlag Labs: secureflag.com/labs/?utm_sou…
#SecureCoding

#CybersecurityAwarenessMonth challenge from Hamish Hansford of Australia's Home Affairs on the latest SecurePod: explain cyber to someone in a way they understand!
🔴 YouTube: youtu.be/Rr8ABK6UEoY
🟢 Spotify: open.spotify.com/episode/5eq…
#cybersecurity #securepod

Does every feature get the same security review, or only the ones the team has time for? 🛡️
The SecureFlag MCP Server runs the same threat modeling and training steps on every epic.
Learn how to make security consistent: blog.secureflag.com/2026/10/…
#ThreatModeling #DevSecOps

Most teams find security problems after code ships. By then, fixes cost more 💸
SecureFlag offers one platform for developer security: model threats at design, build secure coding skills in hands-on labs, and prove compliance.
Explore our platform 👇
secureflag.com/platform/?utm…

The more code AI generates, the more human judgment matters.
Developers must still spot insecure assumptions, challenge weak requirements & make sure features ship safely 🛡️
Build faster. Keep security in the loop.
Prepare for AI-assisted development 🔗 secureflag.com/solutions/ai-…
