

Putting prevention first with Continuous Vulnerability and Exposure Management, Smart Prioritization, and Automated Remediation. Vulnerabilities hate us.
California, US
Joined September 2009
- Tweets1.8K
- Following341
- Followers537
- Likes91





Pinned Tweet
Songs from the SOC: #7
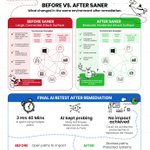
AI Anxiety: The Remediation Rush
AI is getting really good at finding security weaknesses.
The problem? Attackers can use those capabilities too.
Finding vulnerabilities is becoming easier. Reducing risk before they can be exploited is the real challenge. While patches are being built and roadmaps are being planned, the clock is still ticking.
A lighthearted reminder that while finding weaknesses gets easier, Prevention remains the foundation of security.
#CyberSecurity #AI #CloudSecurity #VulnerabilityManagement #Infosec #PreventionFirst #SecPod #mythos #gpt
CVE-2026-97229 is a CVSS 10.0 GitLab flaw that can allow unauthenticated remote code execution through crafted CI/CD regex input.
Self-managed GitLab users should upgrade to 19.2.8, 19.3.5, or 19.4.2.
secpod.com/learn/security-re…
#GitLab #CyberSecurity #RCE

Critical Bricksforge flaw exposes WordPress sites to remote code execution.
Attackers could exploit vulnerable sites to run code and take control of affected systems.
Update Bricksforge now:
secpod.com/learn/security-re…
#WordPress #CyberSecurity

CyberXero is linked to the theft of 628,000 Ukrainian records, using AI-assisted tooling to support initial access operations.
Read the full analysis:
secpod.com/learn/security-re…
#CyberSecurity #ThreatIntel

CVE-2026-21589 is a critical unauthenticated file access flaw affecting multiple Atlassian Data Center products.
Attackers can access specific files when the exact path is known.
Patch affected instances now:
secpod.com/learn/security-re…
#Atlassian #CyberSecurity #CVE

CVE-2026-88779 is being exploited in targeted attacks against Citrix NetScaler ADC and Gateway.
The SAML-related flaw can trigger denial of service on exposed deployments.
Upgrade to a fixed build:
secpod.com/learn/security-re…
#Citrix #NetScaler #CyberSecurity

CVE-2026-102255 is a CVSS 10.0 pre-auth SSRF flaw in SonicWall SMA 1000.
Unauthenticated attackers could reach internal functionality and perform unauthorized operations.
Apply the fixed platform hotfix now:
secpod.com/learn/security-re…
#SonicWall #CyberSecurity #CVE


Two critical Check Point flaws, CVE-2026-85102 and CVE-2026-85103, can allow unauthenticated remote code execution on VPN-enabled gateways and management appliances.
Apply LivePatch Take 24 or the relevant hotfix immediately.
secpod.com/learn/security-re…

Microsoft’s September Patch Tuesday fixes 973 vulnerabilities, including 113 Critical flaws and 2 zero-days already exploited in the wild.
Prioritize the exploited zero-days and network-facing RCE flaws.
Read more:
secpod.com/learn/security-re…
#CyberSecurity #Microsoft #ZeroDay
🚨 CVE-2026-20212 puts Cisco Nexus 9000 switches at risk of root-level RCE.
Unauthenticated attackers may execute code as root or crash affected switches.
Patch affected systems or restrict access to vulnerable ports.
secpod.com/learn/security-re…
#CyberSecurity #Cisco #RCE
SonicWall SMA 1000 appliances are under active attack.
CVE-2026-83548 and CVE-2026-83549 can be chained from unauthenticated SSRF to remote code execution. SonicWall has confirmed exploitation in the wild.
Patch affected SMA 1000 systems immediately.
secpod.com/learn/security-re…
🚨 PaperCut zero-day alert: an authentication bypass can be chained into remote code execution, putting exposed servers at serious risk.
Read more:
secpod.com/learn/security-re…
#CyberSecurity #ZeroDay #PaperCut #RCE

🚨 Cl0p is exploiting CVE-2026-12569 in PTC Windchill and FlexPLM, targeting 40+ organizations.
The flaw can enable unauthenticated RCE and data theft.
Patch affected systems now.
secpod.com/learn/security-re…
#CyberSecurity #Cl0p #CVE

🚨 GeoServer zero-day alert: a flaw in jsonArrayContains could open the door to remote code execution.
Security teams should identify exposed GeoServer instances, assess risk, and apply available mitigations or fixes immediately.
Read the analysis:
secpod.com/learn/security-re…

🚨 Gunra ransomware is exploiting Fortinet auth bypass flaws to breach networks, steal data, and deploy ransomware. (secpod.com)
Patch exposed FortiOS and FortiProxy devices now.
Read more:
secpod.com/learn/security-re…

🚨 Microsoft’s August 2026 Patch Tuesday fixes 421 vulnerabilities, including 3 zero-days.
CVE-2026-68820 is already being exploited in the wild.
Prioritize patching and verify remediation.
secpod.com/learn/security-re…
#PatchTuesday #CyberSecurity #ZeroDay

🚨 Actively exploited Metabase zero-day with a CVSS 10.0 score.
Security teams should identify exposed instances, apply available fixes, and verify remediation immediately.
Read more:
secpod.com/learn/security-re…
#CyberSecurity #ZeroDay #Metabase