
Cloud Threat Researcher Author of Inboxfuscation, CloudGrappler | Speaker at BlackHat*, DeepSec, BlueTeamCon, FIRSTCON, BSides*
Kosovo
Joined January 2024
- Tweets129
- Following243
- Followers73
- Likes624
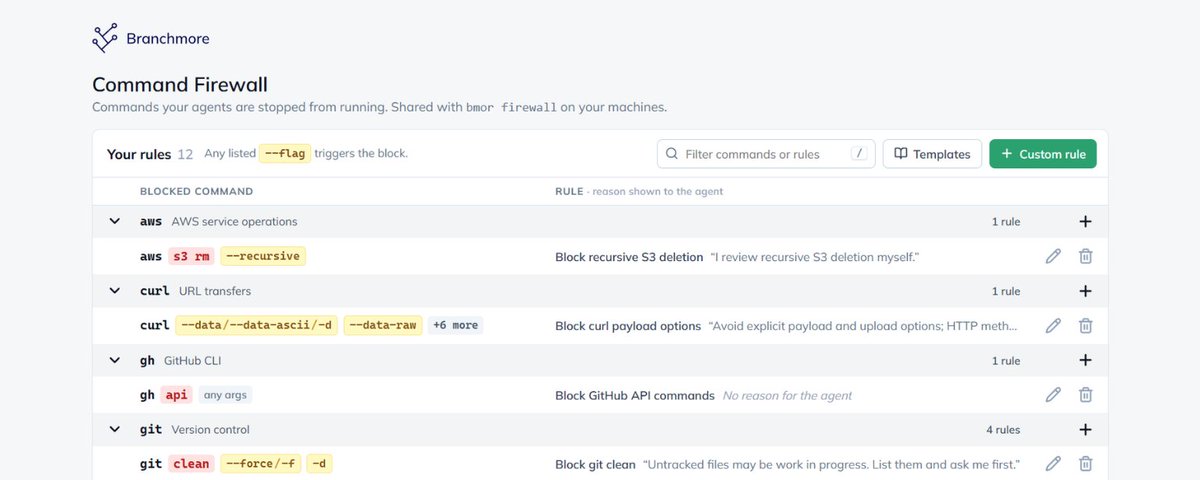
This is a great way to stop AI burning your house! I’ve been using Branchmore for a while to build, and this is definitely one of the most useful feature for a security professional

This is a clear example of why checking the sender isn’t enough. It’s their real email address, but someone else is using the account. An event invite from someone you know probably won’t raise many eyebrows.


The ConnectWise incident is another reminder: a breach at your supplier can become your security problem.
That applies to email, too. A message from a supplier’s real mailbox can still come from an attacker.
The relationship is trusted. Is the person behind the email?
#SupplyChainSecurity #IdentitySecurity #Microsoft365 #EmailSecurity #BEC #CyberSecurity #ConnectWise

Andi Ahmeti retweeted

JUST IN: Cybersecurity experts warn that AI agents are highly vulnerable to phishing emails containing hidden malicious instructions.
Andi Ahmeti retweeted

☀️ I just launched @Branchmore on @ProductHunt!
Branchmore tracks tokens and agent traces to find problems with token costs, unsafe commands and unproductive agents. Then it converts those learnings into fixes for your AGENTS.md and Agent Skills.
producthunt.com/products/bra…

Andi Ahmeti retweeted

Cyber Run Club: Thought of the run
“Hard to do the puzzle without seeing the image on the top of the box”
I heard this line on a podcast I was listening to on my run today and for some reason I just keep coming back to it!
Maybe it’s because my sisters growing up love to do puzzles so it’s uncommon to have a half finished puzzle on a table somewhere in the house with the box propped up next to it!
But it’s also helped with my running journey!
Getting into running these past 7 quarters (yes I think of my life in quarters you can thank sales for that! 😂) has forced me to humble myself and be a bigger all over again.
One of my biggest takeaways is the value that comes from input from those that have already been where I’m trying to go and done what I’m trying to do!
Aka those that have seen the top of the puzzle box!
They can help me with technique, tips on workouts so I don’t burn myself out, what the right kind of running shoes are and a million other things!
Not because they are an expert, but just because they are further along the journey than I am! They have seen the top of the box or at least the next portion of the top of the box!
Whether you are doing a puzzle, starting a running journey, building a startup, or even just starting your career, having a few people help be in your corner to show you the top of the box can be incredible helpful!
For those that have answered my rookie running questions, THANK YOU! 💪
PS - Stole this photo from my wife during one of the morning runs this week! Look how cool! 👀

Andi Ahmeti retweeted
Tip: the automation mindset is important we use AI more. Turn repeated tasks into Skills, and repeated Skills into scripts.
You'll save tokens, time and improve consistency.
I elaborate in this article: ashu.co/automate-chats-into-…

Andi Ahmeti retweeted

Big thanks to @thecyberwire for covering our recent ChatGPhish research from @SecEagleAnd1 in their recent episode.
"Ahmeti demonstrated how attackers could insert fraudulent account warnings and malicious links into otherwise legitimate summaries. He also showed that embedded QR codes could redirect victims from their desktops to attacker-controlled websites on mobile devices, potentially bypassing browser-based security protections. The vulnerability stems from ChatGPT treating untrusted external content as trusted input during summarization."
thecyberwire.com/podcasts/da…

Andi Ahmeti retweeted

ChatGPhish Vulnerability Turns ChatGPT Web Summaries Into a Phishing Surface thehackernews.com/2026/05/ch…

Andi Ahmeti retweeted

⚠️ A new technique called "ChatGPhish" turns OpenAI’s ChatGPT into a #phishing tool.
No special prompt required... simply summarizing a malicious web page can cause #ChatGPT to display phishing links, fake security alerts, QR codes, and attacker-hosted images in its trusted interface.
Full story: thehackernews.com/2026/05/ch…

Andi Ahmeti retweeted

⚠️ New ChatGPT Vulnerability Lets Attackers Turn Web Pages Into Phishing Payloads
Source: cybersecuritynews.com/chatgp…
A browser-based prompt injection technique that transforms any web page into a phishing delivery surface by exploiting ChatGPT’s page summarization feature, rendering attacker-controlled links, fake security alerts, and QR codes directly inside the trusted ChatGPT interface.
The attack builds on the same trust-transfer logic previously demonstrated against Microsoft Copilot, where attacker-crafted email content could manipulate AI-generated summaries through Cross Prompt Injection Attacks (XPIA).
ChatGPhish escalates that premise by swapping the bounded email primitive for the browser where users spend the majority of their working day.
#cybersecuritynews #vulnerability

Andi Ahmeti retweeted
Attacker-controlled text in emails can shape what Copilot shows you in Outlook summaries — producing security alerts that look system-generated.
P0 Labs documented how. Read more.
hubs.ly/Q04dyYQK0

Andi Ahmeti retweeted
🚨Microsoft Copilot Email & Teams Summarization Vulnerability Enables Phishing Attacks
Source: cybersecuritynews.com/micros…
Microsoft Copilot Email Summarization Vulnerability allows an attacker to hijack Copilot's output by embedding attacker-controlled text in an ordinary email, producing convincing phishing content within the assistant's trusted summary interface without relying on attachments, macros, or traditional exploit code.
The vulnerability allows an attacker to hijack Copilot's output by embedding attacker-controlled text in an ordinary email, producing convincing phishing content within the assistant's trusted summary interface without relying on attachments, macros, or traditional exploit code.
#cybersecuritynews #microsoftcopilot

Andi Ahmeti retweeted
Attackers now just need your AI to repeat after them.
P0 Labs documented how attacker-crafted text in an email turns a Microsoft Copilot's summary output into a phishing delivery mechanism.
Full research: hubs.la/Q046xjL_0
Andi Ahmeti retweeted
Our CTO, Ian Ahl, unleashed an AI agent to hunt threats in the OpenClaw ecosystem. It found active threats in minutes. Malicious “skills” were stealing API tokens + OAuth creds. Agents are becoming sysadmins, but security hasn’t caught up. Full research: hubs.la/Q041lkPM0

Andi Ahmeti retweeted
Our P0 Labs team has open-sourced a growing set of cloud & identity security tools — from threat hunting to detection automation — freely available for defenders everywhere. 🌍🔍
hubs.la/Q03YD3pT0
👉 Dive in & contribute: hubs.la/Q03YD3FV0 #OpenSource #ThreatIntel

Had a blast presenting at BSides Munich and DeepSec this week, diving into our latest work at @permisosecurity and breaking down fresh TTPs from LUCR-3 (Scattered Spider).
#LUCR3 #ScatteredSpider #PermisoSecurity #P0Labs #BSidesMunich #DeepSec #ThreatResearch #ThreatDetection


Andi Ahmeti retweeted
Our co-founders Jason Martin and @paulsnguyening sat down with @JohnJEgan to talk about how they manage their roles as co-CEOs for his recent article in @SHRM .
"When done correctly, a co-CEO structure can be a 'superpower,' helping a company navigate business complexities and run parallel strategic initiatives."
shrm.org/executive-network/i…

Andi Ahmeti retweeted
LUCR-3 (Scattered Spider) is back — and more dangerous than ever.
Join @permiso_io’s P0 Labs researchers @andi_ahmeti & @abianmorina at #BSidesMunich + #DeepSec as they expose LUCR-3’s latest TTPs across cloud & SaaS environments.
#CyberSecurity #ThreatIntel #CloudSecurity
