

Security Researcher at @CredShields | Bug Bounty Hunter | Audits : Solidity & Rust | Pentester
Web3
Joined December 2020
- Tweets2.1K
- Following1.3K
- Followers1.5K
- Likes5.4K




Shreyas retweeted

hot take: the loudest people in security tend to be the least technically skilled, myself included.
you are either terminally online or terminally obsessed with hacking something for weeks, no free lunch, my posting gaps usually mean i am actually getting technical work done.
Shreyas retweeted

I got curious about Immunefi's submission fees so I checked their public fee collector.
It received 415,639 USDC across 6 months (from 20 April through 26 October 2026).
These were 8,346 transfers from 2,074 addresses.
The five largest sender wallets paid 32,005 USDC combined:
1. 0x2e804b...12aef8 - 9,945 USDC (258 payments)
2. 0x0059f3...c5e5be - 6,115 USDC (258 payments)
3. 0xb97c45...a1b2b7 - 5,450 USDC (90 payments)
4. 0x55b2e4...7784d0 - 5,400 USDC (54 payments)
5. 0x9889b9...2b51a6 - 5,095 USDC (128 payments)
The median incoming transfer was 25 USDC and the average was about 49.80 USDC.
These are public Ethereum transfers, checked through block 26,278,968.
The fee collector's address is in the comments.
Shreyas retweeted

Cybersecurity folks are tired of being right for decades on advising to get the basic security principles correct instead of chasing the next shiny new thing.
I think defensive AI will certainly have a big role in near future but only if we get the deterministic fundamentals fixed first.


Shreyas retweeted

I'm seeing firsthand how AI can empower experienced auditors.
It's as if auditors were historically warriors with swords. Then they discovered the existence of guns (AI) and now some auditors even use machine guns.
Speed and accuracy is much better than ever. Don't stay behind.
Shreyas retweeted

I think something dangerous is happening to audits.
It seems like there are fewer audits and audit prices have gone down.
Cheaper audits should be good right?
Not necessarily
🧵👇
Shreyas retweeted

1/ 🚨 DamlForest just dropped — The CryptoZombies for DAML Smart Contract Security 🌲🔐
Hunt real vulnerabilities, fix DAML contracts in-browser, and grow your tree from Seedling → Ancient Tree.
12 Trails
50+ hands-on challenges
6 Growth Stages
Live Demo: damlforest.netlify.app/
Open Source: github.com/0xRayaa/daml-fore…
#DAML #Canton #SmartContracts #BlockchainSecurity #Web3Education


Shreyas retweeted

🔍 What is DAML & Canton?
Most blockchains focus on decentralization.
DAML + Canton focus on something harder:
Multi-party trust with real privacy.
A quick overview for developers, auditors & security researchers 👇
Shreyas retweeted

Or that contests remain the most effective form of audit when it comes to finding more bugs faster per dollar than any other method.
@zellic_io should open source the @code4rena platform and operational manual so projects or foundations or VCs or @ethereum or @_SEAL_Org can run these as I always felt they were: public goods. cc @samczsun

Shreyas retweeted

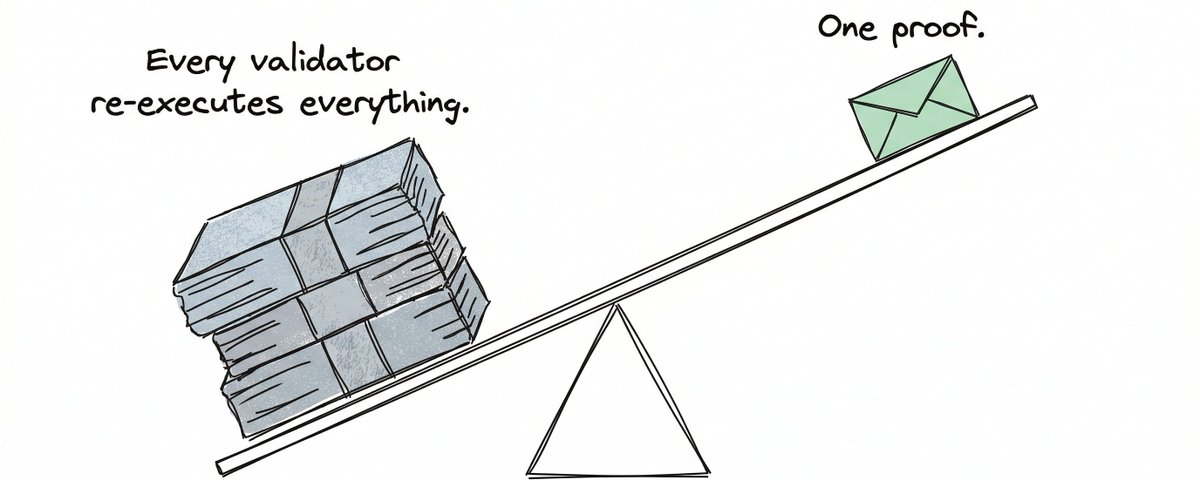
Big news from Immunefi: we just shipped Proof of Duplicate, and it's *the* feature I've been wanting to see for a long time.
For years, one of the most frustrating experiences a whitehat could have was submitting a report, putting in the hours of research, the careful write-up, the working PoC… and getting back a one-line "duplicate, closing."
No justification and no transparency. No way to push back. That era is over.
Starting now, when a submission is closed as a duplicate, it points to the original report. The researcher can read the original. They can compare the reports for themselves... and if they believe the call was wrong, they get a formal dispute button.
Verdict upheld means the report stays closed. If the verdict is overturned, the report gets reopened and goes back through triage like nothing happened, including reward eligibility.
This matters beyond the feature itself. The whitehat community is the immune system of crypto. Every protocol secured, every exploit prevented, every billion in TVL that didn't get drained.
For this immune system to keep working, things have to keep improving for whitehats. Proof of Duplicate is just one piece. There will be more.
SR Summer 2026 is coming.



Shreyas retweeted

CredShield, with support from the One Trillion Dollar Security Initiative, has released the annual OWASP Smart Contract Top 10.
This list provides an overview of the most critical smart contract risks for developers and security teams to protect against today.

🚀 The OWASP Smart Contract Top 10 team announces the 2026 OWASP Smart Contract Top 10. New research highlights the most critical smart contract risks, helping Web3 developers and security teams stay ahead of evolving threats. owasp.org/www-project-smart-…
#OWASP #SmartContracts #Web3 #OpenSource

Shreyas retweeted

Over the past several years, I’ve had the privilege of leading the OWASP®️ Foundation Smart Contract Top 10 initiative.
What began as a need for clarity around recurring smart contract failures has evolved into a structured framework that reflects how contracts actually break in production.
The 2026 edition defines the primary contract-level failure patterns that consistently lead to loss in blockchain systems, grounded in exploit data and practitioner experience.
Proud that @CredShields and @SolidityScan contributed deeply to this effort.
Sincere gratitude to the Ethereum Foundation Ecosystem Support Program for supporting the OWASP Smart Contract Security initiative and strengthening security standards across the ecosystem.

CredShields and @SolidityScan are proud to contribute to the release of the @owasp Smart Contract Top 10 2026.
OWASP Smart Contract Top 10 defines the primary contract-level failure patterns that repeatedly lead to loss in blockchain systems.
Sincere gratitude to @ethereumfndn Ecosystem Support Program for supporting the OWASP Smart Contract Security initiative.
owasp.org/www-project-smart-…


Shreyas retweeted
January hit different!
🔥 Just wrapped my first collab with the absolute legends at @PashovAuditGrp — and it was straight fire.
Massive respect to these best auditors who made it unforgettable: @m3rlinbx0 @saidamdev @x0sauce
Huge thanks for the opportunity @pashov @cvetanovv0 @danogurtsov
Report Link: github.com/Sanket-722/Audits…

