Cybersecurity signal, minus the noise. Daily SOC/blue team news, breakdowns & alerts. New ebook out now ⬇️

Joined June 2026
Candiru spyware targeted Al Jazeera through zero-click attacks embedded in ads—no user interaction needed. SOC teams must rethink ad filtering and monitor ad traffic for unusual activity. #Candiru #ZeroClick #AdSecurity #SOC #ThreatIntel
1
7
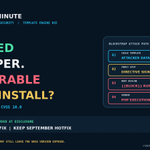
1/5 A Magento patch was published. A standard Composer install may still leave the vulnerable base version in place. BlockStrap (CVE-2026-103849) is a CVSS 10.0 flaw that can give unauthenticated attackers arbitrary PHP execution. 🧵
1
1
48
4/5 Do not remove the September VULN-39341 hotfix. BlockStrap and StyleSmuggler are separate flaws in the template engine. The October fix does not replace the earlier protection. Sansec reproduced four code-execution routes within 24 hours.
1
3
5/5 No exploitation was observed at disclosure. Waiting for attacks is the wrong trigger. Patch now. Verify both fixes. Inspect template/email activity, hunt new PHP files or processes, and rotate secrets if compromise is suspected. Source: Sansec / Adobe #Magento #AppSec
2
Hackers used stolen ConnectWise credentials to access 173 Microsoft 365 tenants via MSPs. Enforce least privilege and MFA on MSP tools to block these attacks. #ConnectWise #Microsoft365 #MSP #SOCMinute
1
68
Check out Episode 14 of the SOC Minute Weekly Podcast, now on Spotify! open.spotify.com/episode/1iz…
1
1
6
Attackers intermittently tampered with AOMEI Backupper update servers, delivering a backdoor to Windows systems updating between May and July 2026. Security teams must monitor update-related activity closely. #SupplyChainAttack #SOCMinute #BackupSecurity
1
20
NIST, NSA, and CISA release core practices guiding organizations on incident readiness for super intelligence agents. Align your response strategies today to manage emerging AI risks. #IncidentResponse #SuperIntelligence #NIST #NSA #CISA
1
12
APT group UAT-11985 uses fake Google invites in an AitM phishing attack targeting Taiwan research orgs, bypassing MFA protections. Security teams: verify unexpected invites and monitor for unusual logins. #Phishing #APT #SOCMinute
1
1
136
1/5 BeyondTrust Remote Support is designed to broker privileged access. ARMORY CASTLE turned it into an entry point. CVE-2026-102764 was exploited as a zero-day to upload files, establish persistence and reach downstream systems. Here is the observed chain. 🧵
1
1
73
4/5 Patch status: • SaaS instances were patched automatically • Self-hosted 24.3.1-26.2.3: apply BT26-05-RS • Older than 24.3.1: upgrade, then patch An upgrade closes the flaw. It does not determine whether an exposed appliance was already compromised.
1
3
5/5 Hunt beyond the appliance. The actor deleted local logs and used admin access to reach downstream systems. Preserve syslog, WAF and firewall records. Rotate brokered credentials, review Jump Item permissions and rebuild suspect appliances. Source: BeyondTrust / Mandiant
5
Hackers hijack D-Link and Ubiquiti routers to resell stolen bandwidth via proxyjacking. Monitor your device traffic and keep firmware updated to block unauthorized proxy use. #Proxyjacking #NetworkSecurity #DLink #Ubiquiti #SOCMinute
1
30
Critical PwnEscape Linux kernel vulnerability (CVE-2026-99999) lets guest VMs read host memory, risking sensitive data in cloud environments. Immediate kernel updates and host-guest isolation reviews are essential. Stay secure! #LinuxSecurity #CloudSecurity #PwnEscape
1
193
3/5 Administrators reported attacks dating to September 10. Observed activity included PHP web shells and searches for password databases, password-manager artifacts and cryptocurrency wallets. Reports linking the flaw to ransomware remain unconfirmed.
1
1
11
4/5 Update richdocumentscode to 26.4.303 or later or remove it. Disabling the app is not enough. Nextcloud 29 and older cannot install the fixed release: upgrade Nextcloud or remove the app. The earlier CVE-2025-66208 fix does not address this path.
1
21
5/5 After updating, review proxy.php traffic, new PHP files, web-server child processes, outbound connections and access to credentials. If compromise is found, rotate exposed secrets. Source: Collabora / BleepingComputer #Nextcloud #Cybersecurity
4