

Insights from the Digital Forensics/Incident Response and Threat Research Team at SECUINFRA. We regularly publish reports, detection rules and other findings!
Berlin & Frankfurt am Main, DE
Joined April 2021
- Tweets431
- Following87
- Followers3.2K
- Likes142





Pinned Tweet
🚨Malware distributed via Steam
Fancy a bit of after work gaming? Beware of infostealer malware distributed via the Steam store!
Using @steamdb we managed to visually identify a very suspicious file in the game files. Luckily, we managed to retrieve a sample for analysis, which will follow in this thread.


Greetings from the Virus Bulletin Conference 2025 in Berlin, Germany 🇩🇪
We are looking forward to interesting presentations on the global cyber threat landscape and discussions with industry colleagues!


🎟️ 🛫 Check-in services disrupted at multiple airports
According to Reuters the European Union Agency for Cybersecurity (ENISA) confirmed that the outage is related to a #Ransomware attack on systems operated by Collins Aerospace / ARINC [1].
1/4 🧵

The independent researcher Kevin Beaumont found out that the outage is still ongoing. Apparrently affected systems were restored from backups, but the threat actors retained access and encrypted additional systems [3]. This indicates that the containment and eradication steps during the incident response process were not completed successfully the first time around. It is likely that the threat actors established a persistent way of accessing the internal network.
3/4🧵

Sources and Links:
[1] Reuters News coverage reuters.com/business/aerospa…
[2] Our slides about BianLian's TTPs github.com/SIFalcon/research…
[3] Kevin Beaumont's thread cyberplace.social/@GossiTheD…
4/4🧵
We are gladly supporting our local BSides conference in Frankfurt am Main, Germany 🇩🇪 again this year! You can look forward to two days of interesting workshops and presentations 🎙️
There are still a couple of seats left for our workshop on Windows forensics, grab them while you can 🧑💻
bsidesfrankfurt.org/workshop…


Proud to partner with @SI_FalconTeam for a 2nd year running as Silver sponsor! Plus they give a workshop too! Thank you, @SI_FalconTeam ! secuinfra.com/de/
📰 🚨 New blog post!
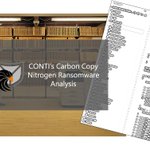
Sometimes we stumble upon malware that looks new on the surface, but suddenly feels very familiar during the deep dive analysis. This was the case in our recent analysis of Nitrogen Ransomware that we conducted together with our Security Research Intern Leon! Below you can find our writeup including the malware analysis as well as IoC and detection rules.
🔗 secuinfra.com/en/techtalk/co…

„Goedeavond“ from The Hague 👋 Today we attended the Hague Threat Intel Exchange (#haguetix), featuring talks about nation state and cybercrime threats. Thank you for the great presentations and conversations afterwards.


🚨 🇩🇪 Fast spreading Multi-Factor-Authentication Phishing campaign
We have observed multiple phishing incidents, primarily with German customers, that affect users enrolled with Multi-Factor Authentication. This type of an attack is also commonly referred to as Attacker-in-the-Middle (AitM) Phishing.

Prevention
The following measures can be used to detect or prevent this attack path:
- Implementing Conditional Access for the M365 environment. Access is only granted after verification of certain connection or device details. Specific Microsoft licensing is required.
- Using phishing-resistant 2FA methods such as FIDO 2 security keys, passkeys, Windows Hello for Business etc.
- Implementing e-mail filtering and analysis services, web filtering through proxy solutions.
-Raising the awareness of employees for this attack vector through appropriate training.
Indicators of Compromise #IoC
pweprarteasamesil[.]biz
bldsosinveppaversnty[.]biz
SECUINFRA FALCON TEAM retweeted

Today, I'll be speaking at @RVAsec about macOS internals! If you're interested, stop by 🍏
@SI_FalconTeam #InfoSec

ALT RVAsec presentation 50 minutes June 4th
SECUINFRA FALCON TEAM retweeted
Looking forward to speaking at @THOTCON about macOS and Linux internals! Come say hi if you're around today 🐧
@SI_FalconTeam
#InfoSec #THOTCON

ALT THOTCON in ASCII art text
SECUINFRA FALCON TEAM retweeted
Hey everyone! I will be speaking at @THOTCON about macOS and Linux internals! Say hi if you're around 👋
@SI_FalconTeam
#InfoSec #THOTCON
☑️#ClickFix / Fake Captchas posing as Cloudflare Verification pages
We stumbled upon a web page that closely resembles Cloudfare's Anti-DoS Verification pages. Upon clicking the verification button, the familiar ClickFix verification dialogue is presented.
1/7🧵
We identified this malware as #HijackLoader, with the final payload being Arechclient2 RAT. This combination has been previously observed by @redcanary here: xitter.cf/redcanary/status/19154…
A complete analysis of HijackLoader is beyond the scope of this thread, but stay tuned for long-form content 👀
6/7🧵

Last month we noticed a surprising payload combination in some paste and run (aka ClickFix and fakeCAPTCHA) campaigns: HijackLoader dropping the Arechclient2 RAT. 🐀
💡 Learn more about Arechclient2 and the rest of the month's top 10 threats in our April Intelligence Insights: bit.ly/4481vUx
🎬 Watch the full video of @techieStef's appearance on this week's Office Hours here: bit.ly/3j3DCmw
Last but not least, here are some #IoC:
URLs
clients.contology[.]com/captcha/
koonenmagaziner[.]click/smash/clock
gutenortherad[.]click/mountains/fairy
Files
crys. zip = 5d6be6cc3fb6f8c4c5d1b5f2eb399b74
Crysta_X64.exe = ff254c1778aefe5af06889f1f999dee3
DivXDownloadManager.dll = deb5bd989c9fdd5fe7f78f00a1216eb0
Heeschamjiet.rc = 2d4fdba00b7f7b02408a8ea6c199037e
Shonomteak.bxi = e43ec4f0aa69a344fcb8431e60195f0f
msvcp80.dll = 272a9e637adcaf30b34ea184f4852836
msvcr80.dll = 43143abb001d4211fab627c136124a44
7/7🧵