

D&D, fantasy, & tea hoarder #vtuber item asset & background design artist for @rainbowvtuber visual novel Rainbow: Heart of Chroma [email protected]
Joined April 2021
- Tweets3.1K
- Following730
- Followers141
- Likes52.1K




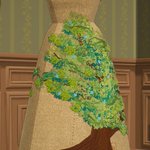


Adora's coronation dress is still one of the best dresses i've made, but i also made a VERY scuffed dress for Dorothy's Alien abduction commision.
Anyway here is her target dress 🤣🤣🤣
(with proof that i used EVERY fabric in her requirements lmao)


Seraph ✨🐉 | VSmarties retweeted

I reshared this last night, but I cannot stress enough, do NOT click any links that come into your emails. Don't trust any phone calls, emails, texts you recieve. Only interact directly through the website portals/apps externally.
Read more below about what's going on. It's BAD

This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS (In a typical year, these would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea

Seraph ✨🐉 | VSmarties retweeted

🚨【続報】Googleアカウント乗っ取り疑惑の正体が判明
先日ポストした、Google公式アドレスから「2日後にアカウントの復旧情報が変更される」という不審なメールが届いた件
結論から言うと、Googleの正規メール送信機能を悪用したフィッシング詐欺
2日経過した現在も問題なく使用できています
仕組み⏬️
① 攻撃者が自分のGoogleアカウントで
「個人情報 → メール → 連絡先メールアドレス → 別のメールアドレスを追加」
を操作し、標的のGmailアドレスを入力する
② Googleが標的のアドレスに確認メールを送信する
そのため、送信元は本物の
[email protected]
DKIM署名もGoogleの正規ドメイン
つまり、メールの送信元を確認しても本物に見える
③ メール本文には、別のロシアのメールアドレスが登録され、2日後にアカウントの復旧情報が変更されるという警告が記載されている
受信者が焦って取り消そうとするのが狙い
④ 最大の罠
取り消し用として記載されたURLには、Googleの公式サイトに見える文字列が含まれている
例えば
"https://[email protected]/..."
この "googIe" の「I」は小文字のLではなく、大文字のi
さらにURLの "@" より前は、アクセス先のホスト名ではない
見た目だけで判断すると騙される可能性あり
また昨今では通常の英字とよく似た別の文字
а(キリル文字)
о(キリル文字)
е(キリル文字)
с(キリル文字)
р(キリル文字)
見た目はほぼ同じでも、内部的には別の文字を使う手法も増えている
⑤ 偽のログイン画面に誘導し、Googleアカウントのパスワードを入力させて盗み取るという手口
つまり、Googleの本人確認が突破されたのではなく、本物のGoogle通知を利用して、偽の緊急事態を演出している
「Google公式アドレスから届いた」
「DKIM認証が通っている」
だけでは、メール本文の内容やリンクまで安全とは限らないということに注意が必要というこれまでのフィッシングよりも高度化している
不審なGoogle通知が届いても、メール内のリンクからログインせず、Googleアカウントの設定画面に直接アクセスして確認することをおすすめする
同様のメールを受け取った方はご注意を⚠️

🚨【注意喚起】Googleアカウントが乗っ取られる可能性のある不審な復旧申請が発生
本日、Googleからかなり怖いメールが届いた
内容を簡単にまとめると、
「Googleサポートによる本人確認が完了しました。2日間の猶予期間後、パスワードと既存の復旧手段が削除されます」
というもの。
当然、私は復旧申請などしていない。
調べてみると👇
① YouTube Partner Program(Enterprise Support)経由でGoogleアカウントの復旧申請が行われたと記載
② Google Accounts Teamに引き継がれたとのこと
③ 本人確認は既に完了したと通知
④ 2日間の猶予期間後、第三者のメールアドレスにパスワード変更の案内が送られるという内容
⑤ 現在のパスワードと復旧手段は削除されるとのこと
しかも、指定されていた連絡先はロシアの「mail.ru」ドメイン。
メールの送信元は
[email protected]
さらにGmailで確認したところ、
送信元:idverification.bounces.googl…
署名元:accounts.google.com
Googleの正規ドメインによる認証が確認できた。
単純な送信元偽装メールとは考えにくいが、通知内容の真正性や復旧申請の進行状況は現在確認中。
ちなみに、私のYouTubeチャンネルは収益化していない。
にもかかわらず、YouTube Partner ProgramのEnterprise Support経由で本人確認が完了したと記載されているのが謎…
現時点ではGoogleアカウントに正常にログインできているが、メールの内容が事実なら、パスワード変更だけでは防げない可能性もある。
Googleアカウントを利用している人は、身に覚えのない復旧申請やセキュリティ通知が届いていないか確認してほしい。
同様のメールを受け取った人や、Googleサポート経由のアカウント復旧に詳しい人がいたら情報をいただきたい。
進展があれば追記します。


Seraph ✨🐉 | VSmarties retweeted

If you can't find a good reference, you can make your own!!
It's quite fun when you get used to it 🌷


i delay stream for 30 minutes waiting for maintinence to show up (fire alarm check), they don't show, and RIGHT as i am about to start the game THEN they start bangin on the front door -3-
but hey if anyone wants to watch me suffer through RE2 i'll be over here 😭📷 (i hate playing horror games waaaaahhhhhh)
twitch.tv/seraphblade25

When work wears you out so much you just sit there staring at your screen wanting to relax but genuinely being too tried to move and your brain feels like empty static 🫠🫠🫠

Seraph ✨🐉 | VSmarties retweeted

Checkt mal euren NVidia Treiber.
Die Hurensöhne haben mit dem letzten Patch eine Funktion hinzugefügt, dass AI Agents einfach Zugriff auf euren PC haben 🤡🤡🤡
Das ist PER DEFAULT An.
Macht das schleunigst aus!

plaed a new game today called Death's Door and OMG its such a cute game! you play as a crow reaper and its so cuuuuttteeeee
i titally didn't stay up until 2am playing dressmaker nooooooooooooooooooooooooooooooooooooooooooo
o3o
well, Dorothy in #Dressmaker wanted a dress that gets her picked up by aliens, so i made her a literal target dress 🤣🤣🤣
the pic below prooves i met all the requirements
