

Web3 security researcher & developer - Github: https://xitter.cf/t.co/fIKSA7D1aL - Audit resume: https://xitter.cf/t.co/SEafwgjjvX
on-chain
Joined June 2020
- Tweets464
- Following854
- Followers255
- Likes20K





Pinned Tweet
decided to make my page and resume more organized.
so i built a personal website, check it out here:
rsameth.xyz
it contains my resume and i also plan to release AI generated slop-ass articles (jk, it would be only interesting ones) in there + other security related features in the future.
you can see my contest achievements + other private works here:
rsameth.xyz/resume
github.com/rohallah12/audits
articles:
rsameth.xyz/articles
you can also sign-up with gmail or github and leave comments/votes.
Hacks will increase because of how strong the open-source models are becoming + cheaper token cost.
Like 1 year from now you could have your platform being scanned by thousands of basically free agents in real-time looking for exploits. Absolutely no room for security mistakes.
Some projects are just alive by miracle. Like when you read their code u ask yourself how the hell they made it this far without getting exploited .
Literally every single finding of glm 5.3 flash is invalidated totally by gpt astra. Shows that glm 5.3 flash just hallucinates too much. Astra saved me from aubmitting many ibcorrect reports claimed by glm
anybody knows what kind of agentic system @OpenAI used to solve Navier–Stokes problem? 88 hours and millions of $ spent on tokens is wild but what interests me is how the system could keep exploring genuinely new paths at that scale without drowning in context, or repeating itself or losing track of assumptions/results.

i have been working on a lot of unique ideas for my AI security auditor over the past few months. lots of great ideas, lots of drafts, lots of different implementations. as a result, i have spent little to no time doing bug bounties or security audits the way i used to.
i even had to dive deep into some complex math to design parts of it.
it's still a work in progress, but i have decided to replace the automated loop with myself for now. instead of code handling agent orchestration, job assignments, etc. i am doing that part manually.
i have come to the conclusion that it's totally possible to build a tool where more $ spent on tokens means more code explored and more vulnerabilities found. but the point is not just to spend more $. its to design the agentic system in a way so that the $ goes toward the more interesting parts AND youre covering more of the system as you spend more.
those are the hard problems i am currently working on.
we will see what happens
I am losing so much usage cause of openai random resets, i was suppose to use 80% in 2 days then get a reset, now i have to wait another week 😆

2) specifications, relationships, and behavior of the original system.
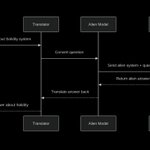
ask a question about the solidity system, an LLM would first translate the question into a corresponding question about the alien representation. that question and the alien version of the system would then...


fable 5 tells you straight up that they cant do the task because of cybersecurity risks, and thats fine honestly.
but gpt 5.6 interrupts you 100 times mid task with this warning.
like bro if you dont wanna do this then block my task from the begining so i dont waste tokens.

xitter.cf/claudeai/status/207830…
the model is basically useless with all the dumb cybersecurity filters. even asking a very very abstract question about security is routed through opus 4.8 which isnt even on par with opensource models.
Its time to switch to gpt 5.6 sol

Beginning July 20, Claude Fable 5 will be included in all Max and Team Premium plans, at 50% of limits.
Pro and Team Standard users will continue to have access to Fable via usage credits, and will receive a one-time $100 credit.
Demand for Fable has been challenging to predict, which is why we rolled it out to subscription plans in stages, extending access several times as we secured additional capacity.