

find me a critical vulnerability, make no mistakes.
Joined September 2015
- Tweets370
- Following269
- Followers1.9K
- Likes1.1K




Liked PHP2Shell? You’re gonna love Node2Shell.
We reproduced CVE-2026-111497 as pre-auth RCE. On a vulnerable Node.js runtime, app.use(express.json()) is enough to expose your server to code execution through a single Brotli request. Patch your systems now!
imperva.com/blog/node2shell-…

docker cp container:/etc/hosts ./hosts.txt
That’s all it took for a malicious container to escape.
Meet CVE-2026-17106 aka CopyEscape: a container-to-host arbitrary file-write vulnerability leading to code execution outside the container.
imperva.com/blog/copyescape-…

Ron Masas retweeted

A very interesting data point on whether distillation gives you a competitive advantage. Sonnet 5 is just objectively worse than GLM 5.2, and is likely around a similar size. Sonnet 5 was almost certainly distilled (and not just distilled from tokens, but proper distillation from logits) from Mythos. This should give you an update on how relatively unimportant distillation is, in particular for the Chinese labs. It's just a way to warmstart the model for RL; the American frontier labs do it with human data, Chinese do it with tokens from American models, but they could get to basically exactly the same model without it, it would just be a little bit more expensive and require more human data collection coordination/aggregation
Ron Masas retweeted

Microsoft ranked me #6 in the world on the 2026 MSRC Most Valuable Researchers list.
#3 Azure · #3 Azure DevOps · #7 Dynamics & Power Platform
My unfair advantage: autonomous AI agents I built, hunting alongside me.
Offensive security now runs at machine speed.

Today, we're proud to recognize the Top 100 Microsoft 2026 Most Valuable Researchers (MVRs).
Security researchers play a critical role in helping protect customers by identifying and reporting vulnerabilities across Microsoft products and services. We're grateful for their partnership and the impact they have made over the past year.
Congratulations to this year's Top 10 MVRs:
🥇C46F3708A45EF0041BD0A49DDAEA0E25
🥈ShinHyuiq & Alan Pang
🥉cherrypick
4. Brad Schlintz (@nmdhkr)
5. wtm (@wtm_offensi)
6. Asaf Cohen (XBREACH.AI)
7. bccc95a61a3cc79d7b2c4423c808f744
8. Felix B.
9. 142a423e2574abf10d65eba46891ca5e
9. Anonymous
This year, we updated the MVR leaderboard to rank researchers based on total bounty awards, creating a clearer connection between recognition and security impact. We also introduced Special Mentions to recognize researchers who submitted valid vulnerability reports during the recognition period, regardless of leaderboard ranking.
See our blog for the complete list of the Top 100 MSRC 2026 Most Valuable Researchers and the top researchers by bounty program: microsoft.com/en-us/msrc/blo…
Thank you to every researcher who partnered with us this year to help protect customers worldwide.

ALT Microsoft 2026 Most Valuable Researchers (MVRs)

I recently got access to OpenAI’s Trusted Access for Cyber program.
With all the GPT-5.5 hype and the Anthropic Mythos discussion, I wanted to test it for myself.
The result: **GPT-5.4** helped identify and develop a working Safari exploit affecting all Apple devices.
It found a JSC WebAssembly use-after-free that gave us stale read/write access inside the Primitive Gigacage. Then it spotted a bug in Safari’s Fetch implementation where in-flight opaque cross-origin responses could be materialized inside renderer memory.
By combining the two, a malicious page could steal authenticated cross-origin data and completely defeat the Same-Origin Policy.

The best security research starts where someone else's ended. Remember React2Shell? @SillamYohann picked up where it left off and found CVE-2026-23869, a single HTTP request that can freeze your React server for minutes.
Here's how. 🧵
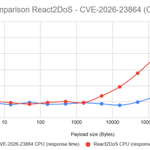
How does it compare to CVE-2026-23864? That one needed a 1MB payload to stall the server for seconds. React2DoS achieves minutes of computation with tens of kilobytes.


Ron Masas retweeted

I got a 1T (trillion) parameter model running on my MacBook Pro.
Kimi-K2. 1.029T params.
~1 TB raw weights.
524 GB converted.
~1.7 tok/s.
Yesterday it was 671B. Today it's 1T.
Same laptop. Same M4 Max. No cloud.
When I say we: I mean Claude and me.

