

Rob retweeted

lol whole new calling conventions for PIC literally a day after I release my kit 😅 aff-wg.org/2025/10/13/weedin…
Rob retweeted
[Crystal Kit]
Evasion kit for Cobalt Strike.
github.com/rasta-mouse/Cryst…

Rob retweeted

New blog from me on using CLR customizations to improve the OPSEC of your .NET execution harness. This includes a novel AMSI bypass that I identified in 2023. By taking control of CLR assembly loads, we can load assemblies from memory with no AMSI scan. securityintelligence.com/x-f…

Rob retweeted

I've been getting questions about this again recently, so I wrote a small post. Patching .NET functions from an unmanaged CLR harness: outflank.nl/blog/2024/02/01/…

Rob retweeted

We just released Reflective Call Stack Detections and Evasions! This was co-authored by our @XForce Red intern Dylan Tran @d_tranman! Dylan is wicked smart and it was fun working with him! Check it out!🥷
securityintelligence.com/x-f…

Rob retweeted

New blogpost by @0vercl0k: "Competing in Pwn2Own ICS 2022 Miami: Exploiting a zero click remote memory corruption in ICONICS Genesis64" doar-e.github.io/blog/2023/0…
Rob retweeted

Wrote a blog post for my company on how we implement obfuscation for our C# post-exploitation arsenal. Discussing some detection opportunities and our ways around them. Special thx to @Flangvik for his video on SharpCollection, which is our pipelines base
r-tec.net/r-tec-blog-net-ass…
Rob retweeted
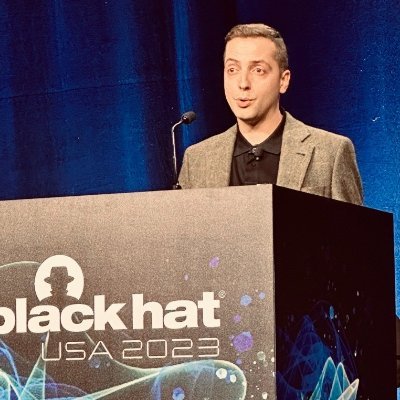
I have posted the slides for the #BlackHat talk @chompie1337 and I gave yesterday -> Close encounters of the advanced persistent kind: Leveraging rootkits for post-exploitation
github.com/FuzzySecurity/BHU…

Rob retweeted

Lo prometido es deuda, el research sobre el CVE-2023-28252 ya esta publicado con su PoC junto a la explicacion detallada del reversing que hicimos con mi amigo @solidclt.
github.com/fortra/CVE-2023-2…
Mas dificil que barrer escaleras para arriba.
Ojala les sirva.

Rob retweeted
Short write-up on baby's first UAF challenge h0mbre.github.io/PAWNYABLE_U…. Post is meant to serve more as an advertisement for pawnyable.cafe/linux-kernel/. It was a great resource for me to get started on Linux Kernel exploitation. Also I need a new blog layout yikes
Rob retweeted

Today I am finally releasing a new 3-part browser exploitation series on Chrome! This was written to help beginners break into the browser exploitation field.
Part 1 covers V8 internals such as objects, properties, and memory optimizations. Enjoy! jhalon.github.io/chrome-brow…
Rob retweeted

a beautiful write-up : CVE-2022-1786 A Journey to the Dawn blog.kylebot.net/2022/10/16/…

Rob retweeted

This is probably the most complex exploit I've done so far. A UAF in Android kernel freed by kfree_rcu (introduces a delay) in a tight race + kCFI + Samsung RKP. Yet its still possible to gain arbitrary kernel RW, disable SE and root from untrusted app. github.blog/2022-06-16-the-a…

Rob retweeted

Up your security research skills: This Windows LoadLibrary port for Linux by @taviso is a great project to contribute to. You'll learn how *both* OS's work internally. Use it to fuzz Win binaries faster on Linux
github.com/taviso/loadlibrar…

Rob retweeted

Do you want to learn how to find vulnerabilities in Google Chrome? @Nosoynadiemas just released the last exercise of Fuzzing101! github.co/3s8m12H

Rob retweeted

I just released more details about the recent Samba (pwn2own) vulnerability. #CVE-2021-44142.
as hot 🔥 as still being reserved on Mitre. 🙃
writeup: 0xsha.io/blog/a-samba-horror…
PoC (level-0) : gist.github.com/0xsha/085903… 1/2
Rob retweeted

Here are the slides from the "Attacking JavaScript Engines in 2022" talk by @itszn13 and myself @offensive_con. It's a high-level talk about JS, JIT, various bug classes, and typical exploitation flows but with lots of references for further digging! saelo.github.io/presentation…
Rob retweeted

Check my first blog about alternative process injection without allocating new memory to bypass EDR.
netero1010-securitylab.com/e…
Rob retweeted

Morning!
Just pushed a new blog post that's intended to be the first in a series using LibAFL to solve Fuzzing101 exercises. I've been wanting to dig in to LibAFL for awhile and learning the library "in the open" seemed like a fun idea.
epi052.gitlab.io/notes-to-se…
Rob retweeted

SecureAuth #Impacket 0.9.24 is now available. Discover the new features including ways to dig deeper into #ADCS, a more hardened #SMB server and delegation features. Read the blog by @0xdeaddood: ow.ly/ZB4550GzycC #offensivehacking