
Researcher at @CNRS in the @SpiralsTeam. Browser fingerprinting, web privacy and security, software engineering. Creator of https://xitter.cf/t.co/zA4XAvkjiH.
Lille, France
Joined January 2018
- Tweets253
- Following320
- Followers390
- Likes1.8K




Ca fait trois ans que je suis de loin la technologie Utiq. La CNIL a bien évidemment donné son accord à l'époque car on touche directement à la vie privée des utilisateurs avec les opérateurs et il fallait des arguments forts pour convaincre que ça allait être ok avec le RGPD.

C'est juste totalement contraire à la lettre et à l'esprit du RGPD, et effectivement que la @CNIL n'en dise pas un mot est pour le moins problématique. Mais vu qu'elle a déjà abandonné l'idée de combattre les cookiewalls assortis d'un paywall... Il n'y a hélas plus rien à espérer
Le cookie de consentement est passé de 3 à 6 mois de validité et tous les opérateurs français ont ajouté le support de leur box Internet depuis 1 an (consenthub.utiq.com/pages/pr…), ce qui change complètement la donne en terme de tracking par rapport à un avis de la CNIL d'il y a 3 ans
Happy to announce that we have a 2-year postdoc position on web security and online tracking available in our team! Contact me directly if interested.
📍Where: Lille, France
⌛ Duration: 24 months
📅 Start date: September 2026
👉 More information: recrutement.inria.fr/public/…
AmIUnique is starting a new adventure on mobile! 🎉📱
We have just launched our first Android application to study if users can be identified through an application without using a single permission.
Link: play.google.com/store/apps/d…
Retweets are greatly appreciated 😊

When you launch AmIUnique and tap "Scan my device", the application will collect your device fingerprint and display a selection of key attributes. Our goal is to analyse all the fingerprints we will receive to understand if the way Android is built can pose a privacy problem.


This application is a first step to investigate the fingerprintability of the mobile ecosystem. We plan on releasing another app similar to the AmIUnique.org website where you will be able to see how your own fingerprint compares to all the other collected fingerprints.
Pierre Laperdrix retweeted

I'm looking for a postdoctoral/research associate to join my group at @NYUAbuDhabi in sunny Abu Dhabi! ☀️🏖️💻
Postdoc application: apply.interfolio.com/156376
Don't have a PhD? Apply to be a research associate: apply.interfolio.com/156377
Three good reasons to apply: 1/2
Pierre Laperdrix retweeted

After several success iterations of SecWeb, @stecalzavara and I have decided that it's best for the Web community to merge with MADWeb, as we want to avoid fragmenting the community. So, please consider submitting to madweb.work/ (weather is nicer in San Diego ;-))
Google won't deprecate third-party cookies after all. This seems to be the worst outcome for me as heavy investment has been made in the past four years to develop alternatives that will now work alongside existing 3P cookies. Tracking will be more present on the web as a result.

After much back and forth, Google has decided to keep third-party cookies in its Chrome browser. Turns out all the fuss over the years wasn’t in vain after all; the ad industry’s cries have finally been heard. buff.ly/4ffRQyw

Our paper on Server-side tracking will be presented by @Fouad__Imane at #PETS2024 on Thursday! Come say hi to her to know more! Unfortunately, I had to cancel my trip at the last minute 😢

I'm super happy to announce that our paper on server-side tracking (SST) made with @Fouad__Imane and @Cristianapt was accepted at PETS!
"The Devil is in the Details: Detection, Measurement and
Lawfulness of Server-Side Tracking on the Web"
PDF hal.science/hal-04617727v1/d…
More info 🧵

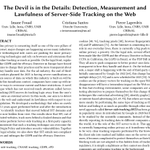
ALT Screenshot of the first page of our paper "The Devil is in the Details: Detection, Measurement and Lawfulness of Server-Side Tracking on the Web" published at PETS'24
For this study, we focused on detecting a small subset of SST servers. We relied on different crawls made in 2020 and 2022 to detect websites that shifted from the traditional tracking model to the server-side tracking one and found some websites that operated that change.

ALT Figure presenting our methodology with three different crawls. We crawled the Alexa top 10k in March 2020 and May 2022 to detect trackers that shifted to the server side.
The second problem is about the responsibilities and liabilities of the different actors in the data collection. Now that there is an additional intermediary server in the mix, who is responsible and liable for that? How can users exercise their rights to access their data?
I'm super happy to announce that our paper on server-side tracking (SST) made with @Fouad__Imane and @Cristianapt was accepted at PETS!
"The Devil is in the Details: Detection, Measurement and
Lawfulness of Server-Side Tracking on the Web"
PDF hal.science/hal-04617727v1/d…
More info 🧵
ALT Screenshot of the first page of our paper "The Devil is in the Details: Detection, Measurement and Lawfulness of Server-Side Tracking on the Web" published at PETS'24
On top of that, most of these intermediary servers are hidden as a first-party ressource through techniques like CNAME cloaking so that they can bypass ad blockers and not be affected by the upcoming third-party cookie depreciation. In short, it is a perfect privacy nightmare.
