

Find it. Fix it. Prove it. Vulnerability management and cyber automation for SMBs, MSPs and enterprise teams. Start free at https://xitter.cf/t.co/2WjcaDdDWP 🚀
London, England
Joined August 2018
- Tweets1K
- Following350
- Followers776
- Likes290





Pinned Tweet
#CyberSecurity breaches can be devastating to anyone, especially Not-for-Profits that may not have big enterprise budgets. We have put together a list of some top FREE cybersecurity tools every #NFP should consider. A thread. 1/10
In case you missed it, another round of RoboShadow updates went live last week!
This release brought seven new additions to the platform, with a particular focus on making life a little easier for MSPs managing multiple organisations, improving automation and making reporting more useful.
Here's what's new:
🔹 Tenancy Vulnerability Reporting: An expanded view of antivirus, OS updates, data/disks, hardware, and software across all your organisations.
🔹 Tenancy-Level Device Groups: Group devices across different organisations in one place.
🔹 Auto-Install Rules in AI AutoFix: Automatically install approved software across your estate using rules.
🔹 One-Click Update Improvements: A tidier interface with General and Advanced settings.
🔹 Windows Updates: Restart Options: More control over when devices restart after updates.
🔹 Custom DORA SLAs: Set remediation timeframes that reflect your own requirements.
🔹 Executive Summary Report: A clearer, more accessible overview of your estate for leadership and board reporting.
They're all available to explore in the portal now, with Tenancy Vulnerability Reporting and Auto-Install currently under Experimental Features.
The full release blog covers everything in more detail, including short walkthrough videos to help you get started. 😊
🔗 eu1.hubs.ly/H0z4S630
#RoboShadow #CyberSecurity #MSP #VulnerabilityManagement #Automation

Only 4 days to go until Pax8 Beyond EMEA in Copenhagen!
Terry, Liz, Kristers and Rob will be there from 18–20 October at Booth #304, and we're really looking forward to catching up with familiar faces, meeting some new ones and hearing what everyone has been up to 😊
There are a few conversations on the agenda we're particularly looking forward to:
🔹 AI and the future of the MSP: With agentic AI taking centre stage, we're interested in how MSPs are embracing the opportunities while navigating the security challenges.
🔹 Cybersecurity and business growth: How MSPs can strengthen their security offerings, create more value for customers and build sustainable revenue streams.
🔹 Automation and working smarter: A topic close to our hearts! Especially how MSPs can reduce manual work, improve efficiency and free up more time to focus on their customers.
If you're coming along, do pop by Booth #304, whether you'd like to see RoboShadow in action, have a chat about cybersecurity or simply stop by to say hello and grab some merch, we're looking forward to seeing you.
#Pax8Beyond #Beyond26 #MSP #Cybersecurity #Pax8Copenhagen #RoboShadow

As promised, we're keeping the releases coming, and last week's headline feature was our new Patching Compliance Report (Beta) for anyone reporting against Cyber Essentials or DORA. A lot of what's in this one came straight from your feedback, so a big thank you to everyone sending ideas our way.
Here's a quick look at what's new in the portal:
🔷 Patching Compliance Report (Beta): see which vulnerabilities are still within their remediation deadline and which have slipped past it.
🔷 Compile Full Report (Experimental): every vulnerability type across every device, in one Excel workbook.
🔷 Automatic PSA Remediation: If an app has an AutoFix rule, tickets are held back unless AutoFix has failed a set number of times.
🔷 Bulk Service Actions: start, stop or restart several Windows services in one go.
🔷 Clearer Patch Levels: Added OS revision (UBR) tracking, so machines on the same build but different cumulative updates are now shown separately.
🔷 A redesigned Licence and Billing area, plus a handful of quality of life updates.
You'll find more on these in the blog, which includes step-by-step guidance for each feature 😊
🔗 Read the full release here: eu1.hubs.ly/H0ySrx90
#CyberSecurity #MSP #CyberEssentials #DORA #PatchManagement #RoboShadow

For anyone who missed it, we announced our largest release last week, after a summer of building, testing and tidying, with three completely new products now opening up for early access:
🔷 AI Pentest Agent - running real exploitation attempts across networks, code and cloud environments to find out how an attacker could actually get in.
🔷 Microsoft Sentinel (SIEM & SOC) - making another important layer of security more accessible for internal IT teams and MSPs.
🔷 App Manager - a zero-trust approach to understanding and controlling the apps, packages and tools running across an estate.
There's a lot more in this release, all covered in our blog:
🔗 eu1.hubs.ly/H0yNwWv0
Vulnerability coverage has been expanded further with eight new elements that are available to test through our App Bounty, several features out of Beta and Experimental, and a refreshed RoboShadow interface that we'll be rolling out gradually 😊
#CyberSecurity #VulnerabilityManagement #MSP #Pentesting #SIEMSOC #RoboShadow

📣 If your organisation has been hit by a cyberattack, our team will help you get through it, for free.
Attacks are increasing, and AI is changing the shape of what's coming at businesses and MSPs alike. Security by obscurity isn't holding up as a strategy anymore, and when an incident does happen, the clean-up can be just as stressful as the attack itself.
So here's what we're offering to the whole market:
🔹If you've experienced a cyber incident, get in touch with our team with some evidence of what happened.
🔹We'll get you access to the full version of RoboShadow across your entire environment, free of charge.
From there we'll run a complete audit and fix as much as the platform can resolve automatically, which for most organisations covers somewhere between 60 and 90% of what's found. Anything we can't fix automatically, like firewall port changes, gets raised as a ticket straight into your service system.
It doesn't matter how big your organisation is or whether you can pay for it afterwards. Once you've confirmed the clean-up is done, we'll remove the licences, and we'll give you a sensible 48 hours to do that rather than chasing you for it.
If you've been hit, get in touch with the team by emailing us at [email protected].
#CyberSecurity #MSP #RoboShadow #VulnerabilityManagement #CyberAttack #AI
⚡Microsoft's September Patch Tuesday became the largest release in its history.
900+ vulnerabilities addressed, 113 of them rated Critical, and two zero-days that were already being exploited before patches arrived.
With a release this size, prioritisation matters more than ever. We broke down what needs attention first, and why a record-breaking number doesn't automatically mean record-breaking risk.
Read the full breakdown: eu1.hubs.ly/H0yd9v80
#PatchTuesday #CyberSecurity #VulnerabilityManagement #CVE #MSP #RoboShadow #Microsoft

We’re excited to share that RoboShadow will be at #Pax8Beyond in Copenhagen from 18 to 20 October!
Come and find us at booth 304 to meet Terry, Liz and Kristers, discover how RoboShadow helps MSPs simplify Cyber Security and, as always, be in with a chance of winning some brilliant LEGO sets! 😊
The agenda looks seriously good, with more than 70 hours of content spanning AI, Cyber Security, MSP growth and operational efficiency.
From asking what happens when AI stops playing by the rules, to exploring what AI agents really mean for SMB customers and whether we’re ready for Cyber Security in 2030, there is so much we’re looking forward to.
Are you attending? Which session is already at the top of your list?
📍 Bella Center, Copenhagen
📅 18 to 20 OctobIer
📌 Booth 304
#Pax8 #Pax8Beyond26 #RoboShadow #CyberSecurity #MSP #MSPCommunity #VulnerabilityManagement #AI #Automation

A lot of "free" cybersecurity is a login page and a button that says "book a demo to see pricing". Ours is a proper internal and external overview of your attack surface, running in minutes.
Here's what you get with us, all at no cost:
💠External Scanner, 1000 ports, manual
💠LAN Scanner, 1000 hosts, manual
💠Web App Scanner, OWASP checks, manual
💠Device Agents, one daily update
💠365 and AD Sync for device coverage
💠MFA Compliance read straight from Microsoft 365
💠Domain Enumeration, manual
💠SSL Scans, manual
💠Antimalware status from third party or Defender
💠Disk Encryption, BitLocker management
💠Prospecting for MSP health checks
💠Weekly Report of your vulnerability totals
💠Community Support by email
No card on file, no trial countdown, and Community stays free.
#CyberSecurity #RoboShadow #MSP #VulnerabilityManagement #VulnerabilityScanner #FreeCybersecurity

In case our last post didn't convince you already...
You can't protect what you don't know is exposed.
🚨 Case in point: you've probably already heard about Cl0p's latest run that's now hit 43 companies, including Shell, GE, and Philips.
A critical vulnerability was being actively exploited, patches were made available, and yet weeks later around 80 instances were still exposed to the internet...
That's the kind of gap we're here to help you close. Scan your external attack surface with RoboShadow completely free, with no card required, and see what someone looking at your organisation from the outside can see too.
Sign up here: eu1.hubs.ly/H0xN09w0
#CyberSecurity #AttackSurfaceManagement #VulnerabilityManagement #ExternalAttackSurface #MSP #RoboShadow
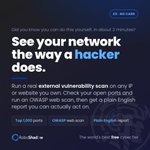
👩💻Point RoboShadow at any IP address or website you own and you'll get an external vulnerability scan back in a couple of minutes, for free.
You'll see your perimeter the way an attacker would from the outside, unauthenticated: open ports, plus an OWASP web-app scan.
We don't need you to install an agent, put in your credit card details, or get on a sales call with us, we just think that everyone should see their own attack surface. So this lives in our free tier, and it stays there.
Give it a go on your own domain and see what comes back! As always, we're here for you if you have any questions or need help with anything :)
#VulnerabilityManagement #CyberSecurity #ExternalVulnerabilityScanner #AttackSurface #OWASP #InfoSec

🌒In one of the biggest releases of the year, Microsoft's August Patch Tuesday addressed roughly 400 vulnerabilities, including 42 rated Critical and three zero-days - one of which was already being exploited before a patch existed.
We've broken it down for you in the blog and included what to prioritise this month:
🔗 eu1.hubs.ly/H0xCXRF0
#PatchTuesday #CyberSecurity #VulnerabilityManagement #MSP #RoboShadow #Microsoft

💡 As more organisations build their own applications and increasingly use AI to help write code, we have to think about how those applications are protected too.
Security by obscurity has never been a long-term strategy, and understanding what's happening inside your own environment is more important than ever.
🔗 Watch the full video on YouTube: eu1.hubs.ly/H0xqPtd0
#CyberSecurity #AI #ApplicationSecurity #SIEM #SOC #InformationSecurity #RoboShadow #VibeCoding
If an AI model is interacting with your environment, it's still making API calls, enumerating systems, requesting data and generating activity along the way. Those are exactly the kinds of patterns that SIEM and SOC capabilities are designed to detect.
As organisations adapt to increasingly capable AI, continuous monitoring is likely to become more important than ever. Fortunately, enterprise-grade SIEM and SOC services are also becoming much more accessible, giving organisations of all sizes more options than they've had in the past.
🔗 Watch the full video on YouTube: eu1.hubs.ly/H0xmBNw0
#CyberSecurity #AI #SIEM #SOC #CyberRisk #MSP #RoboShadow
After an interview at a GTIA event, someone came up to our CEO, Terry Lewis, and mentioned how hearing the discussion around new AI variants coming to the market had really reduced their anxiety around AI.
We think that says a lot about where we are at the moment. There are some very real advances happening, but there are also plenty of headlines that make it difficult to judge what deserves our attention and what should be taken with a pinch of salt.
One point to consider: AI is uncovering vulnerabilities at a pace that wasn't possible before, bringing long-standing security issues to the surface much faster than we've been used to. This presents new challenges, but also gives organisations the opportunity to identify and fix problems that may otherwise have remained hidden.
🔗 Watch the full video on YouTube: eu1.hubs.ly/H0xdStL0
#CyberSecurity #AI #CyberRisk #VulnerabilityManagement #InformationSecurity #MSP #RoboShadow
Lately it feels as though every conversation about AI starts with another headline or prediction about where everything is heading.
It can be hard to know what to pay attention to, especially when some of the discussion makes it sound like the rules have changed overnight. It's easy to assume the security landscape has suddenly become impossible to keep up with.
But the reality is more measured and nuanced than headlines suggest. In one of our recent videos, our CEO, Terry Lewis, speaks about Anthropic's Mythos models, where they fit into the wider AI landscape, and what organisations should realistically be thinking about as these tools become more capable.
🔗 Watch the full video on YouTube: eu1.hubs.ly/H0x8mHP0
If you're trying to make sense of all the noise around AI and cyber security, we think you'll find it useful 😊
#CyberSecurity #AI #CyberRisk #MSP #InformationSecurity #RoboShadow # Anthropic #Mythos
AI has already changed how vulnerabilities are discovered, and the next challenge is in keeping up with the volume.
Our CEO, Terry Lewis, touched on this in his conversation with GTIA - we're likely going to see a "tsunami" of CVEs as software vendors use AI to identify and fix security flaws at an unprecedented scale. Which is good news for improving software security, but it also creates a huge challenge: every newly discovered vulnerability still needs to be assessed, prioritised and patched.
For MSPs and security teams, effective vulnerability and patch management will become even more critical as the pace of discovery continues to accelerate.
If you're looking for a better way to stay ahead of these changes, or need support with anything, please do get in touch with us - the team are always ready and happy walk you through how RoboShadow can help 😊
#CyberSecurity #AI #VulnerabilityManagement #CVE #PatchManagement #DevSecOps #SoftwareSecurity #MSP #RoboShadow #GTIA #MSPShow
We're back with another clip from our interview with GTIA:
There's a lot of discussion around the security risks that come with AI, but it's worth remembering that AI still has to interact with the environments we already manage.
If an AI agent is interacting with your environment, it's making API calls, enumerating resources, changing configurations, and leaving activity behind - those are the kinds of activities SIEM and SOC platforms are designed to detect, giving security teams the visibility they need to respond.
A few years ago, building a mature SOC was out of reach for many organisations because of the cost. Today, with platforms like Microsoft Sentinel, Defender and the growing MSP ecosystem, those capabilities are becoming much more accessible.
As AI becomes part of day-to-day operations, security can't be something we bolt on afterwards. It needs to be part of how we build and deploy these systems from the start.
#CyberSecurity #ArtificialIntelligence #MicrosoftSecurity #SOC #ThreatDetection #DefenderXDR #SecurityOperations #MSP
🎉 RoboShadow Summer Release: Mac & Linux agents are now in public Beta.
Your estate isn't one operating system, so your security shouldn't be either. This release brings full vulnerability scanning and CVE matching to macOS and Linux, right alongside Windows, all from a single platform.
Here's what's now live:
💠 Mac & Linux agents (Beta): CVE scanning, hardware and software inventory, firewall and antivirus checks, and full Apple Silicon (ARM64) support. Qualys/Nessus-grade coverage, minus the cost and complexity.
💠 Smarter AutoFix: we now prioritise CISA KEV vulnerabilities (the ones actually being exploited in the wild) and added 365 CIS Benchmark remediation, so you fix what matters and skip the noise.
💠 AI App-Get: patching software that doesn't play nicely with WinGet, using AI-sourced packages.
💠 The usual housekeeping: external scanner scheduling down to the hour, User Applications on by default, CyberHeal uninstall fixes, and attachments on support tickets. Archived Devices and our MCP (Claude) integration are both out of Beta.
Read the blog in full (includes short video guides and a list of improvements & upcoming releases):
🔗 eu1.hubs.ly/H0wWQG_0
#CyberSecurity #MSP #VulnerabilityManagement #Linux #macOS #EndpointSecurity #RoboShadow

What’s the reality of being an MSP? Too many tools, not enough visibility, and threats moving faster than most teams can remediate. That’s why finding the right partner is more important than ever.
Our Founder and CEO, Terry Lewis, and Mostyn Thomas, Senior Director of Security EMEA at Pax8 sat down with Sophie Milburn at MSP Channel Insights to discuss trends and challenges for MSPs in 2026.
A few of the insights:
💡 Tool sprawl: “MSPs don't like paying for overlapping software, that’s why RoboShadow is supporting other platforms and functionalities,” said Terry.
💡 Shortening remediation windows: "Bad actors can spot vulnerabilities in hours. Time is not on our side, and RoboShadow’s automation is a huge leap for MSPs." Mostyn
💡 What MSPs need: “RoboShadow is enterprise quality, but at small business price. And that's precisely what MSPs need.” Mostyn
Watch the full interview here ➡️eu1.hubs.ly/H0wRLsP0
#RoboShadow #Pax8 #MSP#MSPCommunity #CyberSecurity #VulnerabilityManagement #Remediation #AI #Automation

Anthropic's most powerful AI model was jailbroken in days. Then the US government gave them under 90 minutes to pull it worldwide.
Here's where this differs from the usual "someone broke an LLM" story:
Mythos was positioned as one of the world's most capable AI models, from the company whose entire brand is built around AI safety. It still cracked incredibly quickly. Fortunately, it appears the vulnerability was discovered by a friendly researcher - but it raises the obvious question: what if it hadn't been?
Since we recorded our video, the US has officially lifted restrictions on Mythos / Fable 5 (as of July 1st). But we think the incident itself is still significant. It may be one of the clearest examples yet of how frontier AI models can trigger rapid government intervention and change the conversation around regulation.
But the upside that no one seems to be talking about is that these same frontier models are helping developers identify and fix vulnerabilities across massive codebases. That could mean a huge wave of security improvements over the coming years.
Watch the full breakdown on YouTube: eu1.hubs.ly/H0wHzDN0
Do you think this was the beginning of a new era of AI oversight, or just a temporary setback for Anthropic?
#AnthropicAI #ClaudeAI #Fable5 #AISafety #CyberSecurity #AIRegulation #TechNews
