

Empowering CISOs to build cyber resilience through AI-native continuous offensive security.
Silicon Valley
Joined January 2020
- Tweets1.3K
- Following126
- Followers1.3K
- Likes45


The biggest shift in AI isn’t intelligence, it’s authority. We are rapidly moving from AI that suggests actions to autonomous systems granted the authority to execute them: selecting tools, writing code, orchestrating workflows, and interacting with production environments without continuous human direction.
When you delegate authority to machines, the security paradigm fundamentally shifts.
The core question for security leaders isn’t "Can AI do this complex job?"
It’s: "Do we have verifiable proof that the system cannot exceed the boundaries we set for it?"
Read the full perspective: ridgesecurity.ai/blog/the-se…
#CyberSecurity #ArtificialIntelligence #OffensiveSecurity #InfoSec #AIagents #Automation

Your board will ask one question about PHP2Shell: are we exposed? Two critical PHP flaws (CVE-2026-109618 and CVE-2026-109619) let unauthenticated attackers run code on your servers.
Patching is the fix. Finding every server that still needs it is the hard part, especially end-of-life versions that will never get an upstream patch.
And a version number won’t tell you if an attacker can actually reach the flaw. RidgeBot sends a controlled probe and gives your team evidence instead of guesswork.
Full breakdown from our research team 👇
ridgesecurity.ai/blog/php2sh…
#PHP2Shell #CVE #CyberSecurity #RCE #VulnerabilityManagement #CISO

Ridge Security Technology Inc. retweeted

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.
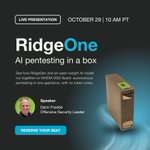
Before you trust any AI with offensive testing, you should be able to answer four questions:
🔗 Register: events.teams.microsoft.com/e…
1) Where do my credentials and findings go?
2) Can it act outside the scope I approved?
3) Can I trust what it reports?
4) What does it cost when we test every week instead of every quarter?
#RidgeOne was built around these questions. Darin Fredde will answer all four with a live presentation.
Can’t join live? Register anyway and we’ll send you the recording.

EV chargers are now critical infrastructure, so we built a realistic EV-charging lab and let RidgeGen loose with no credentials and no human help. In about 4 hours and for roughly $111, it reproduced real Pwn2Own attack chains: it took over the charger’s cloud, stole the cloud credentials, and could start or stop a charging session without logging in.
Every finding was proven by actually exploiting it.
👉 Download the use case: ridgesecurity.ai/use-case/au…
#Cybersecurity #EVCharging #AutomotiveSecurity

Great week at GovWare! ST Engineering, Singapore’s largest system integrator, hosted Ridge Security to present our EV charging infrastructure security solution.
EV chargers are the single most broken category at Pwn2Own Automotive. We showed how RidgeGen autonomously finds, chains, and proves real attack paths across charger cloud consoles and backends, and then retests after every fix. It’s expert-grade validation that scales to an entire charging fleet.
Thank you to the ST Engineering team for having us and to everyone who stopped by!
#RidgeGen #STEngineering #EVCharging #Cybersecurity #AgenticAI #Singapore


AI-driven security testing shouldn’t require sending your data outside your environment.
That’s why we built RidgeOne, a self-contained appliance for autonomous AI pentesting and red teaming. It runs RidgeGen alongside an open-weight model on NVIDIA DGX Spark, entirely on-site, with no external AI calls and no token costs.
RidgeOne is now available, and we’re excited to join the NVIDIA Inception program: businesswire.com/news/home/2…
#AIPentesting #RedTeaming #Cybersecurity

95% of critical infrastructure leaders are worried about AI-powered attacks. Yet 51% still decide what to fix first using CVSS scores or manual review. Here's why that matters:
CVSS grades each vulnerability on its own. Attackers don't think that way. They look for combinations.
Think of a house: an unlocked window, a spare key under the mat, a dog that doesn't bark. None of these looks serious alone. Together, they let someone walk right in.
Your environment works the same way. A few "medium" findings can add up to one critical breach, and a severity score won't show you that.
@PaloAltoNtwks 2026 State of Critical Infrastructure Cybersecurity Report shows the gap:
→ 92% say prioritizing alerts is important or critical
→ 51% still rely on CVSS scores or manual review to do it
→ 91% expect AI-driven security to help defend against AI-powered attacks
If attackers use AI to find your weak spots, you need to find them first. That's what Ridge Security solutions do, test your environment the way a real attacker would.
Source: Palo Alto Networks, 2026 State of Critical Infrastructure Cybersecurity Report www2.paloaltonetworks.com/ne…

We're proud and honored to announce that Ridge Security Technology Inc. has been accepted into @nvidia Inception, NVIDIA's program for startups building breakthrough AI technologies.
This gives the Ridge Security team access to NVIDIA's technical resources, experts, and AI ecosystem as we build #RidgeOne, our AI-powered pentesting solution running on NVIDIA DGX Spark.
Read the announcement: ridgesecurity.ai/blog/ridge-…
#NVIDIAInception #AgenticAI #OffensiveSecurity #Pentesting #RedTeaming #Cybersecurity

Every new AI capability in the SOC triggers the same question: how many analysts can we cut?
Our President & Co-Founder @linglingsan argues in @ForbesTechCncl that it's the wrong question.
The real problem in most SOCs isn't too many people. It's too much work. Teams face ~4,330 alerts a day, and only about 37% get a proper look. AI should take on the scale, repetition, and speed, while people keep the ambiguity, context, and accountability.
As the tools improve, that line can shift, but it shouldn't disappear.
"That's not a smaller security team. It's a more capable one."
Read the full piece 👇
forbes.com/councils/forbeste…
#Cybersecurity #AI #SecOps #SOC #HumanMachineTeaming #ForbesTechCouncil

"AI pentesting" now means very different things depending on who's selling it.
Some tools analyze source code. Some automate web app testing. Some actually exploit and chain. All useful. Not all pentesting. So before you buy, skip "Does it use AI?" and ask what it actually tests, from whose perspective, and whether it can prove what an attacker can reach and exploit.
Because a vulnerability is a data point. An attack path is an exposure.
Hom Bahmanyar breaks down the difference, plus 10 questions to ask any vendor claiming "AI pentesting." 👇
ridgesecurity.ai/blog/ai-pen…
Find. Prove. Fix. And Prove It Again.
#AgenticAI #Pentesting #OffensiveSecurity #CTEM #RidgeGen

One packet. No authentication. Server crash.
@DarkReading breaks down the TDengine zero-day discovered by Ridge Security researchers, and why it matters for organizations running OT/IoT environments >> darkreading.com/ics-ot-secur…
#RidgeSecurity #Cybersecurity #ThreatResearch

Ridge Security will be at #GovWare2026, 13–15 October at Sands Expo and Convention Centre. This year's theme is "Cyber at Agentic Velocity," and that's exactly where we live. Attackers are moving at machine speed. Your offensive security should too. Stop by to see how RidgeBot® and RidgeGen™ help security teams find exploitable risk and fix what matters, continuously and autonomously.
See you in Singapore!
#GovWare #SICW2026 #Cybersecurity #AgenticAI #OffensiveSecurity #PenetrationTesting #CTEM

We're excited to see our latest research featured in @SecurityWeek's news roundup. The roundup highlights our discovery of CVE-2026-42542—a high-severity vulnerability in TDengine that can impact uptime and real-time visibility across industrial telemetry networks.
Check out the full digest to read more about our findings alongside other top cybersecurity updates: securityweek.com/in-other-ne…

Check out our latest feature in @IndustCybersec! Our Research Team uncovered a high-severity vulnerability in TDengine that impacts industrial telemetry and OT monitoring. Read the full article to learn about the findings, potential impact, and remediation steps: industrialcyber.co/industria…

Worth a read if you run time-series databases in OT or IoT environments: ridgesecurity.ai/blog/one-pa…
Ridge Security's research team disclosed CVE-2026-42542 (CVSS 7.5), a pre-authentication flaw in TDengine's RPC handler.
A signed length value from the network is subtracted from an unsigned header size before any bounds check. That lets an undersized value wrap to a huge number that gets passed to memcpy(), so a single malformed packet to port 6030 crashes taosd. Versions 3.4.0.0 through 3.4.1.5 are affected, and the fix is in 3.4.1.6.
#VulnerabilityResearch #OTSecurity #IoTSecurity #CVE


Today, we published the industry's first public benchmark comparing leading LLMs in autonomous penetration-testing workflows. Key takeaways from the benchmark:
🔹 Architecture matters: An LLM alone is just a reasoning engine. To execute complex attack paths without stalling, it requires a dedicated agent harness (like RidgeGen™) to manage execution, track attack graphs, and independently verify findings.
🔹 Coverage vs. Efficiency: While models like Grok 4.5 led cumulative coverage (77%), models like Gemini 3 Flash and GPT-OSS-120B delivered exceptional cost-to-performance efficiency for enterprise operations.
🔹 Solving Over-Refusal: RidgeGen enforces safety boundaries, sandboxing, and target limits at the system layer—allowing models to perform authorized penetration testing without triggering AI alignment false positives.
As Ken Huang puts it: "A Formula 1 engine alone doesn't win the race. You still need the chassis, transmission, and brakes."
👉 Read the official press release on Business Wire: businesswire.com/news/home/2…
#AIinCybersecurity #AutonomousRedTeaming #PenetrationTesting #RidgeSecurity #RidgeGen #Cybersecurity #OffensiveSecurity

The raw benchmark numbers from our latest study tell a compelling story, but the real takeaway goes way beyond model leaderboards: the future of offensive AI isn't about model scale, it’s about harness engineering.
When evaluating models like Grok 4.5, Claude Opus 4.6, and Gemini 3 Flash across environments like Metasploitable3 and OWASP Juice Shop, a clear pattern emerges. High parameter counts and steep price tags don't guarantee seamless red teaming. Unassisted models still trip over safety over-refusal, lose track of attack graphs, and fail at deterministic execution.
Here is why the security industry needs to pivot its focus:
👉 Separation of Reasoning and Execution: A frontier LLM should act as a reasoning engine, not the entire security architecture. Deterministic tasks—like payload verification, target isolation, and state tracking—belong in a dedicated harness.
👉 Overcoming the Safety Bottleneck: Bypassing alignment over-refusal during authorized penetration testing shouldn't mean dropping guardrails. It means letting an orchestration layer structure actions safely and verifiably.
👉 Cost-Aware Security Operations: High-efficiency setups (like GPT-OSS-120B or Gemini 3 Flash) prove that with the right harness, enterprise red teaming can be both deep and cost-effective.
Instead of hunting for the "smartest" model, security teams should build or adopt architectures that turn raw inference into reliable, evidence-backed vulnerability validation.
🔗 Read the complete 8-model benchmark and technical breakdown on the Ridge Security blog: ridgesecurity.ai/blog/the-ha…
