
Cyber Threat Intelligence | OSINT | Misinformation | Threat Hunting
Joined April 2018
- Tweets923
- Following2.5K
- Followers844
- Likes6.5K




dougy retweeted

In recent weeks, more and more people retweeting or sharing shit from this BreakGlass AI thing... That in itself is a sad thing... but - unfortunately - not really surprising.
Until now, I didn't said anything about this publicly. But today, after seeing @JRoosen retweeted a tweet sharing that "quality" article + the "Official Twitter page of the 780th Military Intelligence Brigade (Cyber)" account tweeted that article, I have to ask: what the fuck is going on? Like, random people sharing random things is a thing... but more and more supposedly knowledgeable (in relation to malware/reversing/etc I mean, of course) people, and some also who not only supposedly, but seriously have knowledge are sharing these shits is not great, to say it nicely...
Anyway, the only reason I looked at that article was because when I saw the title containing "a Cardiff University GovRoam Relay", I was like "that could be something interesting if it's true, so let's just quickly look at the article and see if somehow it's true this time". So looked, and of course it turned out that it is wrong.
The article says right after "The Cardiff University Connection" that "This is the finding that prompted this writeup." - so the most important thing in the whole article is wrong.
The C2 IP (so not a domain, but an IP) of that sample is this: 151.242.152[.]131 - it has absolutely nothing to do with Cardiff University.
Also the article mentions 3 ports for that. The first two are clearly wrong, and about the third one I have no idea at all. The right base port is 4408, with a sandbox also showing traffic on port 4409 too.
😫


dougy retweeted
** ZERO-DAY ALERT **
EXPMON detected sophisticated zero-day fingerprinting attack targeting Adobe Reader users
justhaifei1.blogspot.com/202…
#expmon #zeroday #0day #threatintel #pdf #adobereader #acrobat #cybersecurity
dougy retweeted

CERT-UA has documented a significant tactical pivot by hacking groups. Adversaries are increasingly moving away from rapid, one-off data exfiltration in favour of securing long-term, unauthorised access to targeted systems.
"Cyber Threats: Ukraine" report cip.gov.ua/en/statics/analit…
dougy retweeted

Critical Claude Code vulnerability: Deny rules silently bypassed because security checks cost too many tokens adversa.ai/blog/claude-code-…
dougy retweeted

#3/3 - Windows malware
Windows users get on
pwin[.]onelink[.]me/zmFc/dt38769z >>
warboardgame[.]com/github-download.html
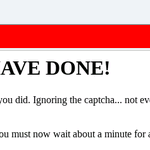
This fake Github download page is serving a ZIP Download (image 1). The same template has been observed in the past serving other Windows stealers.
Downloads are managed by warboardgame[.]com/archiveProxy.php, sending download stats to /statProxy.php
The build analyzed has been detonated here: app.any.run/tasks/83b9cbfe-9…
ZIP Sample -> 67fcd19f1be87ff47246a5fa40549df24da60eb81c62450efd5254fcb3628c1c
Inside ZIP, a .vbs script downloads a build via Powershell from botshield[.]vu/kFcjld. Once b64 decoded ->
15de71073f44c657c23f5f97caa11f1b12e654d4d17684bfc628cc1e5b6bcdd5
This file loads another file from Stealer C2
hxxp://45.93.20.61:5466/api/CryptoByte
(4e90d386c1c7d3d1fd4176975795a2f432d95685690778e09313b4a1dbab9997)
This file sends a log zip to hxxp://45.93.20.61:5466/api/upload
Sandbox log has been saved here -> 4ebbb900e083ccc240a8d354fb6466b339a5c4e7c1711a749ad00b1343bd96eb
On the log you can observe infected machine information (copying the format of Rhadamanthys) (image 3), a screenshot of the machine, default user agents used in browsers and a file "browser_decryption.log" that describes the runtime of an additional payload download from:
hxxp://45.93.20.61:5466/api/client
(751e45828a3ff877ed4add1508b3e54463376cfb11f3171bfac160653ca9813c)
This build scans the system looking for Browsers installation folders, decrypting the encryption of the browsers to extract data (such as User Agent in this preliminary log sent to C2), scan for crypto wallet files and extensions (that will also be extracted and send in log if found) and scan and extract Telegram session related files.
This file is also responsible to create persistence on the machine with scheduled tasks via CLI and via a XML file (image 3)
Additionally and to finish, the build makes requests to hxxp://45.93.20.195:5000
on /api/get_credentials , /api/get_challenge and /api/get_port using a Python client.
The client makes the machine to establish and maintain a reverse SSH tunnel, by retrieving SSH login credentials from the server (Request a challenge, send a response, and decrypt credentials). Then the reverse SSH tunnel is established on a free port of the C2 requested previously, attempting to act as a SOCKS5 proxy
Thank you to whoever leaked/extracted a related client, we love you <3. It helps much to understand what is going on (image 4)
4893748008f7c2a1508bb1bb4fa16a7a92de658b89fe7cc1e68e05a02a9aa4b4
No further analysis has been done, feel free to play with it
🏁


dougy retweeted

amazon's internal A.I. coding assistant decided the engineers' existing code was inadequate so the bot deleted it to start from scratch
that resulted in taking down a part of AWS for 13 hours and was not the first time it had happened
incredible
ft.com/content/00c282de-ed14…

dougy retweeted

Microsoft Defender researchers observed attackers using yet another evasion approach to the ClickFix technique: Asking targets to run a command that executes a custom DNS lookup and parses the `Name:` response to receive the next-stage payload for execution.

dougy retweeted
Possible interesting "topwebcomicsv1.msi": 5a1c14335d0a8b007ff2813e6ef738e8836be38257cc82fe03c02b71d71e1b01
It is using Deno, "the next-generation JavaScript runtime". Seeing malware using Deno is not a common thing, at least yet...
🤷♂️


dougy retweeted

UAC-0001 (aka #APT28 or #FancyBear) exploits CVE-2026-21509 to target Ukraine and EU with COVENANT framework. Details (UA only): cert.gov.ua/article/6287250


dougy retweeted
These fake Fortinet websites, still present on top browser search engines results, are now delivering a fake FortiClient app, signed "Taiyuan Lihua Near Information Technology Co., Ltd. (Certum-given)"
Its a phishing app, that will send credentials to vpn-connection[.]pro
Based on other signed files with same EV cert, recently the TA were also spreading applications impersonating Sophos, WatchGuard and Ivanti.
Analysis: app.any.run/tasks/e83886f5-d…


Watch out for fake Fortinet websites! Also do not blindly trust search engines AI summarizations as they can also lead to malicious redirects.
These redirects lead the user to a phishing site asking FortiClient credentials, sending to myfiles2[.]download, and downloading legit builds as decoy after a valid submission
>> Redirect
vpn-fortinet[.]github[.]io
fortinet-vpn[.]com
>> Phishing
vpn-fortinet[.]com


dougy retweeted
MongoBleed (CVE-2025-14847) is basically Heartbleed for MongoDB
- unauthenticated memory disclosure
- public POC, trivial to exploit
- leaks creds, tokens, cloud keys straight from RAM
- huge exposed surface on the internet
Good writeups and technical details here:
doublepulsar.com/merry-chris…
ox.security/blog/attackers-c…
blog.ecapuano.com/p/hunting-…
Patch fast, rotate secrets, and assume exposed instances were scanned(!)

dougy retweeted

We found that the fix to address the DoS vulnerability in React Server Components (CVE-2025-55184) was incomplete and does not prevent an attack in a specific case.
This is disclosed as CVE-2025-67779. New patches are available now, please update immediately.
dougy retweeted
We are excited that we were once again part in the coordinated international operation #OpEndgame 📣, taking action against the notorious information and credential stealer #Rhadamanthys 🕵️ We assisted in the takedown of threat actor infrastructure and share a full list of #Rhadamanthys botnet C2s on ThreatFox 🦊
Full list of Rhadamanthys botnet C2s:
📡threatfox.abuse.ch/browse/ta…
Europol press release:
🚨 europol.europa.eu/media-pres…

dougy retweeted

Possible new leak of internal Conti / Trickbot chats
A valuable dataset of internal communications that appears to be missing from public leaks.
Some conversations are dated 2019. Not previously published in Conti-Leaks; partially overlaps with Trick-Leaks, but in a different form.
mega.nz/file/hsx0xQxA#4S9TvM…

dougy retweeted

When you think there’s a new APT in town... Relax, it’s just our Red Team doing their thing (thanks to @Defte_ technique)😅
Want to improve your detections or challenge your team? Contact us!


dougy retweeted

Proud to support our Law Enforcement partners in another successful cybercrime disruption:
Operation SIMCARTEL
Great work everyone involved 👏
europol.europa.eu/media-pres…


dougy retweeted

⚠️ Breach Notification from F5 Networks:
“In August 2025, we learned a highly sophisticated nation-state threat actor maintained long-term, persistent access to, and downloaded files from, certain F5 systems.”
my.f5.com/manage/s/article/K…
dougy retweeted
Now you know why the China tab in the APT spreadsheet is the biggest one. You can only imagine the scale of damage their industrial espionage caused - and why some believe it’s far worse than anything ransomware groups ever did.


