

I make animated videos on computer security.
sf
Joined January 2019
- Tweets2.1K
- Following818
- Followers42.5K
- Likes10.7K



Suraj retweeted

> be pakistan government
> develop custom malware
> used to target high profile targets
> used against indian military and political ppl
> named SHEETCREEP
> send indian ppl file
> UAE-India Strategic Partnership Week
> malicious .lnk file
> .lnk executes malicious c sharp code
> does a bunch of stuff for persistence
> exfiltrates data to Google Sheets
> Google Sheets can be used to control victim pcs
> pakistan gov hardcodes google c2 sheet
> PAKISTAN GOV HARDCODES GOOGLE C2 SHEET
> embed access key in payload
> EMBED ACCESS KEY IN PAYLOAD
> malware nerds find it
> look inside
> find all targets from pakistan gov
> monitoring 91 ppl they think important
THEY STARTED SO STRONG. WHY DID YOU HARDCODE EVERYTHING. YOU BURNED YOUR OPERATION
securonix.com/blog/sheetcree…

Suraj retweeted

One of my personal favorite features announced at WWDC will I suspect be a sleeper hit: container machines, allowing your Mac to run a lightweight, persistent Linux environment with your home directory and repos automatically mounted: github.com/apple/container/b…


Suraj retweeted

Meanwhile local model 🫠


I pointed claude opus at chrome and told it to build a full v8 exploit for discord.
A week of back-and-forth pulling it out of dead ends. 2.3B tokens. $2,283 in API costs, and it popped a shell.
hacktron.ai/blog/i-let-claud…

Suraj retweeted
I pointed claude opus at chrome and told it to build a full v8 exploit for discord.
A week of back-and-forth pulling it out of dead ends. 2.3B tokens. $2,283 in API costs, and it popped a shell.
hacktron.ai/blog/i-let-claud…
Suraj retweeted

Solo founding is different.
We've built the place for it.
Applications open for @solofounders program's 4th cohort.
• 10 solo founders building "solo, together"
• 3 months in SF (+ optional housing)
• work closely with me + alumni
• $100k investment
Apply!


Suraj retweeted
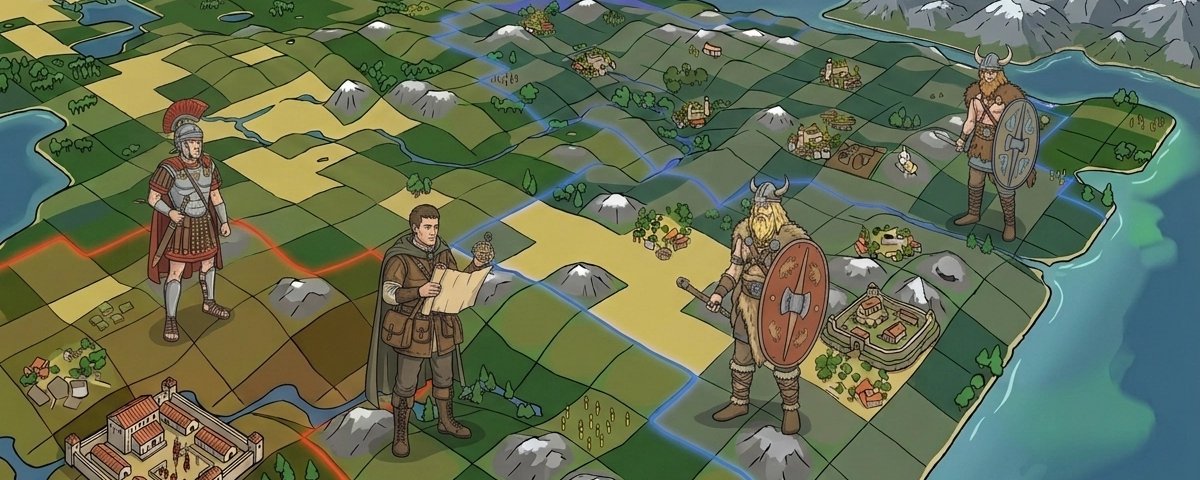
What happens when you let Claude or ChatGPT run a government?
I built CivBench to find out.
Everyday frontier AI models compete head to head in strategy games.
Here’s what our first set of matches revealed 🧵
Suraj retweeted

Hiring to build git for VMs. We fork, snapshot, and resume full sandboxes in 26ms. DM me if you are interested.
Suraj retweeted

New art project.
Train and inference GPT in 243 lines of pure, dependency-free Python. This is the *full* algorithmic content of what is needed. Everything else is just for efficiency. I cannot simplify this any further.
gist.github.com/karpathy/862…


Suraj retweeted
i have @Zai_org 's GLM 5 playing Civilization against Opus 4.6 and GLM5 is exploring in a Z shape, did we just hit brand-aware AI 🤔🤔

Suraj retweeted

Learn eBPF through hands-on exercises directly from your browser.
ebpf.party/
Suraj retweeted

For the past month, Pwno has autonomously discovered 29 vulnerabilities across Linux, FFmpeg, V8, Firefox, Webkit, Redis, PostgreSQL; with 15 OOBs, 6 UAFs.
Most of these bugs are fixed; some are still in the disclosure process. you can see them at bugs.pwno.io
It is really a pay-off moment for me. the idea of Pwno started out by simply harnessing gdb for solving ctf pwn challenges, exactly two years ago. eight months ago, after deciding to pivot from a campus startup I worked on for a couple of months, I decided to pick up what brought me to this crazy world of computer systems in the first place, binary security; and choose the most interesting problem I could ever think about: making AIs that can find cool memory bugs.
I am always saying we're doing research, but the fact is just that most of the time things don't work out. It takes a lot of learning, trial and error, rebuilding things from scratch, and most importantly in someway believing in things could work out even at times it sounds stupid to say.
it always amazes me how we can reinterpret systems that are entirely created by us in a completely different way. we'll hopefully find and patch more interesting bugs that in some way help the internet a little:)
Suraj retweeted
We’re open-sourcing pwno-backend - our previous production backend architecture, that covers up from uploading a binary to k8s ingress that went through a literation of six months, as Pwno heading to new direction.
github.com/pwno-io/pwno-back…
Suraj retweeted
A case study of AI-accelerated hacking:
How we at @HacktronAI hacked our way into Lovable's office, cut attack time from weeks to days, and helped secure Supabase from one of the most complex vulnerability chains we’ve ever worked through.
Suraj retweeted
This is my debut hour-long talk on exploiting a heap-overflow in Llama.cpp RPC, when I was fifteen at ZeroCon. Enjoy:)
research.pwno.io/llama-parad…

Suraj retweeted

Hack so big that even @HacktronAI is affected. We use a service that use the affected backend.