

EVM and Solidity tinkerer.
Immutable Avenue
Joined July 2020
- Tweets120
- Following90
- Followers898
- Likes19




Prodigal retweeted

Introducing Codex: The most accurate and reliable API for blockchain data.
Codex delivers real-time, enriched blockchain data for 4.5 million+ tokens & 1 billion NFTs on 57 networks data API.
Visit codex.io and get started in 5 minutes, for free.


Prodigal retweeted

The @SSS_HQ $SSS LP was just drained on blast because their token contract has a bug where transferring your entire balance to yourself doubles it.
The order of operations decrements the balance for "from" and then sets the balance for "to" - if these are the same address, the "toBalance" does not take into affect the decrement of "amount" and just overwrites the balance with the initial balance + transferred amount.
Attacker was able to get 1310 ETH from the LP by doubling their balance repeatedly and then selling it all
blastscan.io/tx/0x80012bf784…
blastscan.io/tx/0x62e6b906bb…
blastscan.io/tx/0xac3400e3d5…

Several rugpull attempts are mimicking @Furnace404's upcoming launch. If you read their website source code using Inspect Element, you can see they are using a font called "Highschool Runes". With this information, you can now decode their landing page and come to the conclusion that the countdown goes until the 21st, so anything launching before that is likely a scam.


This quoted post is unavailable.
1/ Yesterday, @minerercx's ERC-X token contract was exploited, resulting in a loss of 156 ETH due to a double-accounting error in its internal transfer function, which allowed an attacker to duplicate their own balance by sending tokens to themselves. xitter.cf/ProdigalWiz/status/175…
3/ In response to the attack, the @minerercx team quickly intervened, safeguarding a significant portion of the liquidity pool. This crucial action not only halted the exploit's advancement, but will also now enable now enable them to restart the project.
4/ The team also reached out for my assistance to diagnose and rectify the issue, and further bolstering their commitment to security, they've partnered with a professional auditing firm for a thorough review of their novel ERC-X token standard. All their updates are now transparently documented in their GitHub repository (github.com/Miner-Labs/ERC-X/…), signaling a well-prepared relaunch in the days ahead.
Prodigal retweeted

Thanks to @threesigmaxyz for completing a security audit of our ONFT smart contracts.
A detailed audit report can be found in the announcement below.

The full report detailing key findings is now available! github.com/threesigmaxyz/pub…

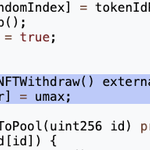
With the increasing popularity of ERC404 token contracts, we're seeing a rise in opportunistic rug pulls. Be extra vigilant for functions like `emergencyWithdrawNFT` hidden within contract code. These can allow the owner to mint infinite tokens in a discreet manner. As the saying goes, protect yourself at all times.

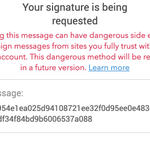
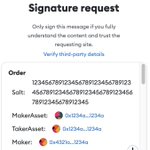
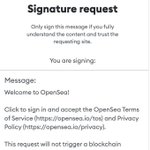
🪂 1/ It's airdrop season, a period when many of us interact with websites to claim tokens, which usually requires signing a message on your web3 wallet such as @MetaMask . But how safe is it?
Let's dive into the world of web3 signatures, uncover the risks, and learn how to spot the safe ones.

⚠️ 4/ Signing Hex Strings: Rare yet risky, these date back to the early days of platforms like @EtherDelta . Starting with "0x...", they are not standard text, and can interact with your assets in unpredictable ways. MetaMask flags them with a warning message for a good reason.

This is due to how the `transfer` function was implemented (etherscan.io/address/0x24289…), where addresses that receive tokens sent by a participant in the angel/private sale, are automatically marked as angel/private sale buyers as well.


Angels/Private salers on @crypto_bitlord7 token $MOLLY can send tokens to other users and mark them as an angel/private seller giving them the same sell tax restrictions.
One private saler is sending tokens to all top holders giving them all high tax.
@crypto_bitlord7 one way to "fix" this without redeploying the contract would be to exclude these incorrectly marked addresses from fees using the following function:

1/ @PeapodsFinance experienced a re-entrancy attack today, a notorious type of exploit in Solidity smart contracts. This incident is reminiscent of the early Ethereum days and TheDAO smart contract incident, which led to a hard-fork and the creation of Ethereum Classic (ETC).
5/ How could this attack have been averted? Simply by using @OpenZeppelin 's ReentrancyGuard.sol (github.com/OpenZeppelin/open…), and incorporating the `nonReentrant` modifier, just 12 letters, to the `bond()` and `debond()` functions would have been enough to prevent it.
