

keycloak as a service on @clever_cloud We can help you on your authentication
France
Joined December 2017
- Tweets216
- Following15
- Followers190
- Likes2



MFA Selector ensures mandatory Multi-Factor Authentication without mandating a personal device. Employees choose their factor (biometrics, hardware key, etc.). ✅
Secure access + Employee privacy = Win-Win.
blog.please-open.it/posts/mf…
#CyberSecurity #MFA #OpenSource #keycloak

oidc-bash now supports JWT Authorization grant !
github.com/please-openit/oid…


A few months ago, we launched a "Keycloak as a Service" offering with a partner: @clever_cloud
The product evolves with each iteration: IP filter, metrics, HA, autoscale, OAuth2proxy for all runtimes...
Here's a quick overview of everything we've done.
blog.please-open.it/posts/ke…

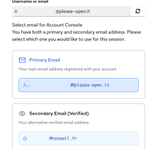
Secondary Email in Keycloak:
blog.please-open.it/posts/se…
allow users to add a verified secondary email and choose which one to share during authentication.

with @clever_cloud we just released a new version of Keycloak
- Keycloak version 26.6.1 (Workflows, SCIM...)
- Per-realm IP filtering (based on caddy) !
- CC_KEYCLOAK_ADMIN_IPS
- CC_KEYCLOAK_ADMIN_IPS_<REALM>
- CC_KEYCLOAK_PUBLIC_IPS_<REALM>
- CC_KEYCLOAK_SCIM_IPS_<REALM>


Lock your session without logging out in Keycloak by using a PIN code
blog.please-open.it/posts/ac…

oauth2proxy configuration generator for Keycloak
blog.please-open.it/posts/oa…
European Companies: if you host your data with a US cloud provider, you are not GDPR-compliant. ⚠️
The Cloud Act overrides data location.
Yes, even if your servers are in Europe.
⬇️
blog.please-open.it/posts/cl…
An authentication proxy is the best pattern for deploying SSO on existing and new apps.
The proxy is in charge of the authentication mechanism, the application receive authenticated requests with the user's details in HTTP Headers.
blog.please-open.it/posts/au…
After oidc-bash, we tried to make a JWT Decoder in bash. It was so complicated with the signatures!
github.com/please-openit/jwt…

Another module for Keycloak :
user attribute regexp mapper
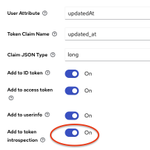
Because in Keycloak user attributes are multivalued (with ability to aggregate them with "user attribute mapper"), we added a regexp filter only to send back attribute if it matches.
github.com/please-openit/key…

New Keycloak module : groups regexp mapper. Map only groups (to a token, userinfo...) that only matches to a RegExp
github.com/please-openit/key…

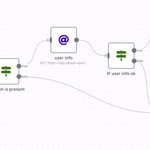
Keycloak has announced "workflows" as a preview feature. A welcome feature we already implemented years ago with... n8n.
This is how we did :
blog.please-open.it/posts/ke…
Postgres 18 now supports oauth2.0 authentication 🥳
postgresql.org/docs/18/auth-…
postgresql.org/docs/18/libpq…

Map HTTP headers to claims in tokens. We built this to support locales during a client_credentials authentication process
blog.please-open.it/posts/ke…
We built a desktop JWT decoder, directly accessible from the system tray :
blog.please-open.it/posts/jw…
github.com/please-openit/jwt…

An authenticator to match rfc8252 8.12 ! "native apps MUST NOT use embedded user-agents to perform authorization requests and allows that authorization endpoints MAY take steps to detect and block authorization requests in embedded user-agents"
blog.please-open.it/posts/us…