

We prove what an attacker can really do to you continuously, and we hand you the detection information you need to improve.
Belgium
Joined January 2023
- Tweets81
- Following17
- Followers136
- Likes26




Pinned Tweet
We scanned thousands of hosts for CVE-2026-48710 and found something important: being behind a reverse proxy, CDN, or Cloudflare is not always enough protection. In some setups, X-Forwarded-Host can still be used as a bypass. (1/2)
Loved catching up with old friends and making new ones at @_c0c0n_ 2026!
Getting such a warm welcome from Kerala Police was a highlight, along with @marver's training session.
Big thanks to the organizers, volunteers and speakers for a great event 👋
#c0c0n2026 #cybersecurity


Beyond the talk, it’s a great chance to grab lunch, connect with the community and swap ideas on where cybersecurity is heading.
If you’re around, drop by and say hello 👋
Link: a6k.be/whats-up/hack-your-ow…

4 Days To Go! We’re teaming up with @AikidoSecurity at A6K for a Brown Paper Bag Session on what no one actually tells you about scaling a cyber startup.
Our Co-founder Babette De Decker will be there sharing lessons and honest takeaways.
#Nemesis #Networking #offensivesecurity

🎙️ @marver is taking the stage at @offbyoneconf to break down the sheer chaos of AI security!
Between indirect prompt injection & models executing untrusted code, context has officially become the new attack surface.
If you’re at the event and want to catch up, drop us a line!

Connect with us to know how it will work on your system: persistent-security.net/cont…
🧐If you’ve been holding off an AI-driven security testing because of strict compliance, we get it!
🥳Introducing Nemesis’s On-Prem Local AI, you can run continuous attack simulations powered by a custom model hosted entirely on your systems.
#LocalAI #EUSecurity #ThreatToTest

Berlin's breach proves defenses need #continuousvalidation. Know controls work before hackers test them!
#Nemesis turns your threat profile into practical on-prem assessments; executing #MITRE ATT&CK techniques to map attack paths & convert missed TTPs to Sigma rules.
#Rhysida

Nemesis | Adversarial Exposure Validation retweeted

Great fun interviewing @marver of @Persistent_Psi and Rob of @goteleport ; for last nights Offensive vs Defensive in the Age of AI

The difference between pulling your hair out over endless alert and finishing your shift usually comes down to your stack. Nemesis's One-Click Intelligence handles the repetitive triage so you can jump straight to quick, clear resolutions.
#ThreatDetection #SOCAnalyst #security

Know More: persistent-security.net

Automated security testing makes AI integration safer.
Protect your organisation by using isolated test accounts, auditing user content to keep AI on track & rotating credentials the moment testing ends.
#AIpentesting #securityassessment #vulnerability #Breach #AttackSimulation
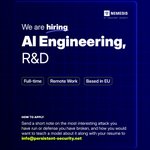
We’re hiring an AI Engineer for R&D at Persistent Security! We’ve got a fantastic team here and some really interesting work ahead of us.
Tag someone who should apply, or comment interested to get the conversation started! 📩
#hiring #AIEngineer #AIpentesting #AIsecurity

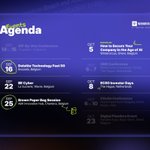
September is looking exciting!
We’re stepping away from our desks to catch up with the #securitycommunity, talk more about detection engineering & breach simulation, and meet in person.
Heading to any of these events? DM us; always up for a coffee ☕
#infosec #cybersecurity

The new built-in MITRE ATT&CK Navigator feature on Nemesis knows exactly which parts of the attack matrix you are testing, and which you are not, without leaving the platform.
Blog Link: persistent-security.net/post…
#MITREATTACK #Nemesis #offensivesecurity
AI agents mimic human pentesting logic at a scale scanners can't match, looking deceptively manual.
Detecting agentic traffic through response patterns and riddles is the first step in defense.
#AIpentesting #securityassessment #vulnerabilityassessment
Nemesis’s new feature, One-Click Intelligence, interprets your results for you & shows you what an attacker could do next, in your own environment, as a co-pilot to systematically validate your security.
persistent-security.net/post…
#ThreatToTest #RedTeam #securitycontrolvalidation
