

i hunt bugs.. Web2 | Web3 | AI security
0x000
Joined October 2019
- Tweets611
- Following413
- Followers361
- Likes3.3K


Rayaa 🚩 retweeted

The DSS 2026 timetable is live.
Nov 1–2 · Mumbai · Amber + Pearl
Pick your talks, save a shortlist and share it with @summit_defi.
Agenda: defisecuritysummit.org/2026/…
Tickets: luma.com/9qtxqqxx
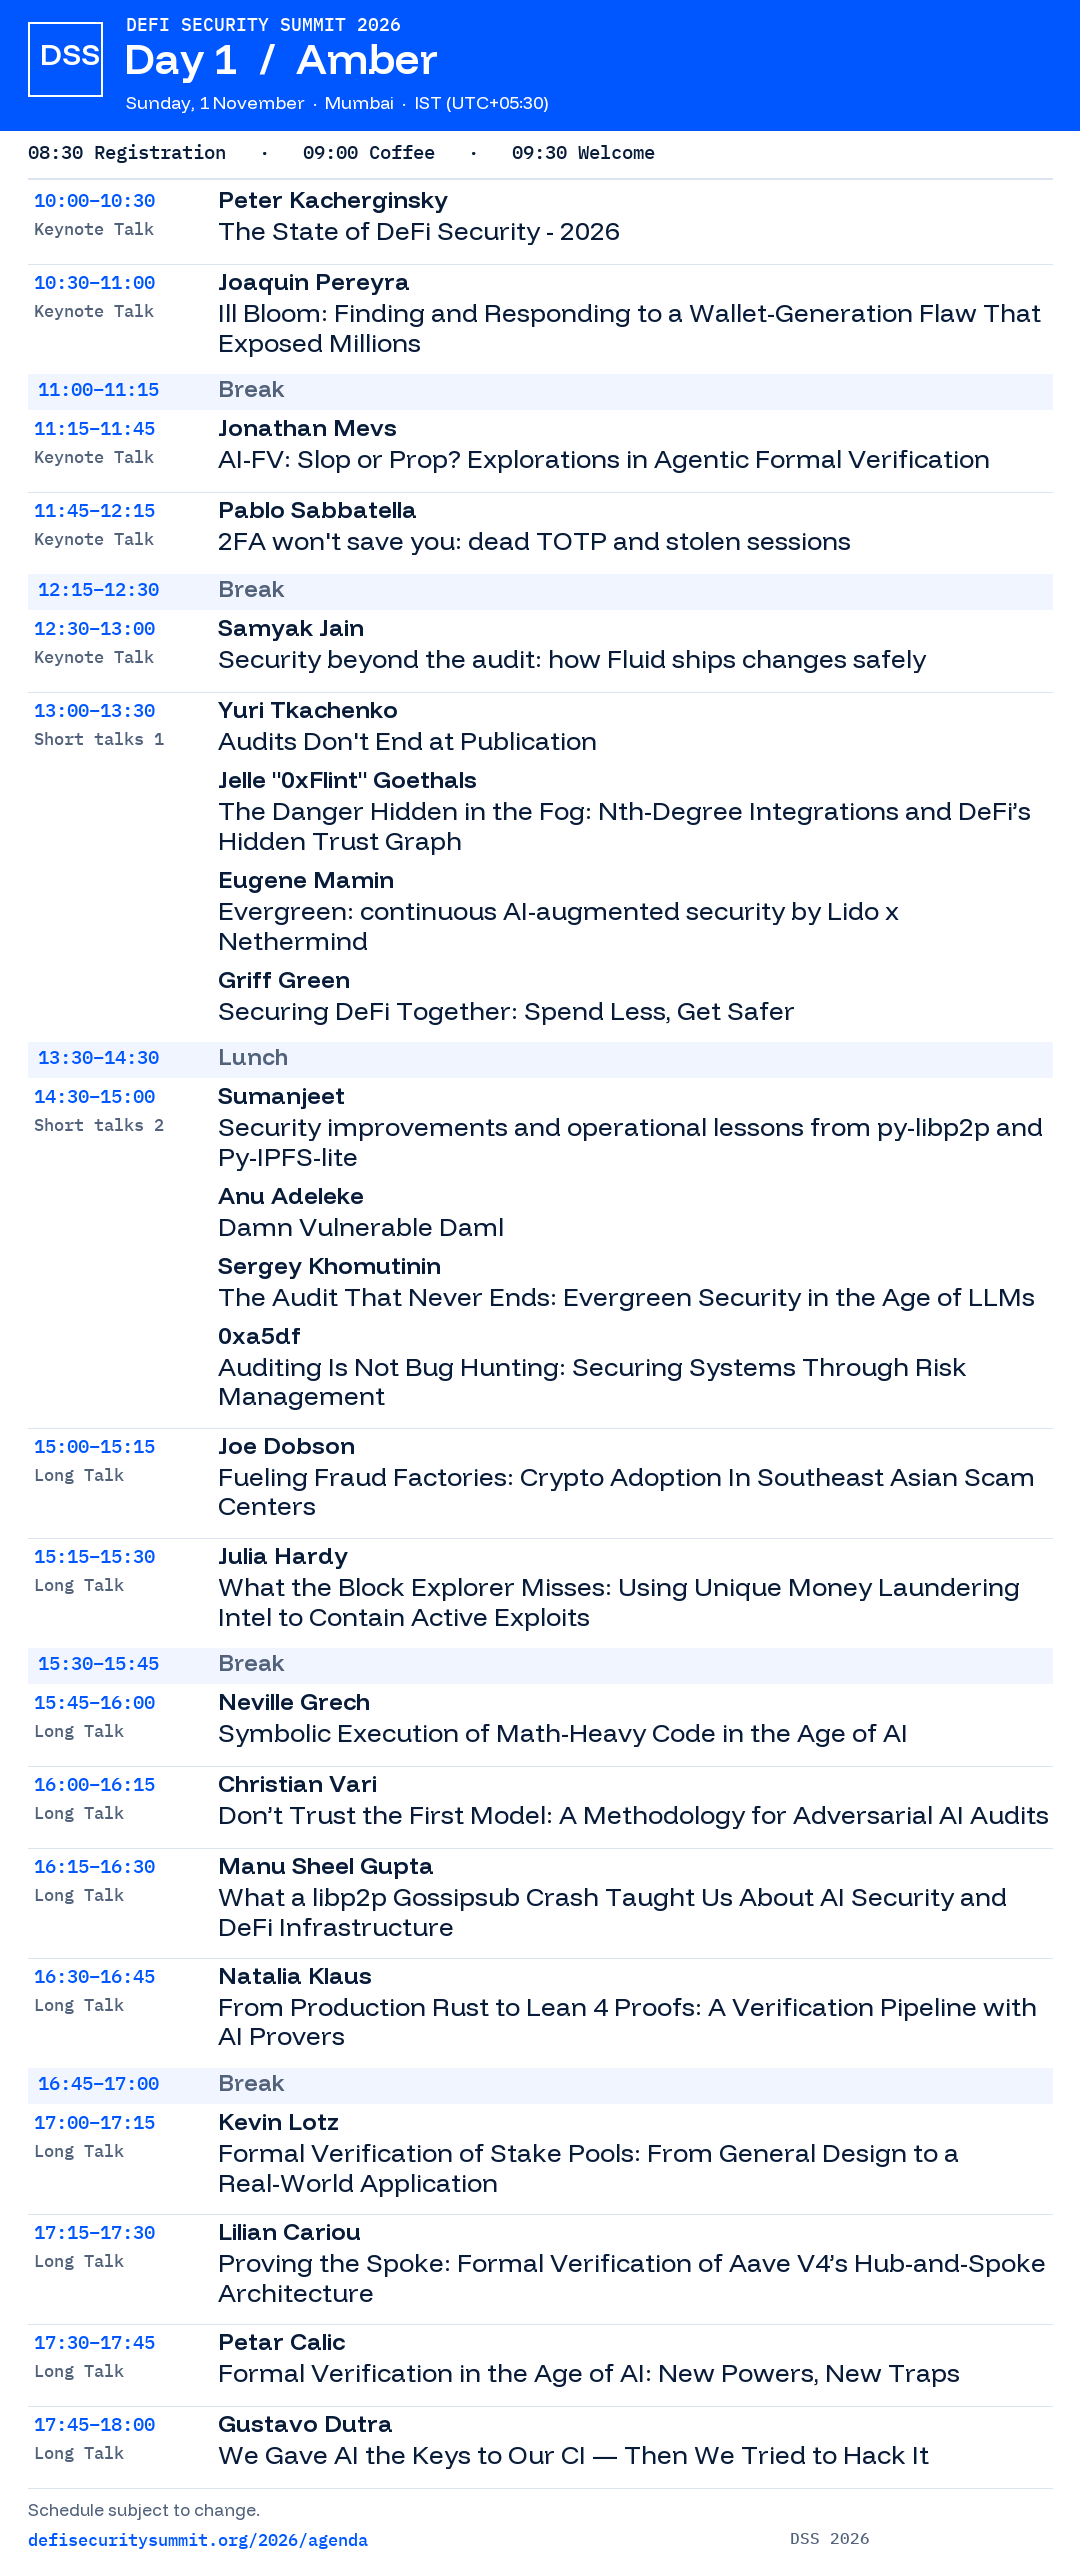
ALT DSS 2026 Day 1 Amber programme. All times IST. Schedule subject to change; full programme at https://defisecuritysummit.org/2026/agenda.

ALT DSS 2026 Day 1 Pearl programme. All times IST. Schedule subject to change; full programme at https://defisecuritysummit.org/2026/agenda.

ALT DSS 2026 Day 2 Amber programme. All times IST. Schedule subject to change; full programme at https://defisecuritysummit.org/2026/agenda.

ALT DSS 2026 Day 2 Pearl programme. All times IST. Schedule subject to change; full programme at https://defisecuritysummit.org/2026/agenda.


Rayaa 🚩 retweeted

All vulnerabilities look like trivial "simple bugs" once you understand the context.
Whenever I don’t immediately see them that way, it’s just because I’m lacking expertise in that area -- and that’s on me to improve.
Just like puzzles, anyone can verify and understand the solution once it’s shown to them. Very few people can come up with the answer themselves. That’s the hard part.
Last year I was monitoring hundreds of contracts and projects. I could only spend a few minutes on each update to assess the risk, since monitoring was just one of many things I was doing.
That said, I did have deep expertise in that specific codebase. I was obsessed with EIP-7702, actively hunting for vulnerabilities involving unbounded external calls, and constantly researching blockchains and bridges. That combination helped me spot the risk of this non-trivial bug during a major upgrade audited by a top team for a top project.
There are plenty of great hunters out there, and some absolute genius blackhats too. They could have found it as well.
That’s what luck looks like for me. We just have to find ways to get luckier.


Rayaa 🚩 retweeted
1/ 🚨 DamlForest just dropped — The CryptoZombies for DAML Smart Contract Security 🌲🔐
Hunt real vulnerabilities, fix DAML contracts in-browser, and grow your tree from Seedling → Ancient Tree.
12 Trails
50+ hands-on challenges
6 Growth Stages
Live Demo: damlforest.netlify.app/
Open Source: github.com/0xRayaa/daml-fore…
#DAML #Canton #SmartContracts #BlockchainSecurity #Web3Education

Rayaa 🚩 retweeted

📂 Key Crypto / DeFi Hacks
┃
┣ 📂 May
┃ ┣ 📂 @VerusCoin ($11.6M)
┃ ┣ 📂 @THORChain ($10.8M)
┃ ┣ 📂 @trustedvolumes ($6.7M)
┃ ┣ 📂 @TransitFinance ($1.88M)
┃ ┗ 📂 @EkuboProtocol ($1.4M)
┃
┣ 📂 April
┃ ┣ 📂 @KelpDAO ($292M)
┃ ┣ 📂 @DriftProtocol ($285M)
┃ ┣ 📂 @rhea_finance ($18.4M)
┃ ┣ 📂 Grinex ($13M)
┃ ┣ 📂 @wasabi_protocol ($5M)
┃ ┣ 📂 @volo_sui ($3.5M)
┃ ┣ 📂 @hyperbridge ($2.5M)
┃ ┗ 📂 @CoWSwap ($1.2M)
┃
┣ 📂 March
┃ ┣ 📂 @ResolvLabs ($23M)
┃ ┣ 📂 @SolvProtocol ($2.7M)
┃ ┗ 📂 @VenusProtocol ($2M+ bad debt)
┃
┗ 📂 TBD


Rayaa 🚩 retweeted

Glad that they will never ask themselves will I even get million dollar bounty
I will be also in this same list One day 🙏

Rayaa 🚩 retweeted

Pashov Audit Group 🤝 @Polygun_
We brought our security expertise to PolyGun, doing 2 audits and a pentest. 4 High, 19 Medium, 59 Low Severity findings uncovered🫡
Read all reports below👇
github.com/pashov/audits/blo…
github.com/pashov/audits/blo…
github.com/pashov/audits/blo…

Rayaa 🚩 retweeted

1. Happy to share our latest product: hackviz.shredsec.xyz
HackViz is a powerful new interactive platform to understand major exploits, visual, educational, and built for security teams, auditors, builders. 🧵

Rayaa 🚩 retweeted

Bear market now and its still the best moment to lock in and keep doing what you do.
Everyone is selling crypto, running to AI businesses, AI content, whatever. Do not sleep on security auditing - this space will rise again, trust.
The path is harder now, for newcomers and for old researchers who aren't positioned well. That's just reality.
2 things I'll say:
- If you have some achievements and ever did a private audit - reach out to every audit company/provider/brand you can find. Offer a lower rate than your best days, offer free, whatever it takes. Being in the game > watching from the sidelines. Always.
- Newcomers - now is the time to study hard. There aren't as many new issues dropping every day like the good times, but the opportunities in contests are still there and you can win. You just need to put in more work than before.
Don't leave the space. We need you!
Rayaa 🚩 retweeted

Under my last post, many people asked what I could have done better to progress faster.
If I had to summarize it, I’d point out two things: a proper combination of high-quality theory and consistent practice.
I strongly agree with @Jeyffre idea that most things we consider “hard” aren’t actually complex — they’re just poorly explained. I’ve seen this in mathematics, and I’ve seen the same in Web3 security.
To learn fast, you need to surround yourself with high-quality, limited content. Especially in Web3, there’s a huge amount of noise and surface-level material. Filtering aggressively is a skill in itself. Keep only what is deep, structured, and written by people who truly understand the topic.
Once you’ve built a solid theoretical base, don’t delay practice. That’s the most important part. Always prioritize hands-on work over “theory for later”. Applied learning compounds much faster than passive consumption.
Even now, I try to make everything practical. If I audit a protocol, I simultaneously study its category in depth. If I’m learning a general topic, I write concise notes about it. Writing and doing force clarity. Action beats theory almost every time.
The other crucial factor is focus.
Decide what field you want to grow in and push until you reach the level you set for yourself. Don’t try to advance everywhere at once. Move sequentially.
For example, I’d love to dive deep into ZK right now. But since I haven’t yet reached my goal of becoming a Senior EVM Researcher, I deliberately postponed that until June 1.
Progress is not about chasing everything.
It’s about choosing — and committing.
Rayaa 🚩 retweeted
January hit different!
🔥 Just wrapped my first collab with the absolute legends at @PashovAuditGrp — and it was straight fire.
Massive respect to these best auditors who made it unforgettable: @m3rlinbx0 @saidamdev @x0sauce
Huge thanks for the opportunity @pashov @cvetanovv0 @danogurtsov
Report Link: github.com/Sanket-722/Audits…

Rayaa 🚩 retweeted
Best resource to learn Rust 🦀 Lang
youtube.com/@letsgetrusty?si…
Based on The Rust Book
#rust #programmer #coding #cyber #web3 #Web3Community
Rayaa 🚩 retweeted
First contest results are in!
I landed at #50 🏆 in the Super DCA Liquidity Network audit with @sherlockdefi.
Got 1 Medium and 1 High finding. Good learning experience!
The climb starts now. 💪🚀


