
Adversary Research Engineer & CTI Lead @ AttackIQ
Joined August 2019
- Tweets18
- Following26
- Followers74
- Likes76
Fran retweeted
Most tracked flight right now - fr24.com/LVKEB/2e2e7cfd
According to tweets the founder and former CEO of @FTX_Official is en route to Argentina after the FTX collapse earlier this week.

Fran retweeted

Microsoft Threat Intelligence Center (MSTIC) has uncovered a wide-scale malicious email campaign operated by NOBELIUM, the threat actor behind the attacks against SolarWinds, the SUNBURST backdoor, TEARDROP, GoldMax, and other related components. microsoft.com/security/blog/…

Fran retweeted

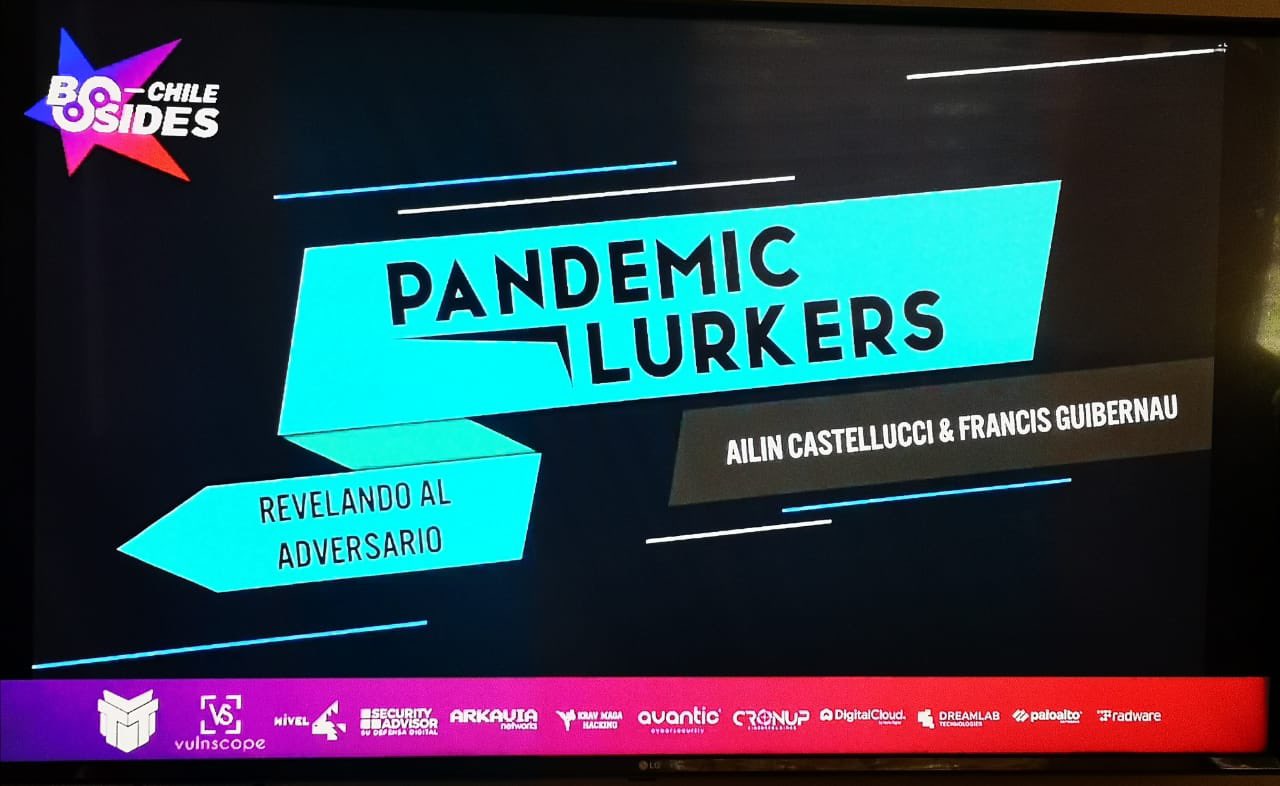
Recién termina nuestra charla con @OutrageousLynx en @BSidesCL 🙌🏻
Muchas gracias por la oportunidad, fue un placer🖤
Fran retweeted

📣 Terminando con los anuncios de @ekoparty! @OutrageousLynx nos hablará sobre atacantes aprovechándose de la pandemia mundial. 🌎
📣 Finishing with @ekoparty announcements! Don't miss @OutrageousLynx talking about the attacks in the global pandemic. 🌎

Fran retweeted
I had the opportunity to see this incredible research of @OutrageousLynx and @Cyb3rhuskys at @enigmaconf and it was amazing
You rock guys! ✨

This is the base for the presentation that we gave at @enigmaconf earlier this year! usenix.org/conference/enigma…
Fran retweeted

This paper gave born to an @enigmaconf talk and @MITREattack Virtualization\Sandbox Evasion technique! Check it out! Amazing job by @ThreatLibrary Team! 🥰❤️

📢 We are finally ready to release the extensive research @OutrageousLynx and I have been working on!! 🥳🥳
We developed the Environment Awareness technique, which describes all the techniques used by attackers to evade virtualised or analysis systems🕵️♀️ https://xitter.cf/t.co/jmaAdDZOJm
Fran retweeted

📢 We are finally ready to release the extensive research @OutrageousLynx and I have been working on!! 🥳🥳
We developed the Environment Awareness technique, which describes all the techniques used by attackers to evade virtualised or analysis systems🕵️♀️ https://xitter.cf/t.co/jmaAdDZOJm
We finally released the Environment Awareness Paper to the public! 🥳🥳
📢 We are finally ready to release the extensive research @OutrageousLynx and I have been working on!! 🥳🥳
We developed the Environment Awareness technique, which describes all the techniques used by attackers to evade virtualised or analysis systems🕵️♀️ https://xitter.cf/t.co/jmaAdDZOJm
Fran retweeted

Threat Group Cards: A Threat Actor Encyclopedia v2.0 is released.
Download: thaicert.or.th/downloads/fil…


Fran retweeted
Unite al canal de telegram de @EkoBlueSpace para recibir todas las novedades y seguir charlando sobre ciberseguridad defensiva! #InfoSec #BlueTeam #ekoparty #StayHome
t.me/joinchat/ETZyzFBIAgvjyf…

Fran retweeted

No se lo pierdan! 😁🤘

Vuelve el training de @33root y @fierytermite 🙌 #ThreatIntelligence con MITRE ATT&CK y otras herramientas #opensource ➡️ https://xitter.cf/t.co/qnjWZDM3DR
.
An awesome training returns 🙌 Threat Intel with MITRE ATT&CK and other open source tools ➡️ https://xitter.cf/t.co/qnjWZDM3DR
#eko2020

Fran retweeted

Congratulations to our amazing teammates @OutrageousLynx and @TorelloAyelen for getting accepted into #Enigma2020! 🥳🙌The work behind this talk is amazing! If you are going to be around SF, you can't miss the opportunity to see them!
I'm so excited!!! 🙀 Our talk @OutrageousLynx "Catch me if you can! Detecting Sandbox Evasion Techniques" will be at #Enigma2020 this month!✨ Don't miss it, we put a lot of hard work into it 😄🥰 xitter.cf/enigmaconf/status/1217…