

Security researcher
California | México
Joined April 2015
- Tweets3.9K
- Following329
- Followers5.7K
- Likes4.7K
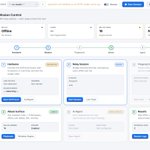



I’ve been working on ATRIUM, a research workbench for EMV payment systems.
It helps researchers observe APDUs, fingerprint cards, apply controlled mutations, and analyze contact, contactless, and ISO 8583 behavior.
It’s also used in SM Academy for hands-on payments.

Now you can listen the modules 1 and 2 instead of reading them. Still editing the training, some updates:
- Finished editing Module 1 and 2 in English and Spanish (including audio)
- Added the VM for the training in module 2
- Still working on content: academy.salmg.net/curriculum…

Salvador Mendoza retweeted

Acabo de crear algo que siempre quise: un software de recuperación de archivos borrados, gratuito, open sorce, facil de usar, que no dependa de que alguien sepa usar linea de comandos:
PhoinixDR · Open Source Data Recovery
pcoronaf.github.io/PhoinixDR…


If you want to have more technical details of this adventure that took more than 5 years: github.com/salmg/SIMtrace2-T…

It is been a long time since this xitter.cf/Netxing/status/1317332…
So decided to built the ISO 7816-3 T=1 support into Osmocom's SIMtrace2 card emulator, hardware-verified EMV transactions, two terminal configs, three silent defects hunted down: github.com/salmg/SIMtrace2-T…


𝗧𝗵𝗲 𝗔𝗺𝗼𝘂𝗻𝘁 𝗧𝗿𝗮𝘃𝗲𝗹𝘀 𝗧𝘄𝗶𝗰𝗲
A payment carries the amount twice: the copy the network approves, and the copy the card signs.
Nothing obliges anyone to compare them.
New series, chapter 1: salmg.net/2026/08/27/the-amo…

I recall discussing this topic back in 2018... This is just the tip of the iceberg. The relay attack will expand to multiple nodes, & we are already seeing relays involving EMV contact data...
The implementations used by authorizers and gateways will be put to the test.

🚨 WindRelay turns Android phones into live contactless payment proxies.
Attackers use SpyNote access to silently install the NFC relay malware. When victims tap a physical card on the infected phone, WindRelay streams its NFC data in real time to a fraudster's device, enabling fraudulent payments.
Read how it works: thehackernews.com/2026/08/wi…

Salvador Mendoza retweeted

#TROOPERS26 videos published:
youtube.com/playlist?list=PL…


Salvador Mendoza retweeted

This is it.
The Proxmark5 promotional video is LIVE.
Wireless. Modular. UHF-ready. Built from 10+ years of real-world RFID research.
This isn’t just another tool, it’s the one you’ve been waiting for.
Watch it. Then pledge. It's never gonna be this cheap again.
👇
indiegogo.com/projects/rfidr…
#Proxmark5 #RFID #NFC #HardwareHacking
Salvador Mendoza retweeted
Everything in the Proxmark3 Iceman firmware.
Every iCLASS, SEOS, Mifare, UL-AES, FeliCa update.
Every late night debugging session.
None of it is sponsored. All of it is open source.
If it has saved you time or taught you something, consider buying me a coffee.
Patreon this week: promo code 82409 for a discount.
patreon.com/iceman1001
#Proxmark3 #RFID #OpenSource #InfoSec


