






Nofix retweeted
Spent some time battle-testing my LLVM Python bindings by building a basic lifter for x86: secret.club/2026/05/21/strig…
Nofix retweeted

Made a little experiment of lifting IDA microcode to z3 to automatically resolve opaque predicates. It works quite well on a few malware families I tested on.
In the gif you can see Lumma stealer's opaque predicates being solved automatically:
Nofix retweeted
This 1-pager from Xusheng Li on GDB internals of how watchpoints are implemented is a delight to read! (especially that double-write behaviour false positive - I did not know about that)


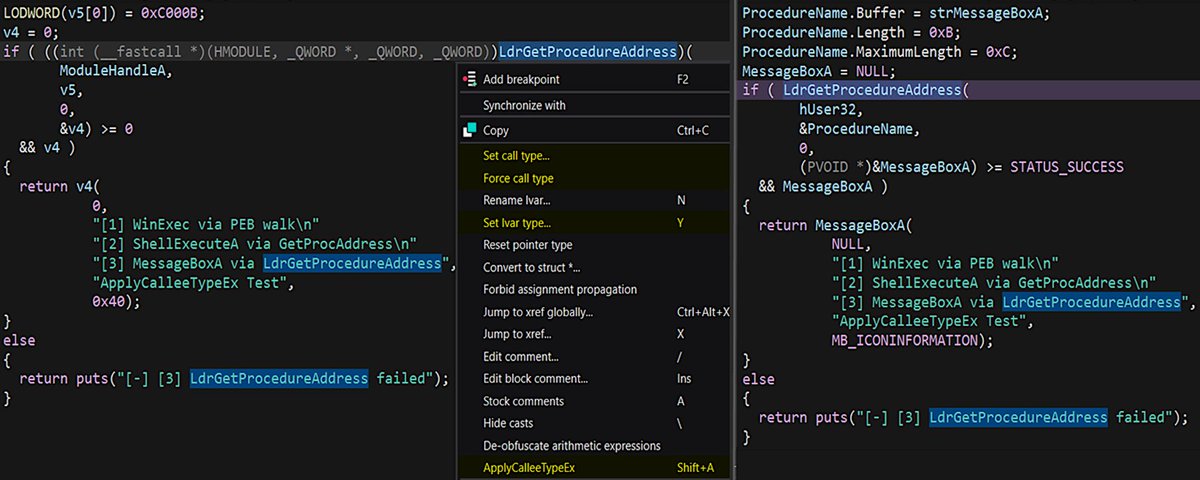


Nofix retweeted
Ever wanted to draw a triangle with OpenGL as a 2kb position-independent shellcode? No? Me neither.
But you can do it anyway: github.com/wbenny/scfw

Nofix retweeted

I'm glad to announce the release of my VS Code Extension: Multi-Search 🔍
If you find it useful, don't hesitate to share it with your colleagues or friends 🙏
- github.com/Ghizmoo/multi-sea…
- marketplace.visualstudio.com…


Nofix retweeted

In today's episode of programming horror...
In the Python docs of random.seed() def, we're told
"If a is an int, it is used directly." [1]
But if you seed with 3 or -3, you actually get the exact same rng object, producing the same streams. (TIL). In nanochat I was using the sign as a (what I thought was) clever way to get different rng sequences for train/test splits. Hence gnarly bug because now train=test.
I found the CPython code responsible in cpython/Modules/_randommodule.c [2], where on line 321 we see in a comment:
"This algorithm relies on the number being unsigned. So: if the arg is a PyLong, use its absolute value." followed by
n = PyNumber_Absolute(arg);
which explicitly calls abs() on your seed to make it positive, discarding the sign bit.
But this comment is actually wrong/misleading too. Under the hood, Python calls the Mersenne Twister MT19937 algorithm, which in the general case has 19937 (non-zero) bits state. Python takes your int (or other objects) and "spreads out" that information across these bits. In principle, the sign bit could have been used to augment the state bits. There is nothing about the algorithm that "relies on the number being unsigned". A decision was made to not incorporate the sign bit (which imo was a mistake). One trivial example could have been to map n -> 2*abs(n) + int(n < 0).
Finally this leads us to the contract of Python's random, which is also not fully spelled out in the docs. The contract that is mentioned is that:
same seed => same sequence.
But no guarantee is made that different seeds produce different sequences. So in principle, Python makes no promises that e.g. seed(5) and seed(6) are different rng streams. (Though this quite commonly implicitly assumed in many applications.) Indeed, we see that seed(5) and seed(-5) are identical streams. And you should probably not use them to separate your train/test behaviors in machine learning. One of the more amusing programming horror footguns I've encountered recently. We'll see you in the next episode.
[1] docs.python.org/3/library/ra…
[2] github.com/python/cpython/bl…

Nofix retweeted

Article très intéressant, surtout quand on a vu ma dernière vidéo sur la panne de l'aspirateur robot Dyson
codetiger.github.io/blog/the…


Nofix retweeted

Hey @ProtonPrivacy, why are you cancelling journalists and ghosting us. Need help calibrating your moral compass❓
First therapy session is for free 😘
Regarding phrack.org/issues/72/7_md#ar…

Nofix retweeted

🔥HeroCTF v7 is back at the end of November!
🚩You can now register your team on CTFtime
🔗 ctftime.org/event/2869
More information to come soon.
Nofix retweeted
🔐 Data encryption in Laravel environments is based on one secret: the APP_KEY. Our ninja @_remsio_ studied the impact of its leakage on the internet during an entire year.
synacktiv.com/en/publication…

Nofix retweeted
I've published my thoughts on part of the anonymization method used in that paper:
hackarcana.com/article/anony…
TL;DR: yeeeah... I don't think it works well

Anyone has a copy of the zenodo.org/records/15170676 dataset? (that's Discord messages; context: news.ycombinator.com/item?id…)
Authors seem to have restricted access, and I wanted to verify sth wrt their anonymization method.
Nofix retweeted
After 6 years, I made a blog thingy again.
This time about MmScrubMemory. An innocuous looking function that has bitten my ass several times in the last several years. And if you're developing a hypervisor, it might've bitten yours, too.
wbenny.github.io/2024-11-21-…
Nofix retweeted

We @binarly_io have just released idalib v0.2.0, an update to our @HexRaysSA IDASDK Rust bindings. It includes many new features: bookmarks, comments, and plugins APIs, hex-rays support, and documentation!
github.com/binarly-io/idalib
Thanks to our contributors: @yeggorv, @0xdea!


Nofix retweeted
New blog entry: C++ Unwind Metadata: A Hidden Reverse Engineering Bonanza msreverseengineering.com/blo…

Nofix retweeted

Bonjour citoyens de l'InfoSec,
Je suis très heureux de vous annoncer ma nouvelle aventure : OffenSkill !
offenskill.com/
youtube.com/watch?v=g5KP9CRE…
Suite à mon départ de ManoMano (miss you guys 💌), je me mets -enfin ?- à plein temps en tant que travailleur indépendant ! 🥳
Cela veut dire que je suis maintenant ouvert à :
- Des missions Pentest, Web / Cloud / devops / Linux / Infra 💥
- Des trainings de sécurité, allant du Novice à l'Expert 💣
- De l'enseignement en école 🎓
- Du mentoring "à la carte" 📜
- Des collaborations en Bug-Bounty 💞
Comme tout nouvel indépendant, tout conseil est bienvenu, que ce soit sur le site, l'offre, l'approche, ou autre ! 👼
Et as always, Like / RT / Share appréciés, voir même plus que d'habiture ! 😉
Au plaisir de vous voir en training ou mission,
Laluka
