

Mylon Intelligence is a solo cybersecurity newsletter delivering the latest threat intelligence — Know What’s Breached. ‖ [email protected]
Joined April 2026
- Tweets110
- Following1
- Followers61
- Likes2





🇲🇾🚨 MALAYSIA DATA BREACH ALERT
On 21/8/2026, the Majin / Majinahanashi ransomware group added a Malaysian company, PCA Group Sdn. Bhd., to their ransomware blog, with 2.65 GB of alleged leaked data.
Mylon Intelligence has done a full breach impact assessment.

The alleged leak contains more than 1k+ corporate documents, including sensitive personally identifiable information (PII) such as government documents including National Registration Identity Card (NRIC), passport, and etc.


📰 | NEWS
The FBI has arrested a Canadian cybersecurity executive for alleged conspiracy to threaten the confidentiality of information in order to extort money [1].
Sources:
1. G. Otto, “Canadian Cybersecurity Executive Arrested in Federal Extortion Case,” CyberScoop, Oct. 10, 2026. cyberscoop.com/edward-dubrov… (accessed Oct. 11, 2026).

🚨 ShinyHunters Breached The FBI
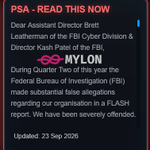
23/9/2026 — Threat actor, ShinyHunters (UNC6040) has allegedly breached the Federal Bureau of Investigation (FBI) [1].
The FBI is aware regarding "unauthorized activity" of FBIjobs.gov & is currently looking into the matter [2].
Sources:
1. Z. Whittaker, “Hacking group ShinyHunters claims it breached the FBI, stole agents’ and applicants’ data,” TechCrunch, Sept. 22, 2026. techcrunch.com/2026/09/22/ha… (accessed Sept. 23, 2026).

2. teiss Team, “FBI investigates claimed data breach of agent records by hacking group ShinyHunters,” teiss, Sept. 23, 2026. teiss.co.uk/news/fbi-investi… (accessed Sept. 23, 2026).

Mylon Intelligence is currently tracking 2 ransomware groups:
1. Spirals
2. n0n
These 2 threat actors are responsible for a sudden surge in organizations affected since September, 2026.


‼️🇦🇷 ARGENTINA RANSOMWARE ALERT
19/9/2026 — The "n0n" ransomware group has added the Ministry of Education of Argentina to its ransomware blog.
The alleged claims are currently unverified and Mylon Intelligence hasn't been able to identify the type of data allegedly leaked.

‼️🚨 RANSOMWARE ALERT
16/9/2026 — The Dragonforce ransomware group has added 2 companies to its ransomware blog:
1. Owen Leigh Optometry
2. Community Property Management
There are currently no statements from the affected companies.

‼️🚨 RANSOMWARE ALERT
6 September 2026 — The Direwolf ransomware group has added 2 companies to their ransomware blog:
- 🇺🇸 eAssist Dental Solutions | Alleged 12M+ records
- 🇺🇸 myLaurel | Alleged 6M+ records
The current claims are unverified.

‼️🚨 DATA BREACH ALERT
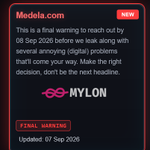
7 September 2026 — Threat actor, ShinyHunters (UNC6040), has added Medela to their ransomware blog.
Medela is a company involved with creating breastfeeding & pumping products.
There current claims are unverified.

Mylon Intelligence is currently tracking the Direwolf ransomware group.
Direwolf is a ransomware extortion group involved with data theft that has become active recently, publishing personal information from over 35 different organizations all over the world since August 2026.

‼️🚨 ShinyHunters (UNC6040) has added 4 companies to it's ransomware blog from 29 to 30 August 2026:
1. 🇺🇸 Neogen Corporation: Food safety
2. 🇺🇸 McKesson Corporation: Medical
3. 🇺🇸 Jack Henry & Associates: Finance
4. 🇸🇪 Elekta AB: Medical
The current leak claims are unverified.

🗞️ NEWS
28/8/2026—Two members allegedly affiliated with TeamPCP, a threat actor that has caused supply chain attacks affecting packages across PyPI and NPM has been arrested by Australian law enforcement with assistance by the FBI.


🚨‼️ DATA BREACH ALERT
18/8/2026 — Threat actor ShinyHunters (UNC6040) has added StreamLabs, a subsidiary of Logitech, to its ransomware blog.
Streamlabs (formerly TwitchAlerts) is a software company headquartered in San Francisco, California, and distributes a variety of software centered around live streaming and content creation.
The current leak claims by the threat actor are unverified, and the impact of the alleged data breach couldn't be assessed.

🚨‼️ DATA BREACH ALERT
14/8/2026—Threat actor ShinyHunters (UNC6040) has added Baxter International Inc. to its ransomware blog. The organization in question is involved with healthcare and located in Deerfield, Illinois, United States.
Over 7.1 million records of data, with some containing personally identifiable information (PII), were allegedly leaked in the cybersecurity incident.
The current leak claims by the threat actor haven't been verified.

‼️🚨 DATA BREACH ALERT
8 August 2026 — Threat actor, ShinyHunters (UNC6040) has added an unnamed company to it's ransomware blog. The threat actor claims to have over 11.5 million records of customer & employee personally identifiable information (PII) & over 3.1TB of internal corporate data.
The threat actor is seeking to communicate with the affected company — most likely for ransom — before August 10, 2026.
