

La familia es todo.
Joined November 2024
- Tweets760
- Following277
- Followers231
- Likes535

Pinned Tweet
The trading bot to use.
t.me/maestro?start=r-alonlic…

Millonarios retweeted

Today's events only reinforce how proud we are of the direction zauth is headed.
We are building the most powerful cybersecurity machine on the internet that ANYONE can use.
Something that currently costs 10's of thousands and weeks, will take hours and a fraction of the price.
Millonarios retweeted
Two critical bugs in PHP today.
Most people running PHP don’t even know it. It’s under their WordPress site, their checkout, or an app they built in a weekend.
This is the new internet, code on a stack you never chose and can’t name.
Learn your stack, and defend it, actively.

Millonarios retweeted

Another day, another major cybersecurity vulnerability.
The thesis gets more and more clear for @zauthinc.
AI Cybersecurity will take over. It already has within attackers and defense will catch up.
Incredible opportunity here.

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.
Crazy deal for any builders live on $ZAUTH.

Millonarios retweeted
Public smart contract audits go live this week.
Months of private testing with real clients, and many vulnerabilities caught before they cost users or protocols anything.
As complexity grows on the blockchain, so do paths for failure. Still, most new code is unaudited because audits are slow and expensive.
Not anymore. Zero excuse to forget about cybersecurity.
Haven't seen a harder working team or had so much conviction in one of my bags. Untouched and will stay untouched. solana:DNhQZ1CE9qZ2FNrVhsCXwQJ2vZG8ufZkcYakTS5Jpump will be THE leader of cyber security for all. There are multi-million raise capitals that Zauth is finding vulnerabilities for.
Here to stay, here to save.

solana:DNhQZ1CE9qZ2FNrVhsCXwQJ2vZG8ufZkcYakTS5Jpump has lived 10 months in a space where most things don't survive 10 days.
My thesis is simple. AI has revolutionized the world of cybersecurity, and you can bet on this revolution with @zauthinc.
zauth has found vulnerabilities affecting millions of people in the web2 world, alongside hundreds of thousands of dollars in smart contracts exposed to drains.
zauth has hundreds of customers, enterprise contracts, and is building a real company; a startup spawned from a fair launch.
There is nothing like zauth. From the product to the team to the token.
I am not wrong. Just early.
Millonarios retweeted

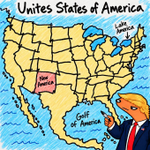
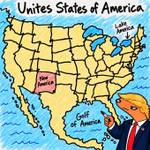
The official website of the Unites States is live.
unitesstatememe.si/


My thesis.

The last time I bullposted a play was Zauth, we ran with it from 20k to 8mil+
I've got the next conviction bag here. I aped Boden at 10k and jeeted it too early thinking it had no merit because there was no direct meme behind it.
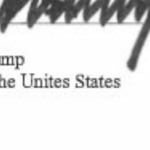
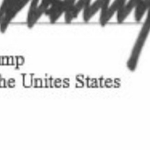
Now Trump signs the biggest executive order for "Super Intelligence" and doesn't proof read it says President of UNITES STATES.
A legit meme delivered to us to feed us. This could be WAY bigger than Boden-Tremp-Senders.
@potusmemelol
EDETAdjB1N8AARfoWWTwxeUJiNFjGAEhBv1JBePnagoh
Millonarios retweeted
Our smart contract audit engine found 70+ ETH drainable in a client's live contract.
Right now this engine is private, by contact only, but soon it will be self serve and fully autonomous. Upload the contract, get the audit.
Previously, smart contract auditing was limited to multi-week engagements and tens of thousands of dollars.
We put the most powerful tooling into your hands, for a fraction of the cost and time.
Millonarios retweeted
Proud to publish this one.
84 findings. 7 rounds. 5 days. 0 remain open.
zauth.inc/audits/agent-wormh…
After a whitebox review of their npm packages and dashboard payment code, every vulnerability found has been remediated.


Agent Wormhole has officially completed its security audit with @zauthinc 🪱
The goal was simple: put our security stack through a real, rigorous test and validate that the technology is ready to protect launchpads and agentic commerce.
84 findings. 83 resolved (1 withdrawn). 0 open.
1.19M+ fuzz cases. 423 exploitation variants. 7 rounds of remediation verification.
Every fix was verified through execution.
This is another step toward making Agent Wormhole a trusted security layer for the next generation of AI agents, launchpads and agentic commerce.
Full audit by Zauth:
zauth.inc/audits/agent-wormh…

Millonarios retweeted
In three years the ability to find and exploit vulnerabilities went from a sophisticated few to everyone.
Offense got the upgrade, but defense did not.
This is why zauth exists. Agents that break into your systems the way the new attackers will, before they do.
Millonarios retweeted
We found a vulnerability in Dragonfly, a database downloaded over 25 million times. It affects every release up to and including the latest one.
Apps use it as their short term memory. Anything that needs to load instantly lives there instead of a slow database.
Dragonfly had three ways to take in data and only checked one of them properly. One malformed file through either of the other two could crash the server and wipe everything in memory, or trick it into leaking pieces of its private memory. The leak worked 19 out of 30 times.
Project Apex, our public security initiative, found it autonomously.
If you run Dragonfly, set a password until the patched release ships.

Our first ever GitHub advisory is live, in DragonflyDB.
One flag, with one call site. deep_integrity was set for RESTORE and nothing else, so replication and RDB file load ran the same deserializer with validation off. Malformed listpack loads clean, HGETALL segfaults the server, or leaks adjacent heap (if you shape it like that), 19/30 runs, live pointers.
Found autonomously by Project Apex. Disclosed Sep 1, fix merged Sep 17, published today by DragonflyDB team.
github.com/dragonflydb/drago…

Millonarios retweeted
Proud to partner with @agentwormhole as we build together to make the future of the internet a much safer place.
We’re currently working with @zauthinc to audit Agent Wormhole’s hosted API and x402 payment flow.
Security products should be held to the same standard they ask everyone else to meet.
We want the layers protecting agent payments and execution to be tested by people whose job is finding where systems break.
