






This is the kind of growth that actually means something.
𝟭,𝟭𝟯𝟭 → 𝟯,𝟴𝟮𝟴 verified agents in three months is proof that teams are starting to treat accountability as non-negotiable.
▫️ Multiple platforms already integrating,
▫️ 200+ chains supported,
▫️ x402 live, and
▫️ a hackathon on the way.
@Concordium is delivering the identity layer the agentic economy will run on.

From 1,131 to 3,828 registered AI agents in just 3 months.
6 platforms now use Concordium’s Agent Registry, including @XDCNetwork, @AITECHio & @8004_scan.
200+ chains supported, x402 payments live, and a hackathon with @encodeclub coming up.
Full update 👇
concordium.com/article/agent…

Imagine securing a national database, only for a poorly monitored third-party account to expose millions of records.
That’s the unsettling lesson from Denmark’s reported data incident.
The main system wasn’t breached. The access granted to a smaller company became the weak link.
It’s a reminder I keep coming back to: “your security is only as strong as the access you forget to watch.”
And yes, even the strongest front door won’t help if you leave the side entrance unattended.
That’s why privacy needs more than encryption. It needs strict permissions, proper monitoring and safeguards that hold up beyond good intentions.
A lesson worth remembering in the age of AI agents, too.
@OasisProtocol oasis-network:native

Oasis is proving that blockchain can do more than just power crypto.
The Oasis x Slovenia cycling season brought people together across 5 races, with over 15,000 sign-ups.
But what makes this even more interesting is how Oasis Sapphire helped make the prize draw transparent and easy to verify.
This is what I love about @OasisProtocol: Taking privacy technology beyond the usual crypto conversations and showing how it can work in real-life activities.
Making things more private doesn’t mean they can’t be transparent when it matters.
#Oasis is building technology with real-world use cases, and this cycling season is a great example of that. More people need to see what Oasis can do
Read the full recap 👇
oasis.net/blog/oasis-x-slove…
@PrivanaFinance $ROSE


Building AI agents for real business use requires more than giving them a wallet and letting them transact.
With @Concordium integrated across @XDCNetwork, developers and businesses can link agents to verified owners without exposing private identity details on-chain.
→ Keep your agent on XDC.
→ Give others a way to verify who stands behind it.
Less “just trust the bot,” more accountability.

#Concordium has had a busy year, from identity infrastructure to sponsored transactions and AI agents.
I’m curious to hear how these pieces fit together and what the team has lined up next.
Town Hall #6 is on October 28.
Questions are open and I’ll be tuning in, you should too.
The Town Hall you’ve all been waiting for is finally here! 🎙️
Concordium Town Hall #6 | Oct 28, 15:00 UTC
From what we’ve shipped to what’s next, we’re covering it all.
Got questions for the team? Submit them below! 👇
forms.gle/EQdKFcJNxy7rY8At5
➝ Your database is encrypted
➝ Access is restricted
Security team is happy.
Meanwhile, the same sensitive data is sitting in debug logs, analytics dashboards, support tickets and third-party tools.
Funny how the front door gets reinforced while the side doors stay open.
One thing @OasisProtocol keeps highlighting is that privacy can fail in the spaces between systems, not just at the main storage layer.
🧵

2/3
This gets even more important with AI agents.
▫️ Agents handle private context, credentials and tool results.
▫️ Those can spill into traces, monitoring systems, error reports or conversation logs if the architecture allows it.
Telling an agent “𝘥𝘰𝘯’𝘵 𝘦𝘹𝘱𝘰𝘴𝘦 𝘴𝘦𝘯𝘴𝘪𝘵𝘪𝘷𝘦 𝘥𝘢𝘵𝘢” is helpful.
Making sure sensitive processing cannot casually spill into the host’s logging systems is a stronger approach.
That’s where confidential computing comes in.
3/3
➱ #Oasis brings this approach through Sapphire’s confidential smart contracts and ROFL’s confidential offchain computation.
➱ By processing sensitive data inside Trusted Execution Environments, these systems can keep plaintext hidden from the host, while attestation helps verify the execution environment.
It doesn’t eliminate every possible leak: Data flows and application design still matter.
But the principle doesn’t only protect where data lives, it protect what happens while it moves and gets processed.
Sometimes the weakest link isn’t the vault. It’s everything connected to it.
🖇️ More Details: docs.oasis.io/build/sapphire…
#ConfidentialComputing #DataPrivacy #OasisProtocol
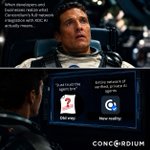
XDC SI agents could already discover services and pay in USDC.
But payment alone can’t answer the big question:
Who stands behind the agent?
That’s why @XDCNetwork chose @Concordium as its exclusive identity verification layer.
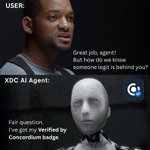
The Verified by Concordium badge links an agent to a verified person or business, while keeping their private identity off-chain.
➝ The agent keeps its wallet.
➝ The owner keeps their privacy.
Accountability comes with it.

AI agents need to prove who stands behind them, not expose who that person is.
Concordium’s Agent Registry links agents to verified people or businesses while keeping private identity details off-chain.
With XDC SI adopting it across its marketplace, agent accountability is moving beyond theory into real-world use.
@Concordium @XDCNetwork

AI agents can move money.
But who stands behind them?
@Concordium brings verified identity to XDC AI, linking agents to accountable ownership without exposing sensitive identity data.
✓ Verified agents
✓ Real accountability
AI agents can move money over x402.
But who’s accountable for them?
@XDCNetwork is taking that question seriously.
Concordium is now the exclusive identity verification layer for XDC AI, bringing the Verified by Concordium Badge to an entire agent network.
And it’s already live. ↓
concordium.com/article/conco…

Managing a crypto treasury with a single key can create a single point of failure.
That’s why multisig wallets matter. They allow teams to require multiple approvals before transactions can be executed, adding an extra layer of security and accountability.
With @OasisProtocol Safe on Sapphire, teams can bring this familiar multisig setup to a network built for confidential smart contracts.
A useful step towards safer, more flexible onchain asset management.
Learn more about Oasis Safe, and how to use it here 👇
youtu.be/-lMfsSuJDNo?si=PxID…
#OasisNetwork #ROSE
Ever wondered where $CCD fits into a @Concordium transaction?
Here’s the flow:
→ A transaction is initiated.
→ A network fee applies.
→ $CCD pays the fee.
→ Validators help process transactions and secure the network through proof-of-stake.
Every step has a role, and $CCD is part of what keeps the network running.
Sometimes, the best way to understand a token’s utility is to see it in action.

Would you trust an AI agent with your money if you couldn’t verify what was running behind the scenes?
A convincing answer from an AI doesn’t mean its execution deserves blind trust.
This is where @OasisProtocol gets interesting.
𝗦𝗮𝗽𝗽𝗵𝗶𝗿𝗲 brings confidentiality to smart contracts, while 𝗥𝗢𝗙𝗟 enables verifiable offchain computation.
Together, they give developers tools to build AI applications where sensitive data stays protected and execution can be independently verified.
As agents gain more control over real assets, “𝙩𝙧𝙪𝙨𝙩 𝙢𝙚” shouldn’t be part of the security model.
𝗧𝗿𝘂𝘀𝘁 𝗻𝗲𝗲𝗱𝘀 𝗽𝗿𝗼𝗼𝗳
oasis-network:native #OasisProtocol

A security certificate can look impressive in a PDF.
But when your data is being processed today, how do you know the system is still running under the conditions you were promised?
That’s the gap worth paying attention to.
@OasisProtocol is making the case for something stronger than taking a document at face value: verifiable proof at the point it matters.
🧵👇

2/3
This is where remote attestation comes in.
With Trusted Execution Environments (𝗧𝗘𝗘𝘀), a receiving party can verify cryptographic evidence that specific software is running in a genuine, expected hardware environment.
Instead of relying only on a company’s claim, you get something you can check.
That’s an important distinction for confidential AI, private transactions and autonomous agents handling sensitive data.
3/3
One important nuance: attestation doesn’t magically prove code is bug-free or eliminate every hardware risk. Audits and ongoing security work still have a job to do.
What it adds is another layer of verification, right when data is processed.
That’s what I find interesting about the #Oasis approach: less “𝘁𝗿𝘂𝘀𝘁 𝗼𝘂𝗿 𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗣𝗗𝗙” and more “𝗵𝗲𝗿𝗲’𝘀 𝗽𝗿𝗼𝗼𝗳 𝘆𝗼𝘂 𝗰𝗮𝗻 𝘃𝗲𝗿𝗶𝗳𝘆.”
✓ Privacy is useful.
✓ Privacy you can verify is a stronger foundation.
🖇️ More Details: oasisprotocol.org/blog/tees-…
#VerifiableAI #Privacy

AI agents can make decisions, interact with protocols and move assets on their own.
But when an agent acts, one question matters:
who stands behind it?
@Concordium’s Agent Registry gives agents a verifiable on-chain identity linked to a verified human or business. Zero-knowledge proofs help verify that link without exposing sensitive personal data.
As agents take on real responsibilities and handle real value, knowing what they can do isn’t enough.
You need to know who authorised them and who answers for their actions.
Autonomy gives agents the ability to act.
Identity brings accountability.
