
VP @ZeroNetworks | Former @Microsoft | Retired @USMC. Author, Gamer, Classic Car Enthusiast and all around Techie / Security Human.
Washington, USA
Joined April 2014
- Tweets2.7K
- Following455
- Followers1.1K
- Likes7.1K





Nicholas DiCola retweeted

Reporting on MTTD or alert volume won’t dismantle the language barrier between CISOs and business leaders.
Containment metrics bridge the gap by showing how resilient the business is against worst-case scenario cyber threats.
Zero’s Cyber Resilience Toolkit for CISOs provides a step-by-step framework for assessing your current posture and building a business-aligned strategy for strengthening cyber resilience, plus a customizable deck for reporting the findings that actually matter at the board level.
📍Get the toolkit ➡ hubs.li/Q04ygmfx0
#CyberResilience #Cybersecurity #CISO
Nicholas DiCola retweeted
New machine joins the network? It's segmented automatically. No tickets, no manual rules.
"We allow what we allow and everything else is locked down."
We apply the same logic to AI: control what agents can reach and contain AI-driven attacks before they spread.
See it for yourself → hubs.ly/Q04yhBn50
Nicholas DiCola retweeted
Outcomes like containment and uptime protection drive executive buy-in for security investments. How can CISOs build a strategy that delivers on those objectives?
We outline a three-step framework in our Business Impact Analysis Guide:
🔎 Critical asset identification: partner with your CRO, CIO, and COO to find out what matters most to the business
🗺️ Attack path analysis and containment metrics: map how an attacker could reach those assets – and what would stop them – to score cyber resilience
📊 Investment prioritization: overlay the business and technical analyses to learn where security teams should focus first
Connect the dots between security enforcement and business value with our Cyber Resilience Toolkit for CISOs 👉 hubs.li/Q04ygk_q0
#CyberResilience #Cybersecurity #CISO


Nicholas DiCola retweeted
There's a person at Zero you don't know - but you should, according to @crn's latest list.
Ronit Spiwak-Wolf is our Partner Marketing Lead - and was one of the OG marketing team members at Zero. She built the partner marketing function from the ground up, creating the programs, communications, and enablement infrastructure that has helped establish Zero as a 100% channel-first organization.
The list of successful events, relationships, and programs that she's built and run is too long to mention here. So we'll just say this about her exemplary dedication to Zero: Thank you, Ronit. We are so proud to have you as a core part of ZeroNation!
CRN - The 100 People You Don’t Know But Should 2026: hubs.li/Q04y8Cv20
Nicholas DiCola retweeted
"We're going full throttle agentic AI automation."
But: "AI has created more brand new problems than it's solved on the security side. It's just a mad rush to get your arms around everything."
80% of enterprises already have AI tools running inside their environment - sanctioned and unsanctioned. What percent of that access is actually enforced?
Everyone's foot is on the gas, but whose hands are on the wheel?
See how you can accelerate AI innovation at your org without losing control with Zero like your CISO peers.
hubs.li/Q04xHY8L0
Nicholas DiCola retweeted
Maybe the answer to AI isn't more AI.
Every booth at Black Hat seemed to be selling the same thing: AI-powered attacks, so buy our AI-powered defense. Some of that was real. But it skips past the stuff that already works.
AI can make an attacker faster, however it doesn’t hand them your whole network.
Getting in is one hurdle. How far they can move once they're inside is another — and that one we know how to solve. Zero Networks. Zero Trust. Segmentation.
AI speeds up the attack. Segmentation keeps it from becoming a disaster.
We had exactly this conversation at Black Hat with an architect in the utility industry — someone who doesn't get to treat "blast radius" as hypothetical. Worth the watch (only one minute of your time).
Bonus because it buys us more time for tennis on the weekend.
#ZeroNetowrks #Cybersecurity #AI #ZeroTrust #Microsegmentation
Nicholas DiCola retweeted
🎉 Big news: 𝗪𝗲'𝘃𝗲 𝗲𝘅𝗽𝗮𝗻𝗱𝗲𝗱 𝗼𝘂𝗿 𝗣𝗮𝗹𝗼 𝗔𝗹𝘁𝗼 𝗡𝗲𝘁𝘄𝗼𝗿𝗸𝘀 𝗶𝗻𝘁𝗲𝗴𝗿𝗮𝘁𝗶𝗼𝗻.
The original integration paired our microsegmentation with their NGFWs. This one goes further — zero-touch containment, traffic redirection to Prisma AIRS and Strata Cloud Manager, and now AI agent governance on top.
What that means in practice:
→ Zero Networks contains compromised assets automatically, no manual policy writing
→ Selected traffic gets redirected to Palo Alto for deep Layer 7 inspection
→ AI agents get identity-based policies restricting where they can connect
→ Everything's visible in one place through Strata Cloud Manager
Full details: hubs.ly/Q04tRyVK0

“advised to segment networks to block lateral movement…” so microsegment. Got it !!
@ZeroNetworks

CISA: Medusa ransomware hit over 500 critical infrastructure orgs
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

OR... hear me out... Just microsegment with @ZeroNetworks cause then you get visibility into every activity + FW on!!

ACTIVE DIRECTORY GROUP POLICY SECURITY: WINDOWS FIREWALL ENABLED FOR ALL PROFILES
Period.
Setup:
Group Policy Object is at the domain root level.
GPO is set to ENFORCED
All three Profiles are ENABLED
Display a notification for new protocols ENABLED
Logging is set to ENABLED
Right?
When we get asked to turn the Windows Firewall _off_ for any reason we ask WHY?
"Oh, because our auditing software needs it off."
Me: NO. What product?
Them: XYZ Audit Software
Me: Okay, their docs say TCP on ports 9997-9999.
Them: Oh
* All y'all know where that's going to go right?
"We need it off for troubleshooting purposes."
Me: How do you know for sure it's the problem?
Them: We turn it off
Me: Did you know there's no OFF for Windows Firewall?
Them: Uh ...
Me: It goes into Limp Mode locking down the stack!
Them: Oh ...
Me: We have logging enabled so guess what?
Them: What?
Me: There's no DROP messages for your app so you're all good no firewall in the way!
Me: DOH! SMH!
EDIT: Oh, and not to forget, the Public Profile is locked down period. No exceptions can be made by the user. No uninitiated inbound connection at all. Total stealth mode.


They forgot to add microsegment these critical servers from everything else internal. And add JITMFA with @ZeroNetworks 🤔

🔴 Kritik Uyarı: VMware ESXi ve vCenter sistemleri hacklenmeye başladı!
Dünya genelinde VMware ESXi ve vCenter Server sistemlerine yönelik fidye yazılımı saldırıları başladı. Saldırganların özellikle genel erişime açık vCenter sunucularını, son yayınlanan kritik güvenlik açıklarını kullanarak hedef aldığı ve bazı sistemlerde başarılı olduğu bildiriliyor. Ayrıca VMXNET3 açığı, ele geçirilen bir sanal makineden VM Escape ile ESXi host'a erişim riskini de beraberinde getiriyor.
👉 Öneriler:
* Son yayınlanan güvenlik patchlerini hemen uygulayın. İkisi de yayınlandı.
* vCenter'ı internet erişimine kapatın; yalnızca VPN veya yerel ağ üzerinden yönetin.
* ESXi ve vCenter loglarını şüpheli oturumlar açısından inceleyin.
* Güncelleme yapamıyorsanız, vm'lerde sanal ağ bağdaştırıcısı olarak VMXNET3 yerine E1000 yapın.

Next week. Meet me and real @ZeroNetworks customers at Black Hat booth #1852.
zeronetworks.com/landing/bla…
🤖 Made with AI

My favorite part of any event: watching customers teach each other things I can't.
At Black Hat, we're hosting a CISO panel — real security leaders on how they're building AI containment and cyber resilience. Not a pitch. Peer to peer.
Info: zeronetworks.com/landing/bla…
Sneak peek: our Black Hat booth.
Real customers, 1:1, telling you what it's actually like. No pitch, no gimmicks.
Skip the pitch, talk to a customer. Booth #1852.
zeronetworks.com/landing/bla…
🤖 Made with AI

Nicholas DiCola retweeted
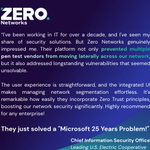
💙💚 "Zero Networks is one of the Firm's most critical security controls and plays a significant role in our Zero Trust architecture." 💙💚
👀 Get a no-BS review of our microsegmentation capabilities from a Manager, IT Security and Risk Management in the Services (non-Government): hubs.li/Q04pNjY70
🏄♀️ Or, skip ahead and kickstart your own effortless microseg journey - book a demo with our team → hubs.li/Q04pNlkV0

New term for the pile: "least agency" — OWASP's take on least privilege, but for AI agents. An agent should only touch what it's meant to. Not new. Just a new name for something we've solved at the network layer for years.
Something's coming at Black Hat 👀
Clearing this up: our customer bar isn't a bar with drinks.
Microsegmentation has always been brutally hard to actually finish. We built Zero to change that — and the product does what it says it does.
Booth focal point: real customers, real stories, no gimmicks. #1852 ask for me
Customer asked me last week: "How do I stop AI from talking to things it shouldn't?"
AI segmentation = network microsegmentation. If the network won't let it talk, it can't. OWASP just named this "least agency." We've called it microsegmentation.
Come see it at our booth at BH
