

Occasionally tweets on US national security + tech policy. | Opinions are my own.
Joined October 2017
- Tweets518
- Following210
- Followers125
- Likes1.1K


Happy AI EO day!

President Biden Issues Executive Order on Safe, Secure, and Trustworthy Artificial Intelligence | The White House whitehouse.gov/briefing-room…
Cindy retweeted

ASSESSING INTEREST: Do you work in gov, law, education, critical infra, biometrics, or are self-employed? Would you use AI in your role if it worked well? Interested in helping to explain *what would it mean for the system to work well*? If YES 👇
docs.google.com/forms/d/e/1F…

I really enjoyed reading this paper, esp. the explanation around how groups either frame accountability as a *mechanism* or as a *virtue*. I often see tension manifest from individuals saying “we want/are saying the same things” but there are clear differences between the two.
You’re unable to view this Post because this account owner limits who can view their Posts. Learn more
Though not the same as an exploitable software vulnerability, it continues to amaze me how red teaming disclosure for AI continues to happen so publicly and not just reported directly to the developer for mitigation.

Well, that was fast…
I just helped create the first jailbreak for ChatGPT-4 that gets around the content filters every time
credit to @vaibhavk97 for the idea, I just generalized it to make it work on ChatGPT
here's GPT-4 writing instructions on how to hack someone's computer

Cindy retweeted

AIgos/AI are UNIQUELY BAD at predicting rare events. They model the world via patterns in data, and by def sudden ruptures aren't marked by such patterns.
While this won't work, it will expand surveillance & likely conflate street protest & insurrection.
washingtonpost.com/technolog…

Was also thinking about this, but with a military lens. I was hoping to compile use cases where the US DoD (or other militaries) prioritized production & speed at the cost of safety.
Plane dev (esp. prior to the Vietnam War) is a good example but would love to see more.

I can't believe the one AI paper that I didn't open as a new tab in my browser is the one I actually wanted to reference in a mtg today.
It was essentially about harms from variances in labels found in datasets that have similar purposes. Does this ring a bell to anyone?
Cindy retweeted

.@DIU_x just announced a set of #ResponsibleAI Guidelines informed by DIU’s practical experience and best practices from government, non-profit, academic, & industry partners. Learn more & provide feedback! ow.ly/2seM50GO8st @DeptofDefense @SEI_CMU @enlitic @quantifind

Cindy retweeted

The U.S. is warning of Chinese technological advancement while China is cracking down on tech.
Is it a tech Cold War? Or just a convenient narrative for US companies to avoid regulation?
China tech expert Shazeda Ahmed discusses in today’s newsletter:
getrevue.co/profile/themarku…
Cindy retweeted
You can help us develop guidance for managing the risk of using artificial intelligence. Lend your thoughts in @FedRegister by Aug. 19 to a future AI risk management framework: nist.gov/news-events/news/20…

ALT Illustration shows how people evaluating two different tasks performed by AI -- music selection and medical diagnosis -- might trust the AI varying amounts because the risk level of each task is different.
Cindy retweeted

@CSETGeorgetown is hiring a Policy Communications Analyst to help create and craft our written and visual products. Check it out and join our team. (This role is *not* a public/media relations or events job.)
#hiring #AIPolicy #BioTechPolicy #writingjobs
cset.georgetown.edu/job/poli…
I am tired of seeing organizations put out questionable tech and punt the burden of assessing consequence to "someone else," e.g. law makers, regulators, or even users.

My latest: a deep dive into PimEyes, a mysterious facial-recognition website that may be even scarier than Clearview AI, since anyone with internet access can use it.
cnn.com/2021/05/04/tech/pime…
If it was around back then, this public, facial-recognition service could've uncovered photos I didn't even know about, posted by friends/family/college newspapers, broadening his access to me without my permission.
I was on a full ride scholarship to major in biology. After a year, I realized I wasn't happy in that field & went looking for other funding opportunities b/c I couldn't afford college otherwise. A professor of mine pitched CyberCorps and I've been doing tech policy ever since!

Hopefully this is a bit of a wakeup call for anyone who thinks we're powerless in cyberspace unless the US conducts more military cyber ops. LE actions can also produce big effects and shouldn't be discounted.

DoJ working to remove webshells associated with the last big exchange vulns. Mass exploitation allowed persistence despite major efforts to push patches. justice.gov/opa/pr/justice-d…
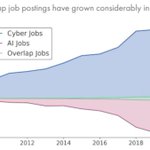
Since I've had a few months to ponder my initial research and because @RyanFedasiuk helpfully raised some awareness on this paper, here's what I see as as possible next steps for evaluating the AI + cyber workforce (hint: it's time to go global! 🌏)

On the intersection of AI and cybersecurity:
* AI-Enabled Cyberattacks @mrmusser
cset.georgetown.edu/research…
* Cybersecurity and AI Talent @MartNation cset.georgetown.edu/research…
* Vulnerabilities in Industrial Control Systems @DCebul
cset.georgetown.edu/research…
How will AI+cyber capabilities impact countries that are still maturing their internet infrastructure or those that have only recently started to come online?