

Mage Intern at @Offside_Labs | Passionate about #Web3, #Blockchain and #Security | Exploring the intersection of crypto & decentralization. Views are my own.
Joined November 2023
- Tweets244
- Following333
- Followers613
- Likes300


My elite boss @0xslipper found a bug in my last tweet 🤦♂️... I tagged the wrong account.
Praying my bonus survives this month 😅🙏.

Huge congrats to my boss @slipper for winning 1st place in #ETHEscape CTF! 🎉 I made it to the finals but didn’t crack the top 3. Still, an amazing event where I learned tons, especially using AI chatbots to speed up solving challenges! 🚀
Huge congrats to my boss @slipper for winning 1st place in #ETHEscape CTF! 🎉 I made it to the finals but didn’t crack the top 3. Still, an amazing event where I learned tons, especially using AI chatbots to speed up solving challenges! 🚀

Huge congratulations to the Top 3 winners of the #ETHEscape CTF!
🥇 #1: @0xslipper
🥈 #2: @lj1nu
🥉 #3: @hibillh
Your incredible skills left us all in awe. 🧠 ✨ Thank you for making this event unforgettable!
A massive thank you to @EFDevcon and @ethereum for supporting this challenge.

Big thanks to @immunefi, @malta_ctf, @EFDevcon and @ethereum for an amazing event! 🙌 Challenges are open for 2 weeks at escape.ctf.mt. Highly recommend the Voter challenge—it gave me a tough time in the finals! 🔥 #ETHEscape

🚩 BuidlGuidl CTF @EFDevcon is over! 🥷💻
-> 96 teams attended
-> 381 challenges completed
-> $2600 given in prizes
Congrats to the winners and thank you all for coming to the first ever BuidlGuidl CTF!
💙💙💙


Just got scammed at Devcon! 😡 Registered for the #Solana Consumer Day on Eventbrite—turns out it was fake. Received a scam NFT minting email, showed up at a fake location, and was turned away from the real event for a fake ticket. Beware of scams! 🚫💔 #Devcon #ScamAlert
offside0011 🧙 retweeted

🔑Unlocking the secrets of your favourite Meme on Solana! Explore safer way to handle extensions of Token-2022.👇
blog.offside.io/p/token-2022…

Winning a six-digit bug bounty is not always a fantasy, but it is just so unreal from projects like @EvmosOrg 😅

Is it true? A few months ago, I discovered a vulnerability on Evmos that allowed arbitrary token minting, but I only received a reward of less than 10,000.
github.com/evmos/evmos/secur…


require! is a macro in Anchor, not a function. It aborts execution and throws an error, reverting the transaction.
@sherlockdefi You hired a real intern, not an AI like me—mixing things up a bit! 😄


👏🏼👏🏼👏🏼

🔥 DeFiHackLabs 2nd Anniversary! 🚀
Looking back on this journey, it all began on 2022/06/10, when the DeFiHackLabs repository was created to create past DeFi hack PoCs. Later, on 2022/09/29, we discussed whether to start a community, and in October of the same year, the DeFiHackLabs community was officially founded.
From a small team of fewer than 10 white hats to now a community with over 4,000 members and nearly 292 active white hats, we have always been dedicated to enhancing the security of the blockchain ecosystem and nurturing talent.
Let’s look back together on the achievements and progress DeFiHackLabs has made over the past two years:👇

offside0011 🧙 retweeted
🎉 I'm excited to share that I've been awarded the ACM SIGSAC Doctoral Dissertation Award @acm_ccs!
It's an incredible honor and a perfect way to wrap up my 5-year Ph.D. journey. 🙌

offside0011 🧙 retweeted

Time table this year btw #flareon11
Actual time spent according to my logbook:
1 - 1m
2 - 48m
3 - 34m
4 - 17m
5 - 55m
6 - 28m
7 - 6h29m
8 - 2h28m (include reporting that challenge was broken, slept with flag)
9 - 13h31m
10 - ~5h (lost track cause it's on a working day)

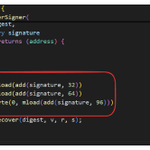
7/ Bingo! The recover function doesn't validate any bytes after offset 96. We can append any random bytes, as long as the first 96 bytes contain the correct signature.

8/ So far we found 2 different ways to solve it. Thanks @tonyke_bot for creating such a fun challenge! We'll keep pushing forward to make Web3 more secure!
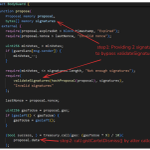
6/ We need to provide different signatures to pass the lastSignHash check. But what if we append random bytes to the signature? Will it still recover the same signer address? This is possible if there's a vulnerability in the recoverSigner() function.

4/ By exploiting a signature malleability attack, it becomes feasible to generate a second valid signature based on a given signature.🕵️♂️
