

Bitcoin education that doesn't suck. Learn Bitcoin: The Journey, Rabbit Holes, Glossary. Free. Ad-free. No Tracking. Open source. Bitcoin only. No bullshit.
Joined October 2023
- Tweets810
- Following1
- Followers348
- Likes409


Bitcoin Core 32.0 was tagged final yesterday.
What changes for regular node runners:
- fee estimates now also read the live mempool, and can only come out lower, so less overpaying on quiet days
- blocks validate faster (inputs fetched in parallel)
room for 200 peers, up from 125
- two security fixes, including an IP leak in private broadcast
No consensus changes, no soft fork. Waiting for the binaries and a .1.
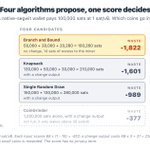
New chapter: Which Coins Does Your Wallet Spend?
Your wallet has no balance. It has a bag of coins, and every payment starts by picking which to spend. What the pick costs now and later, what it tells a chain analyst, and how Bitcoin Core decides.
learnbitcoin.com/rabbit-hole…

What the score can't see: a reused address is linked the moment it is paid, before any selection runs. Core's avoid_reuse flag filters one command.
The wallet's own authors, in the CoinGrinder PR: it still lacks metrics "on basis of their privacy and wallet health impact".
Full chapter, sourced (53 sources), free, no ads, no wallet recommendations:
learnbitcoin.com/rabbit-hole…
Spot a wrong number or quote? Reply here and it gets fixed, with credit.

If you run the mempool explorer from its published Docker images: the backend still bundles Node 24.13.0, which predates the Oct 20 Node.js security release (24.22.1). An upstream PR is waiting on the maintainers. Until a new image ships, three lines put the patched Node into the current one 👇
PHP2Shell was patched today (PHP 8.5.12 / 8.4.27).
Bitcoin itself isn’t affected: nodes and wallets don’t run PHP. Bitcoin websites can be. Plenty of shops, donation pages and forums run on WordPress and other PHP software.
The risk to you is a hacked checkout page quietly swapping the address. For anything large, confirm the address with the recipient another way before you send.
Thanks to @lopp for sounding the alarm
LearnBitcoin.com retweeted
🚨DEFCON 1🚨
In a few hours, a critical vulnerability that affects ~70% of web sites will be disclosed. It allows an attacker to upload and execute arbitrary code.
It's probably best if you stop browsing the internet for the rest of the week.
xitter.cf/ThePHPF/status/2112633…

The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
Readers added context they thought people might want to know
These are server-side PHP RCE vulnerabilities for which web hosts/admins should prepare to patch per official notice; general users face no direct need to stop browsing. PHP detected on ~69% of sites with known server-side language.
php.net/archive/2026.p…
w3techs.com/technologies/d…
cert.europa.eu/publications/s…
sansec.io/research/php2s…
arstechnica.com/security/2026/…
Jamie's long held and inaccurate bitcoin declarations: learnbitcoin.com/rabbit-hole…


The first Ordinals inscription is a 793-byte PNG that’s sat in block 767,430 since December 2022. No new opcode or consensus change needed, just a way to number sats and some data in the Taproot witness. The node queries behind it: chainquery.com/stories/ordin…

Bitcoin's private key space is so extraordinarily large that even if you could test trillions of private keys every second, for billions of years, you would have explored essentially none of it.
We brute-forced two vanity addresses on a laptop CPU this week.
1LearnBTC, any letter case: 46 minutes.
bc1qlearn8tc: 6 hours 1 minute.
Same eight chosen characters. Bech32 has no upper or lower case to lean on, so the average job was 2.7x bigger. Luck did the rest.

The rewritten glossary entry: what a prefix costs, why bc1qlearnbtc can never exist (the bech32 alphabet has no b), and how split-key generation lets someone else do the searching without ever holding your key.
learnbitcoin.com/glossary/va…
