

Kaizen
127.0.0.1
Joined August 2022
- Tweets930
- Following1K
- Followers363
- Likes9.5K
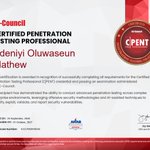





I got certified by @ECCOUNCIL as a Certified Penetration Testing Professional (C|PENT)

Oluwaseun 🌐💻 retweeted

Your next INE certification is 25% off. 🔥
Save on standalone certification vouchers: 👉 bit.ly/4drPMns Code: SEP2625EXAM
Choose your next certification and put your skills to the test.
*New voucher purchases only. ICCA excluded. Vouchers expire in 180 days.

Oluwaseun 🌐💻 retweeted

🚨 GIVEAWAY TIME 🚨
I’m giving away 1× lifetime access to the Pwned Labs Kubernetes Attack & Defense Bootcamp (KRTP)!
Get hands-on with Kubernetes security from local k8s to EKS, GKE, and AKS. Plus the KRTP certification exam path.
To enter:
Like this post ❤️
Repost 🔁
Tag 1 friend who should learn Kubernetes attack & defense 👇
🔗 pwnedlabs.io/bootcamps/krtp-…
The winner will be picked at random.
Good luck! 🚀

Oluwaseun 🌐💻 retweeted

I’ll give a free seat to one person that retweets and responds to this tweet with a 🧑🏽💻

Very excited to see @wunderwuzzi23’s course go live on @hackinghub_io. We are only launching a small cohort to get feedback before opening it up to the general public. So if you want to get it at a discounted price this is your chance. hhub.io/AI2026

Oluwaseun 🌐💻 retweeted

HackerSummer is back! I am excited to announce @AlteredSecurity HackerSummer 2026. Get ready for talks and research blog posts on on-prem and Azure Red Team, giveaways and discounts. More details here - alteredsecurity.com/hacker-s…
This year we are introducing two community sessions - 45 minutes each. Respond to the HackerSummer CFP. Selected speakers get $500 honorarium and any course from our course catalogue. Link to the CFP - alteredsecurity.com/call-for…
#RedTeam #Azure #HackerSummer

Oluwaseun 🌐💻 retweeted

Hacking Google with A.I. for $500,000
brutecat.com/r/hacking-googl…
Oluwaseun 🌐💻 retweeted

Time for another giveaway!
We will pick 6 winners to win one of the following:
1x Annual VIP @hackthebox_eu Licence
5x @PentesterLab 3 Month Licences
To enter:
1️⃣ Follow us @BugBountyDefcon
2️⃣ Like this post ❤️
3️⃣ Re-tweet this post 🔁
Giveaway open until Monday June 15th! GOOD LUCK!

Oluwaseun 🌐💻 retweeted
Bootcamp Giveaway
We're giving away 1 CARTP® Bootcamp seat and 1 CRTP® Bootcamp seat to two participants.
Join live, hands-on training in Azure Red Teaming or Active Directory security.
How to participate:
• Like & follow us
• Comment your preferred bootcamp and why
• Repost
Winners announced June 4, 2026
Limited-Time Bonus:
Enroll in CARTP® (Starts June 5) or CRTP® (Starts June 6) and get 10 extra days of lab access (worth $150+).
Applicable for the first 30 purchases only.
alteredsecurity.com/bootcamp…
#CyberSecurity #RedTeaming #InfoSec #AlteredSecurity

Oluwaseun 🌐💻 retweeted

New banger from @thefosi: HTTP/2 framing WAF bypasses across six proxies.
Use it wisely while you can. :p
lab.ctbb.show/research/h2-WA…


Oluwaseun 🌐💻 retweeted

🚨Cyber Alert ‼️
🇳🇬Nigeria - 𝗡𝗡𝗣𝗖 𝗛𝗲𝗮𝗹𝘁𝗵 𝗠𝗮𝗶𝗻𝘁𝗲𝗻𝗮𝗻𝗰𝗲 𝗢𝗿𝗴𝗮𝗻𝗶𝘀𝗮𝘁𝗶𝗼𝗻
XP95 hacking group claims to have breached NNPC Health Maintenance Organisation.
Threat actor: XP95
Sector: Financial / Insurance
Data exposure (claimed): 200,000 user records
Data type: Personal data
Observed: Apr 08, 2026
Status: Pending verification
ESIX©: 5.73
Full details and impact assessment on HackRisk.io

Oluwaseun 🌐💻 retweeted

Malware Analysis Tutorials: a Reverse Engineering Approach
fumalwareanalysis.blogspot.c…

Oluwaseun 🌐💻 retweeted
🚨Cyber Alert ‼️
🇳🇬Nigeria - 𝗜𝗻𝗱𝘂𝘀𝘁𝗿𝗶𝗮𝗹 𝗧𝗿𝗮𝗶𝗻𝗶𝗻𝗴 𝗙𝘂𝗻𝗱 (𝗜𝗧𝗙)
NormalLeVrai claims to have breached an Industrial Training Fund employee’s email, allegedly accessing 92 government files including emails, financial records (2019–2026 salaries), budgets, internal documents, and employee/contact data.
Threat actor: NormalLeVrai
Sector: Gov / Mil / LE
Data exposure (claimed): Not specified
Data type: Emails, financial records and employee data
Observed: Apr 2, 2026
Status: Pending verification
ESIX©: 5.79
Full details and impact assessment on HackRisk.io

Oluwaseun 🌐💻 retweeted

I finished the Hack the Box COAE cert the day it came out (by about an hour lol) report and all, really was going for first globally. Gonna be close if nothing else!
Review coming next week for the cert portion. If you’re interested in a review of the ai red teaming course that is already live on my personal website.
I Throughly enjoyed the course and test, saying it opened my mind to a deeper level of systems thinking overall would not be an under statement.


Oluwaseun 🌐💻 retweeted

FCMB: Sophisticated API exploitation resulted in the successful siphoning of ₦677 million from a ₦3.5 billion fraudulent attempt.
Sterling Bank: A critical middleware vulnerability enabled the exfiltration of sensitive PII for over 900,000 customers.
Remita: A massive cloud misconfiguration exposed 3TB of archival data, including transaction logs and infrastructure blueprints.
Here is a clean technical breakdown of these incidents:
1. FCMB: The ₦3.5 Billion Heist
This was a logic based exploitation of the bank's digital transaction pipeline
Attackers identified a flaw in the API reconciliation layer, specifically involving the Payattitude integration
By exploiting this vulnerability, hackers initiated transactions that the system validated as successful even though the source accounts were unfunded. This is known as a Zero Balance or Double Spend exploit.
While the system eventually flagged the anomaly at the ₦3.5 billion mark, the latency in the bank's real-time fraud monitoring allowed ₦677 million to be successfully routed to mule accounts and withdrawn before the kill switch was activated.
2. Sterling Bank: The 900k+ Record Exfiltration
This event was kinda like a Network Intrusion targeted at customer identity data, allegedly carried out by the threat actor ByteToBreach.
The breach targeted a critical vulnerability in the Oracle WebLogic Server. This middleware sits between the public facing applications and the bank’s private databases.
Attackers bypassed authentication to extract roughly 2.2 GB of data.
The data contained Personally Identifiable Information (PII) for over 900,000 customers, including names, contact details, and internal Customer Information File (CIF) numbers. This data is highly valuable for "Social Engineering 2.0, where scammers use real account details to trick victims into revealing OTPs or other lateral valuable infos
3. Remita: The 3TB S3 Infrastructure Exposure
This was a Critical Cloud Misconfiguration representing one of the largest infrastructure level exposures in the Nigerian fintech space
A massive Amazon S3 Bucket (Cloud Storage) was left in a Public Read state. This meant the data was accessible to anyone with the endpoint URL, requiring no hacking tools or passwords to download
The volume 3 Terabytes indicates an entire archival Data Lake was exposed. This typically includes millions of individual files and logs accumulated over years
800GB+ of KYC Documents, Massive troves of sensitive personal data, including Passports, Government IDs, Bank Statements, and Utility Bills
Core Databases: Full exports of MySQL and Postgres databases, including three primary databases and over 35,000+ password hashes
The Master Keys: Exposure of Government HSM (Hardware Security Module) keys, which are used to encrypt and authorize high-level financial transactions
Developer Blueprints: Source code, Docker registries, and GitKraken-to-S3 backups, providing a literal how-to guide for attackers to find further vulnerabilities in the system's logic
The exposure included transaction archives, RRR (Remita Retrieval Reference) metadata, and internal system logs. Most dangerously, logs of this size often leak secrets such as API keys and session tokens, which provide a roadmap for attackers to move laterally into other connected financial systems
what can we do
🤖 Made with AI

Oluwaseun 🌐💻 retweeted

‼️🇳🇬 A massive breach allegedly from Remita, a major Nigerian payment processing platform, has been leaked on a popular cybercrime forum.
▪️ Total Size: ~3TB of S3 storage
▪️ Data Includes: 800GB+ of KYC documents (IDs, passports, photos, bank statements, electricity bills), MySQL/Postgres databases, logs, docker registries, source codes, government HSM keys, GitKraken to S3 backups
▪️ Source codes, 35,000+ password hashes, and three databases

Oluwaseun 🌐💻 retweeted
🚨Cyber Alert ‼️
🇳🇬Nigeria - 𝗦𝘁𝗲𝗿𝗹𝗶𝗻𝗴 𝗕𝗮𝗻𝗸 𝗟𝘁𝗱
Threat actor ByteToBreach claims to have breached Sterling Bank Ltd, alleging the compromise of customer and employee data linked to approximately 900,000 accounts and over 3,000 staff.
Threat actor: ByteToBreach
Sector: Financial / Insurance
Data exposure (claimed): 900,000 customer accounts and 3,000 employee records
Data type: Banking records, identity documents (BVN, NUBAN, passport and driver’s licence), transaction histories, loan records, credit scores, and employee data
Observed: Mar 27, 2026
Status: Pending verification
ESIX©: 6.18
Full details and impact assessment on HackRisk.io

Oluwaseun 🌐💻 retweeted
Cybersecurity is not about what you know, it is about what you can do 🔐
👉 Limited-time offers: bit.ly/4bAakbY
Build real skills with hands-on labs and certification prep before March 26.
#CyberSecurity #InfoSec #TechSkills
