





十几年前跟着我爸拜访他的表姑妈。
爸的表姑丈以前是教师,在文革时间被打断了腿,落下了终生残疾。
那天聊着聊着,我就提到毛泽东其实没宣传得那么伟大,搞得太多人受罪了。
本意是替表姑丈诉苦一下,跟老人随意聊聊天。
原本温和笑着的表姑妈突然变脸,扯高嗓门说:我不许你这样说毛主席,他是我最尊敬的人了,你小孩懂什么!没有他,我们… (说了一堆,我忘了)
我只能说,对对对,没有再和她争辩。
作为90后,这是我感受最深的一次老毛崇拜。
虽然老视频上有更夸张的画面,但那毕竟是隔着屏幕。
距离只有不到2米的活人大变脸,而且是熟悉的人突然像变了个人似的,给我的印象特别深刻。

真正值得人们深思的问题是:毛泽东这尊偶像,不只在党里,更在中国人的心里。。。改革开放之后,邓小平曾经非常卖力清楚毛泽东个人崇拜的影响,甚至红宝书成为了禁书,国营书店不许贩卖。很多人不知道的是,邓小平曾一度想摘下天安门上老毛的画像。试行了一段时间,结果北京民情汹涌,邓小平一看形势不对,只得称维修维护,又挂了上去。我家老人文革遭大罪了,但是他在邓小平摘下天安门画像一事上发飙了,破口大骂邓小平,而且他不是孤例。我也搞不清楚是斯德哥尔摩综合症还是别的原因。但我曾觉得再过几十年,彻底摆脱文革影响的一代人,可能就会改变。谁知道,现在中国的年轻人更加认同老毛这尊偶像。所以你们看这个事件,民间的反应和划清界限要远远早于、甚于官方表态。关于拜偶像的问题,我还有很多要说,之后再说吧。
StandX 官宣关停:不发币,最后用一次 $DUSD 空投谢幕。
没拿 VC 的钱,TVL 最高到过 $2 亿,但没做到永续合约 DEX 前三。创始人说,靠炒作发币,代价会留给用户,所以选择体面退场。
关键时间(UTC):
🔹 10/15:所有收益停止,金库关闭
🔹 10/20:合约只能减仓,停止新注册
🔹 10/26:空投查询上线
🔹 11/1–12/31:领取 DUSD,无锁仓,逾期作废
🔹 2027/1/15:剩余仓位按标记价格强平
🔹 2027/1/31:提现和赎回截止
空投来自平台剩余收入加团队自掏腰包,但总额没有公布,23.7 万用户一起分,预期别太高。
预存款阶段我在积分榜排进了前十。可是按现在的规则,大部分收入早就通过 SIP-2 和 SIP-3 补贴发掉了,剩下的钱再按预存款、交易、做市、推荐摊给所有人,我估计也分不到多少。几个月的资金占用和时间成本,大概只换回一点点DUSD。
还有资金在里面的,尽早平仓提现,领取只认官网 standx.com。
一个没有收割用户的结局,在永续合约赛道里少见,但也说明这条赛道有多残酷。


We have an important update to share.
StandX will airdrop $DUSD with no lockup and will not proceed with a token launch.
Airdrop claims open November 1 and close December 31. Perps moves to Reduce-Only on October 20. Positions close January 15.
Withdrawals and redemptions close January 31.
Full announcement article in the next tweet.


可能是这条推文触发了黑客快速动手。
两天前,Mt. Gox 前 CEO 就披露了硬件钱包疑似被植入窃密装置。
一台外观看似正常的 Ledger 硬件钱包,内部却可能藏着能够读取并外传助记词的装置。Mt. Gox 前首席执行官 Mark Karpelès 近日披露,他收到的一台来自马来西亚的设备疑似遭到改装:包装热缩膜没有明显破损,而可疑模块被嵌入屏幕后方、原本用于放置缓冲垫的空间,隐蔽程度较高。
据 Karpelès 分析,植入装置配备了 LTE 通信模块、天线和 eSIM,并通过微控制器接入钱包的 SPI 总线。其窃密方式是监听传往屏幕的数据,识别设备显示的字符,从而在用户初始化钱包、记录助记词的过程中获取相关内容,再借助移动网络将数据传出。

Need free data? Buy a cheap ledger off a dodgy seller, pull the sim out of the spy implant and enjoy while you can (law enforcement may visit you thinking you are the one making these).
xitter.cf/AliceInDisarray/status…

AI agents 太多了。人类快不够用了。

Announcing dots. Dots work 24/7 for you, learn from your feedback, have their own computer, browser and can be connected to over 4k apps in our ecosystem.
They’re powered by Astra our best model yet. Included in your Pro plan, without drawing down on any of your usage. You can even call a dot while it’s working.
We’re getting you started with your primary dot today and soon you’ll be able to create entire teams of them.

Bitget的冷钱包都直接转币出去了,应该是被黑了。
能提款的先提款吧,确认没事再存回去。

Bitget Wallets Suspected of Security Breach, Over $170M in Assets Moved and Swapped to ETH
Breaking: MLM monitoring indicates that Bitget may be experiencing an ongoing wallet security incident, with three hot wallets and one cold wallet suspected to have been compromised. More than $170 million worth of assets have reportedly been moved out and swapped into ETH, with activity linked to 0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee. The affected wallets are said to still hold about $530 million in assets. The attack vector and total losses remain unconfirmed, and Bitget has not yet publicly responded.

qclaw被下架了,毫不意外。
qclaw就是移动事业群里的一个部门的一个小组的创新产品。其实小问题还是很多的。
work buddy是云服务事业群的主力产品。
层级决定了资源,如果发起的人是移动事业群的老大,qclaw可能就是今天的muse了。

看到几个博主发腾讯的qclaw,现在看到已经被暂停下载了,我来说说可能的原因。
你们观察一下首页,这里面最有意思的一点是,有个小字标识这个产品是腾讯手机管家的出品。这个是我待了6年的部门,里面还是有些门门道道的。
当年,腾讯为什么要做手机安全?因为十多年前发生了著名的3Q大战,他们要防御360,防止360在移动互联网颠覆腾讯。所以腾讯手机管家来源于,腾讯收购广州的一个安全创始公司,并合并到MIG而来的。
但是,腾讯手机管家不想只做防御,创始团队还是有雄心的,在微信还没出来时就开发了一款Q信,主攻移动互联网的即时通信。是不是很像现在的qclaw?但后来被微信打败了。Q信这个产品也关停了。
后续发生了很多事,进行了非常多的内部创新,都失败了。另外主营业务开始崩塌,主要是手机都内置了安全应用,腾讯手机管家滑落成一个非常边缘的部门。很多核心员工被离职了,留在里面的人为了证明自己的价值依然在不停“内部创新”,不然就有可能继续被离职。
腾讯手机管家招的人很多都是中大华工的计算机本硕,能力是绝对没问题的。问题是,这只是一个小部门孵化的产品,官网还只挂在手管而不是腾讯的网页下。
这个qclaw就是一个“内部创新”的产品,接入的还是Kimi2.5,而不是接入元宝。他们的资源是很少的,唯一的优势就是跟微信一起在广州办公吧,可能对接微信会方便一点。
马化腾重视起来的话,不会交给一个边缘部门操作,最终应该会是集团战略级产品。qclaw很可能会沦为下一个Q信,作为先卡住其他竞争对手陪跑的产品。之后让路给真的如weclaw之类的核心产品。我估计现在腾讯有不少于三个团队自己在孵化claw了,只是手管先发了出来。
希望腾讯手机管家部门这次能把AI agent做起来吧,在内部赛马中击败其他claw。大家有的是能力,缺的只是一飞冲天的机会。

I was pretty late to deposit into @fablesfi, but I still managed to break into the top 10.
Here’s my lightweight audit of the project. The Fables founder @0xlayans also replied in the thread, outlining the improvements they plan to make.
Deposit now, and you’ll be eligible for rewards at TGE in less than two weeks.
Feel free to use my referral code:
fables.fi/r/bwwxrm
@RobinhoodCrypto
robinhood:0xb9972ca7188e511174947e3936a5315ac7073277 #RobinhoodChain #DeFi #RWA

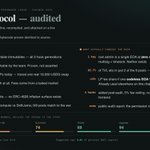
I spent a short auditing @fablesfi — the hook-native ve(3,3) DEX on Robinhood Chain — from scratch.
Not a checklist review. Every deployed hook read line by line, recompiled locally to prove the bytecode matches, then attacked on a live mainnet fork with 37 adversarial tests.
The short version: the contract engineering is genuinely better than most of what I review. What should worry you is almost entirely somewhere else.
Full breakdown 🧵
@RobinhoodCrypto $PROLOGUE #RobinhoodChain #DeFi #RWA #UniswapV4 #ve33 #SmartContractSecurity #DeFiSecurity #TokenizedStocks

什么傻逼恶心项目方。
用户只能接受霸王条款拿回一半钱,or,一分钱也拿不回来。
怎么亏的,不说。
钱去哪了,不知道。
这在传统金融,可是要去坐牢的。
还是区块链好啊,过几个月就能下个项目见了。
就是有太多这种项目方,Defi才会如此凋零。

NUSD and sNUSD holders may now submit redemption requests through the official Neutrl Redemption Portal subject to the applicable terms and conditions.
The Redemption Program provides NUSD and sNUSD holders with a fixed redemption rate based on Neutrl’s previously disclosed liquid reserves. Users who complete a redemption will receive USDC, and the corresponding NUSD or sNUSD will be burned.
To submit a redemption request, users must connect the wallet holding their NUSD or sNUSD and sign an onchain message to verify ownership of the wallet. The portal will provide the applicable redemption details before a redemption is submitted.
The Redemption Program is expected to remain open until 14 November 2026, subject to the applicable terms and conditions. Users are encouraged to carefully review the full terms and conditions available on the Redemption Portal before submitting a redemption request.
The redemption contract has been reviewed by a third-party security auditor. Users should verify that they are interacting only with the official Neutrl Redemption Portal URL before connecting a wallet, signing a message, or submitting a transaction.
redeem.neutrl.finance/
Disclaimer: Neutrl is operated by Caverna Auctus Inc. This communication contains forward-looking statements, including as to timing, amounts, and recovery outcomes, which are estimates only and subject to change without notice. Nothing herein constitutes a guarantee of any specific outcome, financial, investment, or legal advice, or an offer or solicitation with respect to any token. All rights reserved.
这份报告比所有财务报告和新闻都能管中窥豹。
可以窥见,以后所有政府和相关机构都要利用AI来处理黑客攻防、海量数据分析、各种智能监控和研发武器等。
按维稳国防经费算,以后起码一半的国防经费得采购AI。
AI牛市,远未到顶。

We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: anthropic.com/threat-intelli…

I spent a short auditing @fablesfi — the hook-native ve(3,3) DEX on Robinhood Chain — from scratch.
Not a checklist review. Every deployed hook read line by line, recompiled locally to prove the bytecode matches, then attacked on a live mainnet fork with 37 adversarial tests.
The short version: the contract engineering is genuinely better than most of what I review. What should worry you is almost entirely somewhere else.
Full breakdown 🧵
@RobinhoodCrypto $PROLOGUE #RobinhoodChain #DeFi #RWA #UniswapV4 #ve33 #SmartContractSecurity #DeFiSecurity #TokenizedStocks
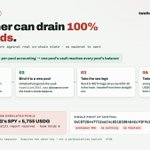
What actually carries the risk:
▸ The root admin is a single EOA with an EIP-7702 delegation, execution delay ZERO. It can grant itself every operations role in one transaction. I simulated it against live state and it succeeds. The docs' own role table says "Admin multisig, configured AccessManager delay." On chain it is neither a multisig nor delayed.
▸ The team clearly knows how to run a multisig: there's a 2-of-3 Safe. They use it to guard the rewards pot, not the protocol. That's a configuration choice, not a limitation. Two transactions would fix it.
▸ The finding I initially under-rated, then promoted: PoolManager.protocolFeeController resolves to an owner that is a CODELESS EOA. No multisig, no timelock, no relationship to Fables governance at all. At the v4 cap it takes 0.1% off every swap, cutting the LP fee share to 33-44%. This is not hypothetical. It is already switched on for another pool on this chain.
▸ Four new hooks were deployed after my audit began, now serving 13 pools, with a 5% fee ceiling (2.5x the audited ones) and, verified today, no AccessManager admin timelock at all, where the nine audited hooks have 3600s. They hold only team seed capital and the frontend doesn't list them. Yet.
I'm deliberately not collapsing this into one number, because the spread is the finding:
Code security 88
Upgrade risk 94 hooks are immutable. No proxy, no beacon, no delegatecall
Oracle risk 88 there is no oracle to attack
Economic 74
External deps 45
Admin risk 42 one key, zero delay
Attacker holding no keys: I found no path to principal.
Malicious team: 0% of principal, up to 20% of fees.
Suggested cap if you LP here: 2-4% of personal DeFi capital.
基本复核了Robinhood Chain的所有新Defi,没有一个买得下手的。
有完全是奔着Rug pull来的团队,匿名+随时可取本金。 $two $bow
有估值5千万u但存款只有50万,被各大割吹捧是yfi降临的。 $shroom
有明明是Defi项目,却发了个meme币,然后说meme币只能在tge时兑换2.5%项目代币,但其meme币已经市值上千万u的泡沫项目。 $prologue
Robinhood Chain的新Defi最大问题是,核心基础设施已经被老牌项目卡位了。只能从边边角角找些弱需求项目。
而且,Defi老人都被黑客搞得ptsd了,不是官方或老牌项目,基本都不会尝鲜存钱了。
现在最值得买的反而是 $pendle ,刚迁移到Robinhood Chain,基本面强,估值合理,凸性够高。
@pendle_fi
$PONS $PSDQ $PAIR $PROLOGUE $FABLES $BOW $TWO $UP $EARN base:0x2a0a59d6b975828e781ecac125dba40d7ee5ddc0 ethereum:0x808507121b80c02388fad14726482e061b8da827 solana:63LfDmNb3MQ8mw9MtZ2To9bEA2M71kZUUGq5tiJxcqj9 $RAM $INDEX solana:BCzBBz5c6fCcRU7UjdJxszaECh7FdnU551MoQewpQv7L $LEGS base:0xa15d5c95b7c0eecac06f673ad390ad6066705af7 $NEKO solana:3PKk38cMrPQ1HR5HH96gWYTsH3TgEn78eC8x6uqSpump $YETF $FILL $9TO5 $PACK monad:native solana:61Wj56QgGyyB966T7YsMzEAKRLcMvJpDbPzjkrCZc4Bi $ROHM solana:GMkWVrn6A4anxwBqsN5ofk3SjyabYTtQUKpk8c3iKinG $SHROOM $PARE $MERA $VOXEL $ORDO $SYNDROMICS $MURI solana:4VnaCje2AUzyWUKJDtwmpFjzewE4bx2B6Ha4HgS4pump $BAG $SLV $OTER $STOCKKIT $AOBS $OBS $QSTRAT $SEMI solana:Gbu7JAKhTVtGyRryg8cYPiKNhonXpUqbrZuCDjfUpump $ORBIO $PONSBALL $PORT $BALIN $GREEN

🧵 Longbow (Robinhood Chain) — spot-oracle exploit, technical post-mortem + still-open advisory
1/
🚨 Security advisory for @longbowlend
The NOTHING market on Longbow was drained via spot-oracle price manipulation. The root cause is a design choice in the market's oracle — and as of Robinhood Chain block 55,530,002 it is still not fixed.
Full on-chain breakdown 👇 #DeFiSecurity
2/
The oracle. Market NOTHING (id 0x071fb8a9…f4b0be) is priced by
0x0F932e0fE68B0219820ffcB4C2B1906E29BedacC.
Disassembling it: it reads a Uniswap v4 pool slot0 directly via extsload. No observe(), no TWAP. Longbow's own API labels its oracleType: "spot".
3/
Why that's fatal. Morpho Blue calls oracle.price() inside both borrow and liquidate. An instantaneous AMM spot price is movable within a single transaction, so the collateral valuation can be inflated and deflated atomically by the same caller. This is the textbook spot-oracle failure.
4/
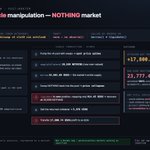
The attack — tx 0x414b5b7c832b67dcd0c3f16907c8702ff794ce9dd0b749d0100e7549ba202d49 (a contract-creation whose constructor ran the whole thing atomically):
① pump the v4 pool
② supplyCollateral 20,599 NOTHING
③ borrow 24,691.89 USDG
④ dump NOTHING back into the pool
5/
⑤ liquidate its own position, repaying only 914.45 USDG → Morpho returns all 20,599 NOTHING to the liquidator (= attacker)
⑥ sell the returned collateral
⑦ net 17,800.74 USDG to an EOA
badDebtAssets written off: 23,777.45 USDG.
6/
Where the loss landed. The bad debt was socialized 100% onto the MonkeyHood / Partner VaultV2 0x19d55f7FE2d3962796F5825CbDae2dd493Be0986, which held 100% of that market's supply shares. The vault realized a ~95% write-down that has not recovered since.
7/
⚠️ STILL OPEN — verified today at block 55,530,002:
• oracle address unchanged (still the extsload/slot0 contract)
• vault collateralToken cap still 50,000 USDG (not zeroed)
• price() still live & manipulable
• no remediation tx — only a 414 USDG adapter withdrawal since
8/
Fairness / scope: this is NOT a Morpho bug. @MorphoLabs markets are permissionless and behaving exactly as specified, and Morpho's own oracle guidance warns against raw AMM spot feeds. The vulnerable decision is Longbow's: a spot oracle wired to a live market with a non-zero cap.
9/
The rest of Longbow is not exposed to this vector — the other 54 markets use Uniswap V3 TWAP (e.g. PONS, backed by a deep pool w/ observationCardinality 20,000) or Chainlink feeds. NOTHING is the only market reading a raw spot price. But one open market is enough.
10/
Actionable asks for @longbowlend:
1️⃣ set the NOTHING collateralToken cap to 0 (stops new allocation immediately, no timelock)
2️⃣ retire/replace the oracle with a TWAP or Chainlink feed
3️⃣ audit every market's oracle bytecode for slot0/extsload vs observe()/latestRoundData
11/
cc curators & ecosystem for visibility: @SteakhouseFi @robinhoodcrypto @ponsdotfamily
Read-only analysis, no funds touched, all reasoning reproduced on a mainnet fork. Reproducible IOCs above.
#DeFi #RobinhoodChain #bow
