

https://xitter.cf/t.co/42tIk8kfrZ
Joined July 2011
- Tweets1.2K
- Following868
- Followers592
- Likes17.6K






Pinned Tweet
A bit of news, I’m making the big leap from Belfast to London
Really grateful for all the friends, family, cyber geeks and my work for supporting me ❤️
If you’re devastated by the thought of me not being around, you’ve not gotten away that easily, I’m back once a month! 😁

James Matchett 🔜 bsky retweeted

> be JayTaelien
> security researcher
> discovered Discord zero day exploit
> send Twitch embed to victim
> something something
> massive exploit chain
> arbitrary code execution
> only requirement is victim clicking a Twitch embed
> Discord confirms 1 ClickRCE
> pays him $5,500
Dawg, someone get Discord on the horn and tell their CEO his company is a fucking piece of shit. This exploit is devastating and if this guy didn't tell them, and instead decided to weaponize it, he could have fucking destroyed end users.
All bro would have had to do is be like. "Check out this Twitch streamers clip", and destroyed their machine, executing any malware they wanted arbitrarily, stealing data, whatever.
Bro could have gone to large Discord channels, shared the link, potentially infecting thousands upon thousands of people effortlessly
He could have down more precise operations targeting prominent streamers, moderators, celebrities known to use Discord, and fucking wiped them all out with anything he chose to execute
Imagine if he sold this exploit to ransomware groups
He could have made millions of dollars, easily
Imagine if he went into a cryptocurrency Discord and the payload was a cryptodrainer. He could have drained entire communities in seconds
And they paid bro $5,500
That's absolutely sickening. JayTaelien is a fucking saint and decides a much larger payouf
James Matchett 🔜 bsky retweeted

BA responded to my claim with "the aircraft...had to divert to London Stansted Airport due to wind conditions at London City Airport ... you’re not eligible for compensation". Where did you get the information about the flight to Nice with the same aircraft?
Really nice of @British_Airways to cancel my flight to Belfast so they can instead put on a better paying flight to Nice with the same aircraft
Looks like I’m in the airport for another 6 hours

James Matchett 🔜 bsky retweeted
Meta and Russian Yandex engaged in unprecedented internet tracking practices, likely illegal with EU data protection law. Companies designed tracking systems that exploited Android's localhost socket permissions to create covert communication channels between websites and native mobile apps, bypassing Android's app sandboxing protections. Android allows any app with internet permission to listen on localhost ports without user consent, and web browsers can access these localhost interfaces. When users visit websites containing Meta Pixel or Yandex Metrica scripts, the JavaScript tracking code sends data directly to specific localhost ports (Meta uses UDP ports 12580-12585 via WebRTC, Yandex uses TCP ports 29009-30103 via HTTP). Facebook, Instagram, and Yandex apps run background services that actively listen on these predetermined ports to receive tracking data, then link this anonymous web activity to authenticated user accounts and transmit the combined data to company servers.
This technique affects billions of Android users and renders privacy protections like incognito mode, VPNs, and cookie clearing completely ineffective. Meta Pixel attempted localhost communications on over 17,000 of the top 100,000 websites, with 78% doing so without user consent. The method allows comprehensive profile building linking anonymous browsing to real identities, tracking everything from shopping to sensitive site visits. It also creates vulnerabilities where malicious apps could eavesdrop on browsing history by listening on the same localhost ports.
This surveillance operated without disclosure. Following public disclosure, Meta immediately ceased the practice and removed related code while browser vendors scrambled to implement protections.
The practice violates multiple GDPR and ePrivacy principles. The technique transforms supposedly anonymous first-party cookies into cross-site tracking identifiers without explicit consent, violating ePrivacy Directive requirements for cookie consent and GDPR's lawful basis for processing. By secretly linking web browsing to app-based identities, it constitutes undisclosed profiling that undermines user expectations and data minimization principles. This is a material for max #GDPR fine. localmess.github.io/


James Matchett 🔜 bsky retweeted

Our fundraising quiz is proving to be popular! Thanks to everyone who came along - we had to find more chairs!
Huge thanks to @larianstudios for gifting us keys to @baldursgate3 for our raffle! Also to @comicbookguysni and @replaybangor - thank you 🎮♥️
#IVGO #vgm #gaming
Anyone in the infosec sphere potentially selling a ticket for @BSidesDublin
May procrastination has once again come to bite me 😁😁
Thanks all!
James Matchett 🔜 bsky retweeted

Meet the new team.
We’re delighted to welcome three new leaders to scale and solidify our support for the enterprise market.
Welcome to the team!
#SoftwareSupplyChain #ArtifactManagement #DevOps

James Matchett 🔜 bsky retweeted
Poland now has the largest quantum key distribution network in Europe, and second after China. Pionier-Q – 1 770 km.


James Matchett 🔜 bsky retweeted
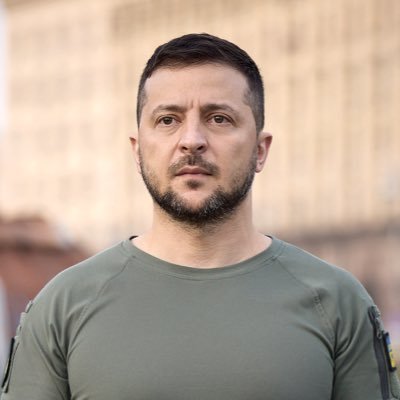
London. A meaningful and warm meeting with Prime Minister @Keir_Starmer.
During our talks, we discussed the challenges facing Ukraine and all of Europe, coordination with partners, concrete steps to strengthen Ukraine’s position, and ending the war with a just peace, along with robust security guarantees.
A principled statement of support from the Prime Minister and an important decision: today, in our presence, Ukraine and the United Kingdom signed a Loan Agreement. This loan will enhance Ukraine’s defense capabilities and will be repaid using revenues from frozen Russian assets. The funds will be directed toward weapons production in Ukraine. This is true justice – the one who started the war must be the one to pay.
I thank the people and government of the United Kingdom for their tremendous support from the very beginning of this war. We are happy to have such strategic partners and to share the same vision of what a secure future should look like for all.
🇺🇦🇬🇧
James Matchett 🔜 bsky retweeted
City Hall will be illuminated in blue & yellow this evening to show solidarity & support for Ukraine on the three-year anniversary of the Russian invasion.
#BelfastLightsAtNight

ALT City Hall illuminated in blue and yellow.
James Matchett 🔜 bsky retweeted

Last Chance for Early 🐤 Tickets – Offer Ends This Friday 🎟️❗
Book online 👉 beltech.co/
#BelTech25

James Matchett 🔜 bsky retweeted
defending freedom and not going anywhere.
thank you to everyone who is standing with us.

James Matchett 🔜 bsky retweeted
It was a pleasure serving on the @CISAgov Technical Advisory Council, which has now officially been shut down 🫡

DHS has terminated the memberships of everyone on its advisory committees.
Includes several cyber committees, like CISA's advisory panel & the Cyber Safety Review Board, which was investigating Salt Typhoon.
That review is "dead," person familiar says.
documentcloud.org/documents/…

James Matchett 🔜 bsky retweeted

wow. Upon Court order, incriminating exhibits were unsealed at 3:30am in an AI lawsuit against Meta. Once past a 'fake privilege,' it appears Zuckerberg approved the use of a highly controversial, pirated dataset.
Note OpenAI, too? AI companies with no ethics or guardrails. /1

James Matchett 🔜 bsky retweeted

Look I want accommodation in the city centre as much as the next person but why right in this spot? One of the most iconic views in Belfast now ruined. Soooo many vacant upper floors in the centre of town that could have been utilised, ugh #Belfast – at Belfast, Northern Ireland

James Matchett 🔜 bsky retweeted

"All good wishes for Health, Happiness and Good Luck in coming New Year. May peace be with us."
------
Postmark: 30 November 1914

James Matchett 🔜 bsky retweeted
Due to U.S. telco networks being compromised, today CISA is recommending:
1. Use only end-to-end encrypted communications
2. Enable Fast Identity Online (FIDO) phishing-resistant authentication
3. Migrate away from Short Message Service (SMS)-based MFA
4. Use a password manager to store all passwords
5. Set a Telco PIN
6. Regularly update software
7. Opt for the latest hardware version from your cell phone manufacturer
8. Do not use a personal virtual private network (VPN)
James Matchett 🔜 bsky retweeted

🚨 Breaking: White House official Anne Neuberger reveals Salt Typhoon hacking campaign has compromised at least 8 US telecom providers - far more extensive than initially reported.
Campaign impacts dozens of nations.


