

The internet holds vast secrets for those who know how to look
Joined June 2025
- Tweets1.4K
- Following59
- Followers6.2K
- Likes15.3K




Pinned Tweet
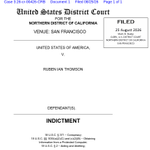
How Threat Actors Abuse Legal Processes 🔥
A deep dive look at fraudulent subpoenas, warrants, EDR and the shinyhunters domain seizure
intelops.st/how-threat-actor…

Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site
krebsonsecurity.com/2026/10/…
IntelOps retweeted

Find out more about OSINT Industries training 👇
osint.industries/services/tr…

IntelOps retweeted

🚨 BREAKING: A Broadcom Wi-Fi bug lets anyone in range run code on routers without the password.
Quentin Kaiser showed it on Proximus, Orange Belgium and VOO routers and estimates ~1.5M in Belgium are exposed, none patched.
The bug dates to 2010. Broadcom won't assign a CVE.


IntelOps retweeted

🚨 UNC6671 INFRASTRUCTURE UPDATE
Two more hostnames have appeared under myssologin[.]com:
⚖️ kelleydrye.myssologin[.]com
⚖️ willkie.myssologin[.]com
The apparent references are Kelley Drye and Willkie, expanding the cluster to four major law firms.
Tracking live. 👀

IntelOps retweeted

Last year, @amnesty revealed technical evidence of spyware firms like Intellexa developing tools for zero-click infection through online ads.
We warned of a dangerous new threat to civil society. Now @citizenlab has caught devices at Al Jazeera being hacked via malicious ads. 🧵


Q27 Why was rey claimed as a larp of SLSH when yuro [ already been fedded ] and rey created it together?
What happened when rey fellout with the other threat actors in SLSH?
A27 I think he was just claimed as a larp of ShinyHunters.
Not sure what happened in the fallout.
Q29 Shifting a bit off topic:
Umbreon, this Canadian exec, and in-between Rey.
Has anyone actually important or vital (to SH) been nabbed to your knowledge?
Both SH leak sites are down (shnyhntww & espeon), and according to Krebs SH has said in response to emails that they are trying to de-escalate, why?
The FBI hack was (supposedly) for rep - what SH is doing now has destroyed that rep.
3 ‘members’ arrested, website down, seemingly no word from the leadership.
I’d like to hear your thoughts, you seem plugged in.
A29 When we're speaking of SH, it's important to acknowledge that the SH we discuss is largely SLSH.
Rey was SLSH in a sense and therefore was SH in a sense. I believe that he was likely one of if not the only orchestrater(s) in the FBIJobs hack.
If the rest of what SH is trying to deescalate, I wouldn't be surprised. Describing him as suicidal is a very apt description for this reason. The FBI hack was this complex of his at the greatest. I don't think he sees it as "destroyed reputation."
There's some glory in suicide. Perhaps he was Japanese! :-)
Perhaps this is my memorial to him.
Or, rather, a memorial to the Rey I considered a friend (and still do, he's just—as they say—no longer with us.)
IntelOps retweeted

“ShinyHunters” pulling ALPHV BlackCat ghosts posting a fake seizure banner.
Bro I made the one you’re using 🤡🤡🤡

IntelOps retweeted
🚨 CURRENT SHINYHUNTERS INFRASTRUCTURE
🇺🇸 DataWagon LLC — 3 IPs
🇷🇺 PROSPERO OOO — 2 IPs
Five IPs across two providers. Tracking continues. 👀
#ShinyHunters #ThreatIntel

Trezor allegedly hit with implants

Despite claims by Trezor today that none of its crypto devices have been compromised - unlike the devices of Ledger, its competitor - hardware hacker @joegrand says he found implants in two Trezor devices and reported this to Trezor in August. My story: zetter-zeroday.com/trezor-wa…

IntelOps retweeted
Ledger was warned last March about implants by hardware hacker @joegrand but apparently did little because no one had yet used implants to steal crypto. That changed last wk with the heist of hundreds of accounts. There is evidence stolen seeds were sent to servers in Hong Kong
Someone embedded hardware implants in Ledger crypto wallets to steal the randomly-generated seed phrases that protect crypto accounts. They used the stolen seeds last week to hijack $100 million in crypto from 300+ crypto accounts. I dug into the mystery zetter-zeroday.com/who-is-pl…

IntelOps retweeted

Akatsuki Legion exposed a pipeline targeting #Citrix #NetScaler via CVE-2026-88771/72. By intercepting a console at 66.154.127[.]156, researchers found a 7-stage machine dropping a DDoS botnet. Respect to @Huntio for backing up the data and @Huntbackio for rich telemetry.
🔗👇
