

cyber threat intelligence, OSINT, and corgi hair. Thoughts are my own, RT/Like != Endorsement. (He/Him)
Chicago, IL
Joined June 2018
- Tweets2.7K
- Following1.1K
- Followers741
- Likes11.9K



Lol this is like the threat actor equivalent of spamming slop bug bounty reports on HackerOne.


Posting and hyping up unverified threat actor claims when I need some attention #OSINTSlop
So, what is your company planning on doing once VC stops subsidizing tokens? Committee sign offs for each prompt ?
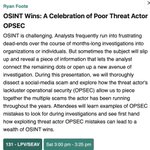
My first ever in-person cybersecurity conference was @BsidesORL back in 2019. So I am really pumped to be giving my talk "OSINT Wins: A Celebration of Poor Threat Actor OPSEC" at the conference tomorrow!


There are many indicators that this type of OSINT engagement bait is slop, but one of the most egregious is recommending a tool that hasn’t worked in years

IntelCorgi retweeted

The end of that Michigan game felt like a metaphor for our society right now. The elite the get rules bent or ignored to accommodate their wants, without any consequence whatsoever

IntelCorgi retweeted

Next hacker summer camp giveaway!
3 seats to our “The Bug Hunters Methodology” course!
Like and share to be entered!
arcanum-sec.com/training/the…

Thanks, HackerOne! I’m so excited to have to give my id to a third party (Veriff) in order to submit bugs to bug bounty programs docs.hackerone.com/en/articl… 🤔

IntelCorgi retweeted

time to bring back "PCAP or it didn't happen" until we start seeing evidence of these claims. I'm not saying its not possible, I'm saying "show your work".


One of the things they don’t tell you bout your thirties is how many times you will find yourself wishing you had a shop vac


Idk if I was a foreign intel operator trawling LinkedIn and I saw someone’s dad made a sponsored post advertising his sons name, job in the military, and clearance level I might splurge a bit on lunch that day #opsecawareness


I used to recommend the @hunchly mobile app for preserving mobile screenshots, but it looks like they took the app off the app store, probably after @MaltegoHQ bought them. Does anyone have any recommendations for an app with similar functionality?


