

Software & Security Research, Penetration Testing, Ethical Hacker Education
Concord, NC
Joined January 2013
- Tweets295
- Following4.1K
- Followers4.6K
- Likes2.7K


Hyperion Gray retweeted

Happy Monday to all researchers. We hope you have a very successful week of hunting and programming. Should you want to sell any technologies don't hesitate to contact us.
Hyperion Gray retweeted

Expectation: I'll use GraphViz to plot this callgraph and it will make the structure perfectly clear
Reality:

Hyperion Gray retweeted
We are firm believers that researchers should get the money they deserve for the research they conduct. It takes time and effort. Zero Security prides itself on helping people from all over the world. We are currently accepting new clients to represent as we continue to expand
Hyperion Gray retweeted

Chainlink is a Russian pump-and-dump fraud.
Until when are such fraudulent activities going to happen under @SEC_Enforcement @SEC_News watch? Protect the American people from Russian fraudsters!
@coinbase why are you tolerating this scam on your platform? @brian_armstrong
$LINK

Hyperion Gray retweeted

The Spectre Rootkit is now released alongside my @BlackHatEvents USA talk, Demystifying Modern Windows Rootkits. Go check it out! github.com/d4stiny/spectre

Hyperion Gray retweeted

Cerberus Bot v2 source can leak to the criminal forum xss[.]is, source code already available for the admin of the forum. The seller looked for a guy who can manage the project but doesn't found. Cerberus Bot selling has been closed because no way to manage a project.


Hyperion Gray retweeted

I've been taking a huge interest in APTs recently and Threat Intelligence in general and I found this paper called "A Threat Actor Encyclopedia" by @ThaiCERT and it's fire! 🔥
thaicert.or.th/downloads/fil…
Hyperion Gray retweeted

If you need to debug a Linux kernel Hyper-V guest check out github.com/weltling/convey.
Allows you to kernel debug the guest from WSL on the host which is neat.

Hyperion Gray retweeted

OPSEC Fail!
Iranian #APT35 hackers accidentally exposed 40 GB worth of sensitive data online, containing #hacking training videos that revealed they managed to hack a member of the U.S. Navy, and a Greek naval officer.
Read Details — thehackernews.com/2020/07/ir…
#cybersecurity

Hyperion Gray retweeted

My new research and open source memory scanner tool Moneta dives deep into the topic of memory stealth and forensics when designing malware or fine tuning detection for it. Many should find this information valuable forrest-orr.net/post/masking…

Hyperion Gray retweeted

OK, we talked to another hacker. Were able to confirm how they got accounts: Twitter employee used internal tool to change email addresses associated with accounts. Twitter seems to have just confirmed this in tweets as well
vice.com/en_us/article/jgxd3…
Hyperion Gray retweeted

At last, the series begins: MMS Exploit Part 1: Introduction to the Samsung Qmage Codec and Remote Attack Surface. googleprojectzero.blogspot.c…
I'm excited to start sharing more about this work, starting with a deep dive into the internals and history of the codec.



Hyperion Gray retweeted

From @FireEye : Financially Motivated Actors Are Expanding Access Into OT
~Attackers are getting more and more comfortable in our industrial spaces.
fireeye.com/blog/threat-rese…
Hyperion Gray retweeted

This is my first part of a series about hooking minifilter/miniport. In this research I focus on Fs Minifilter hooking:
link.medium.com/m93AktZk27
Hyperion Gray retweeted
People usually don't pay attention to thread synchronization techniques (user mode or with kernel objects), but it could be interesting to analyze details, mainly when malware uses these techniques to synchronize malicious threads or two stages of unpacking.
#malware #reversing

Hyperion Gray retweeted

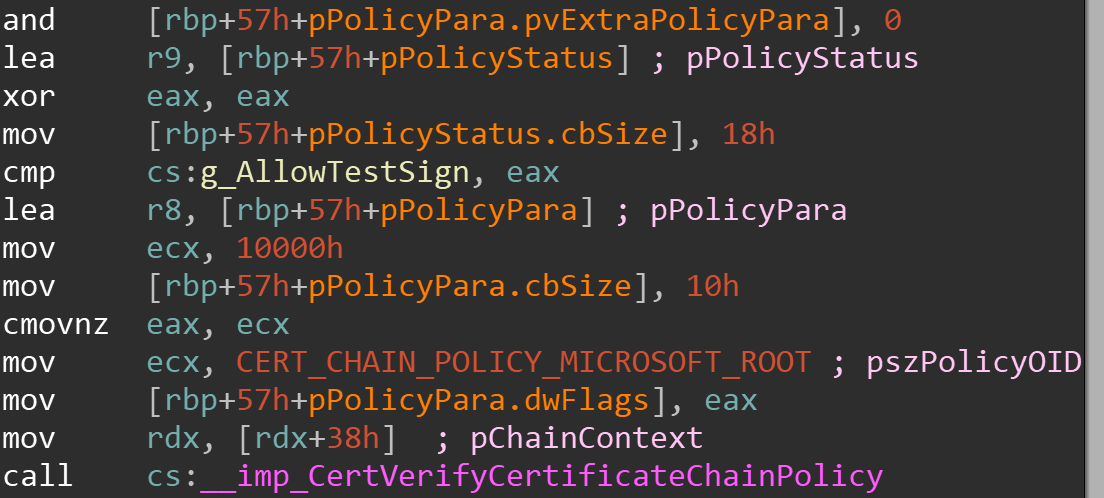
Adding ARMv8.5 Memory Tagging Extension #MTE Opcodes to IDA for #iPhone12 support github.com/Antid0teCom/aarch…
(Please test and report all bugs. This is a quick hack and only partially tested and likely full of bugs)


Hyperion Gray retweeted

I have recompiled netcat for Win to be compatible with Donut. The precompiled version doesn't have the reloc section.
It could be useful if you want to load it directly in memory converting it in shellcode :D
antoniococo.github.io/tools/…
Hyperion Gray retweeted

Published a new blog post detailing the inner workings of hardware breakpoints and exception handling on Windows. Let me know what you think. ling.re/hardware-breakpoints…