
SoB'25 @fedimint || Software Developer || Blockchain Developer || Open Source Contributor #freedom #bitcoiner
World
Joined December 2023
- Tweets490
- Following376
- Followers303
- Likes416




Pinned Tweet
Do you have a GitHub profile?
I'd love to connect with more developers!
Drop your GitHub profile link. Will connect there
Mine - github.com/Harshdev098

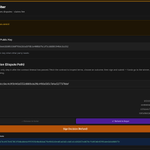
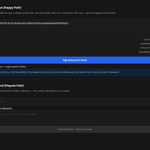
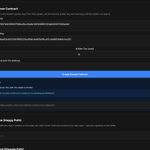
The @fedimint Escrow Module has evolved since I shared the design.
The design has changed quite a bit through implementation, and discussions with people building around Bitcoin, specially @getchama_app @Colabonate @PlebeianMarket and #nostr devs
Here's what's changed 🧵

I've been working on potential escrow module for @fedimint that enables:
👉 Buyer/Seller escrow contracts
👉 Federation enforces contract rules and signature verification
👉 Arbiter assisted dispute resolution
👉 Trust-minimized fund custody through federations
how it works: ...


Discussions with @getraud @Colabonate and other #nostr devs have helped me validate assumptions, identify issues in the threat model, and think through how the escrow flow could map onto their systems.
Want the full walkthrough?
I have updated the playground along with this design:
harshdev098.github.io/escrow…
If you’re working on marketplaces, payments, or other Bitcoin applications where escrow could be useful, I’d love to hear your thoughts.
Design doc: gist.github.com/Harshdev098/…
Harsh Dev Pathak retweeted

built ecashmesh for the @bitshala_org BOSS hackathon.
connecting @fedimint federations & @CashuBTC mints through @lightning
It also checks whether a source can actually afford the route before recommending it.
Ecash that isn't stuck on an island.

ecashmesh⚡️
evidence-aware routing for Ecash across @CashuBTC , @fedimint and eventually @lightning
beyond fees: liquidity, reliability, proof freshness and route risk
which Ecash route should I use, and why?
building for @bitshala boss battle 2026
🔗 github.com/bansalayush247/ec…

Harsh Dev Pathak retweeted

Shielded Bitcoin:
You peg BTC into a private bucket of encrypted notes. Move it around with zero-knowledge proofs so nobody sees sender, receiver, or amount. Later you peg out to a fresh address, on-chain link is gone.
Same mixer logic as Tornado Cash:)
No soft fork. No operators. Bitcoin just stores the receipts.


Harsh Dev Pathak retweeted

Nostr VPN is a decentralized Tailscale alternative that needs no email addresses, user accounts or control servers. Now it also lets you buy and sell VPN bandwidth for bitcoin. nostrvpn.org


Harsh Dev Pathak retweeted

Without privacy, you are simply holding your would-be attackers’ Bitcoin or crypto for them. They just haven’t gotten around to taking it from you yet.

Since 2022 @ODFoundation has campaigned before EU regulators for the privacy of payments and asked the bitcoin industry to join. We were grateful for the support of @jack , @obi and a few other bitcoiners. Most others laughed and said it was not their business.
In 2023 we won a majority in the European Parliament for our safeguards. The closed-door trilogue then removed majority of them from the AML Regulation. We did not have enough loud voices from the industry to defend payment privacy, and now we face the hunting of our data at scale.
There is still a chance. OSCE PA parliamentarians have adopted remedies against the weaponisation of AML/CFT laws and recognised transnational financial repression as a threat to the security of the OSCE area, which covers the US, Canada, Europe and Central Asia.
This would have been impossible without the support of @AtlasNetwork, @cypher_tank and the Reynolds Foundation @AlvaroSalas , who understood the problem at first sight.
Will you keep observing and complaining, or join and make this space safe to use, invest and build in? There is nowhere else to run.
Privacy has to be protected and normalised as a human right. Now, before it is too late.
Harsh Dev Pathak retweeted
i’m afraid of KYC and you should be too.
KYC is a risk to your personal safety.
collecting personal information in the age of cyber security breaches everywhere is extremely irresponsible. and it’s not going to get any better any time soon.
our laws shouldn’t require institutions to KYC, they should prevent them from doing so.
institutions that leak KYC information or fail to defend it from hackers should be punished by the law for risking their user’s safety.
Harsh Dev Pathak retweeted

We found a bug in our legacy Lightning integration and are contacting public gateway operators.
User funds, federations, and ecash are not affected.
Gateways using LDK Node or our newer LNv2 protocol are also not affected. We still recommend staying up to date.
🧵
Harsh Dev Pathak retweeted
A topic this critical deserves my first long-form post.
The real question is not trusted vs trustless. It's how many independent things have to go wrong before you lose money.
@TheBlueMatt said it in one sentence. Run the same software, suffer the same bugs.
⬇️
Think about what actually happened. Liquid was an 11-of-15 multisig. Fifteen independent signers. No keys were compromised. Nevertheless, eleven honest signers approved a withdrawal that emptied 95% of the reserves, because every one of them was running the same code, and the code had the same bug.
A few weeks before that, one firmware flaw swept thousands of Coldcard cold wallets. Different product, same lesson from the other side.
Before anything else, none of this is abstract. Coldcard victims lost savings they stacked over years. LBTC holders woke up to frozen funds through no fault of their own. And anyone who has ever shipped code that holds other people's money can and should empathise with the engineers at Blockstream. I do.
But we have to be honest with ourselves here. The world has changed. AI tooling is surfacing bugs that sat dormant for years, a point Matt also made after Coldcard. Five year old vulnerabilities are getting weaponised. Supply chains are getting attacked. "Secure so far" doesn't mean much anymore.
So let's also retire a comforting fiction. There is no such thing as “trustless.” There never was. It was always shorthand for trust-minimised. Every system puts trust somewhere: in code, in firmware, in the people who write, ship, and run both. Liquid users trusted Elements. Coldcard users trusted a random number generator they never saw.
Don't get me wrong. We should keep doing everything possible to make our code, our systems and the people behind them as trustworthy as we can. Audits, reviews, security culture, all of it. But trustworthiness is not the same thing as fault tolerance, and we need both. Fault tolerance only comes from having independent failure domains. In other words, no single point of failure.
So what does this look like in practice:
1. Multiple implementations of every protocol that holds funds, with the power to reject and not just observe.
2. Multiple wallet implementations. We mostly have this already.
3. Keys generated on hardware from different vendors.
4. Multiple independent, trustworthy humans behind every system that holds money.
5. Geographic and jurisdictional distribution as one jurisdiction's rules can change overnight.
And to be clear, Matt's sentence currently applies to @Fedimint too. Fedimint was designed to remove single humans and single institutions as points of failure. That's the whole point of a constellation of federations. But today there is only one implementation of the protocol: every guardian runs the same software. Federated humans, monoculture code, and it's not good enough.
So I'm calling on the Fedimint community to lead by example and fix this as quickly as we can.
And to everyone else, tell me where I'm wrong. If I am, propose something better. If I'm not, then let's stop debating trusted vs trustless and start demanding independence at every layer. Software, hardware, humans, jurisdictions. All the way down.
That's how Bitcoin stays worth the highest confidence as we enter this new age.

Harsh Dev Pathak retweeted

Calling on fellow cypherpunks to build alternative Fedimint implementations.
The Liquid hack shows once again that single points of failure are what will break our systems and that includes the code we write.
Security is an asymmetric game: an attacker has to find one weakness, while defenders have to find all. AI has permanently changed the attacker-defender balance for the worse. This is a fundamental problem for the entire freedom tech space and only mitigatable by aggressively reducing single points of failure. Federations are meant to do exactly that, but just like Liquid, Fedimint shares the “single implementation” problem.
If we still want to bring privacy and freedom to the world we need to work together more than ever to reduce these single points of failure. For me that means seeking help to bootstrap independent Fedimint implementations. We are still early, but I've started extracting a specification that others could build off and would love to collaborate with any fellow cypherpunks who want to join us in that mission. In particular, I’d love to work with @callebtc and the @CashuBTC team, who have much more experience with a multi-implementation ecash protocol while the Fedimint team brings federation experience to the table.
While AI exposes existing vulnerabilities and wreaks havoc in our ecosystem, it is also an opportunity for talented engineers to be far more productive than ever before. I’ve been talking with @fedibtc and there is funding for a small, crack team to pull this off. If this sounds interesting as a funder, please reach out! The idea is for the teams to be purposefully disconnected from the existing Fedimint implementation and to work autonomously, communicating mainly through the spec process.
If you too believe that privacy and freedom are needed more than ever, please join us!

A topic this critical deserves my first long-form post.
The real question is not trusted vs trustless. It's how many independent things have to go wrong before you lose money.
@TheBlueMatt said it in one sentence. Run the same software, suffer the same bugs.
⬇️
Think about what actually happened. Liquid was an 11-of-15 multisig. Fifteen independent signers. No keys were compromised. Nevertheless, eleven honest signers approved a withdrawal that emptied 95% of the reserves, because every one of them was running the same code, and the code had the same bug.
A few weeks before that, one firmware flaw swept thousands of Coldcard cold wallets. Different product, same lesson from the other side.
Before anything else, none of this is abstract. Coldcard victims lost savings they stacked over years. LBTC holders woke up to frozen funds through no fault of their own. And anyone who has ever shipped code that holds other people's money can and should empathise with the engineers at Blockstream. I do.
But we have to be honest with ourselves here. The world has changed. AI tooling is surfacing bugs that sat dormant for years, a point Matt also made after Coldcard. Five year old vulnerabilities are getting weaponised. Supply chains are getting attacked. "Secure so far" doesn't mean much anymore.
So let's also retire a comforting fiction. There is no such thing as “trustless.” There never was. It was always shorthand for trust-minimised. Every system puts trust somewhere: in code, in firmware, in the people who write, ship, and run both. Liquid users trusted Elements. Coldcard users trusted a random number generator they never saw.
Don't get me wrong. We should keep doing everything possible to make our code, our systems and the people behind them as trustworthy as we can. Audits, reviews, security culture, all of it. But trustworthiness is not the same thing as fault tolerance, and we need both. Fault tolerance only comes from having independent failure domains. In other words, no single point of failure.
So what does this look like in practice:
1. Multiple implementations of every protocol that holds funds, with the power to reject and not just observe.
2. Multiple wallet implementations. We mostly have this already.
3. Keys generated on hardware from different vendors.
4. Multiple independent, trustworthy humans behind every system that holds money.
5. Geographic and jurisdictional distribution as one jurisdiction's rules can change overnight.
And to be clear, Matt's sentence currently applies to @Fedimint too. Fedimint was designed to remove single humans and single institutions as points of failure. That's the whole point of a constellation of federations. But today there is only one implementation of the protocol: every guardian runs the same software. Federated humans, monoculture code, and it's not good enough.
So I'm calling on the Fedimint community to lead by example and fix this as quickly as we can.
And to everyone else, tell me where I'm wrong. If I am, propose something better. If I'm not, then let's stop debating trusted vs trustless and start demanding independence at every layer. Software, hardware, humans, jurisdictions. All the way down.
That's how Bitcoin stays worth the highest confidence as we enter this new age.
Harsh Dev Pathak retweeted
Fedimint v0.12.0 "Second Nature" is here! 🚀
The highlights:
* v2 modules (lnv2, mintv2, walletv2) now the default for new federations ✨
* Much lower Lightning payment latency ⚡️
* @iroh_n0 1.0 networking 🌐
* Wallet recovery without downtime 🔄
github.com/fedimint/fedimint…

Harsh Dev Pathak retweeted
AI weekend project: analyze privacy of real-world ecash usage and optimize coin selection

Harsh Dev Pathak retweeted

Ecash App v0.10.0 is now available on Google Play, Zapstore, and ecash.love.
Mostly contains security fixes discovered through AI scanning, but there's a couple cool new features, such as a Guardian Dashboard.


What actually happens inside @fedimint escrow?
I put together an interactive playground where you can watch the protocol flow
No docs. No live federation. Just the protocol flow, visualized ⚡
A TypeScript mirror of escrow module
Link: harshdev098.github.io/escrow…
#bitcoin #nostr
