

Data Discovery Starts Here
Global
Joined March 2009
- Tweets4.2K
- Following414
- Followers575
- Likes634




The @PCISSC Security Considerations for AI Systems makes clear that PCI DSS applies to AI tools in much the same way as any other system. Our breakdown of the key takeaways: hubs.ly/Q04B91yJ0

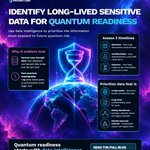
Europe's central law enforcement agency, @europol has published two new reports examining how quantum computing could expose digital assets and encrypted information, and outlining steps to prepare. Read more: hubs.ly/Q04zqbP30

The countdown to @PCISSC’s #PCIEURCM26 is on. Join us in Edinburgh, Scotland for valuable #paymentsecurity insights, collaboration and industry discussions. hubs.ly/Q04zq8X30

AI is expanding data footprints. Risk assessments can become outdated. And sensitive data doesn't always stay where it's expected. How can organisations manage risks they can't accurately assess?
It starts with data intelligence. 🔍 Read more at: hubs.ly/Q04zV_0v0


Find out why data is transforming the digital landscape of organizations today, and how data discovery forms a crucial component of successful transformation – driving innovation, reducing risk and building for the future. Read more: hubs.ly/Q04zq5y30

We're excited to be joining our partners @VectraCorp at #HIMAA26 in Sydney, 26–28 October 2026. Stop by and find out how we're helping organizations with next-generation risk mitigation through data intelligence for visibility, security and compliance. hubs.ly/Q04zMLjw0

The 2027 Global Digital Trust Insight report from @PwC is here. 42% claim that investing in data protection and data trust is a top priority for 2027 budget spend, but fewer than half have data discovery in place company-wide. Read more: hubs.ly/Q04zq1M-0

We break down the key takeaways from the latest AI guidelines announced at the PCI SSC North America Community Meeting and explain how data intelligence delivers key evidence for compliant use of AI.
Read the full article here: hubs.ly/Q04yk9xp0
Data intelligence is an evidence-based understanding of the sensitive data an organization holds. Learn what data intelligence means for next-generation risk mitigation in our latest article, available now: hubs.ly/Q04yjnS10

The EDPB has published draft guidelines setting out a five-step methodology for supervisory authorities deciding whether to impose a fine under GDPR. Controls evidence is key to organizational protection: hubs.ly/Q04yjnm20

September brought new privacy and security obligations into force across Europe, North America and Asia. Applicability thresholds are falling, penalties are rising and regulators are holding firm on enforcement dates. Find out more: hubs.ly/Q04yjmY30

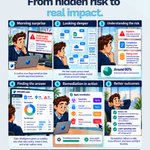
Finding sensitive data is only half the job. The real value comes from what you do next. Data remediation turns visibility into action — helping reduce risk and strengthen control.
👉 Read more: hubs.ly/Q04ykM4g0
#DataSecurity #DataRemediation

The cyber threat landscape of Europe is heavily influenced by ideology-based campaigns and attacks motivated by financial gain, according to ENISA's Threat Landscape Report 2026. Read the full report: hubs.ly/Q04yjmQw0
Data remediation boils down to four options: quarantine the data for review, encrypt it in place, mask it, or delete it. Each addresses a different situation. Read the full article to learn more: hubs.ly/Q04y36360

We’re proud exhibitors at @PCISSC's #PCIEURCM26! Stop by our booth in Edinburgh, Scotland and connect with our team at the Vendor Showcase. hubs.ly/Q04y35Z40

September brought new privacy and security obligations into force across Europe, North America and Asia. Applicability thresholds are falling, penalties are rising and regulators are holding firm on enforcement dates. Find out more: hubs.ly/Q04y7_6-0
Non-human identities (NHIs) now account for 31% of intrusions, according to @spycloudco latest report. Securing them first means finding them, using data intelligence solutions like Enterprise Recon.
Find out more: hubs.ly/Q04xGc3W0 (Report: hubs.ly/Q04xGc2t0)

Verizon's 2026 DBIR analyzed more than 22,000 confirmed breaches in a single 12-month period. While attack paths can't all be controlled, the volume of sensitive data left exposed can be. Read more: hubs.ly/Q04xGbQz0

The @PCISSC new AI guidance contains one line that should change how teams think about AI in payment environments – Protect the sensitive data shared with AI systems. What cardholder data sits inside the systems you have just connected an AI agent to? hubs.ly/Q04xGbrK0

We're barely unpacked, but we can't wait to join the @PCISSC at the Europe Community Meeting in Edinburgh next month. Visit us in the Vendor Showcase to find out how our latest generation of solutions support PCI DSS for next-generation risk mitigation. hubs.ly/Q04xJRzV0
