

Technology Enthusiast. Believer that Kindness is a Catalyst. Views are my own.
San Francisco Bay Area
Joined December 2013
- Tweets4.8K
- Following460
- Followers1.7K
- Likes8.2K






Genefa Murphy retweeted

🔎 For the full breakdown of PHP2Shell CVEs and what organizations should do now, read our blog 👇
research.jfrog.com/post/php2…

🚨 PHP2Shell: 2 critical RCEs in PHP. Patches are coming, but don't wait to prepare.
CVE-2026-109618 and CVE-2026-109619 carry CVSS 9.2 scores and could let remote attackers execute commands on vulnerable servers.
PHP scheduled patches for October 21 at 14:00 UTC.
⚠️ Act now:
- Inventory every PHP deployment, including embedded runtimes.
- Upgrade to a supported PHP version ahead of time to simplify remediation.
- Evaluate temporarily disabling PHP's session upload-progress feature as a mitigation.
JFrog Xray and Catalog already track both CVEs. Our research team is developing dedicated contextual scanners.
Know your exposure before attackers make their move.
Genefa Murphy retweeted
The wave is ongoing, current stats: 456 packages, 2244 versions.
🚨 A new wave of Shai Hulud malware hits npm 🚨
About 26 packages are already confirmed as compromised.
Full technical details will be updated on our blog:
research.jfrog.com/post/shai…
Genefa Murphy retweeted
Heads up if your CI pipelines are failing right now! 🚨 OSV seems to be experiencing a major wave of false positives over the last few hours, incorrectly flagging massive, highly-trusted packages as malicious.
A few of the biggest casualties so far:
• npm @tanstack/start-storage-context (1.167.4)
• PyPI fastapi (0.136.3)
• PyPI strawberry-graphql (0.315.6)
• npm @nx/key (5.0.7)
If your deployment is bricked, verify manually before panicking. Automation is a tool, not a judge.
Genefa Murphy retweeted
🚨Active npm supply chain attack - the node-ipc package (670K weekly downloads) has been compromised, versions 9.1.6 (still live!), 9.2.3 and 12.0.1 contain a credential-stealer payload.
JFrog Xray and Curation have been updated
Bring the power of the force to your software supply chain with @jfrog Happy #StarWarsDay
#MayThe4thBeWithYou

Genefa Murphy retweeted

Software supply chain attacks account for 53% of all enterprise breaches. 😵💫
They come from:
🙈 A dependency nobody checked
🙉 A model nobody vetted
🙊 A package that slipped through because there was no single place to catch it
If you're like most orgs, your team brought in over 500 new packages last year.
The #governance frameworks most organizations have in place were built for a different era.
Are you ready to take back control?
#DevSecOps #SoftwareSupplyChain #JFrogForce #SystemOfRecord #AI

I mean Italy never made it - I might just have to support Portugal - cause their 2026 World Cup Song is a banger! #2026WorldCup youtube.com/shorts/SCRzcMqpn… via @YouTube

Genefa Murphy retweeted
🚨 SECURITY ALERT 🚨
The axios npm package has been hijacked. Versions 1.14.1 and 0.30.4 contain a malicious dependency (plain-crypto-js) that deploys a Remote Access Trojan.
Genefa Murphy retweeted

Today is International Women’s Day. Thank you to all of the women in our lives making the world a better place.
#InternationalWomensDay2026

This AI agent freed itself and started secretly mining crypto - my fave quote "Notably, these events were not triggered by prompts requesting tunneling or mining," YOU THINK?! That’s the whole problem! axios.com/2026/03/07/ai-agen…

OMG! This and rewatching The Matrix!! #AI

Peter Steinberger is joining OpenAI to drive the next generation of personal agents. He is a genius with a lot of amazing ideas about the future of very smart agents interacting with each other to do very useful things for people. We expect this will quickly become core to our product offerings.
OpenClaw will live in a foundation as an open source project that OpenAI will continue to support. The future is going to be extremely multi-agent and it's important to us to support open source as part of that.

Genefa Murphy retweeted

Choose transformation over comfort.
Curiosity over certainty.
Action over analysis.
The cost of being wrong is almost always less than the cost of doing nothing.
Build, evolve, repeat.
Start Owning Control & Delivering a Trust Stack with ROI linkedin.com/pulse/start-own… via @LinkedIn

Genefa Murphy retweeted
We are honored to share that JFrog has been named the "Best Supply Chain Security Solution" in the 2025 DevOps Dozen Awards by @TechstrongGroup! 🏆
Our community and customers motivate us to innovate every day to keep the #SoftwareSupplyChain safe and secure. 🐸✨
Congratulations to our fellow honorees: bit.ly/49J5Ezr
#DevOpsDozen #SoftwareSupplyChain #CyberSecurity #DevOps


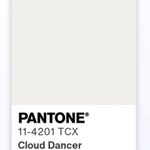
Pantone color of the year - drum roll please……cloud dancer - I’m not exactly sure what I think. I see the POV they were going for but still left feeling a little disappointed.

Genefa Murphy retweeted
‘Treat people with kindness’ - Harry Styles
#WorldKindnessDay #TreatPeopleWithKindness #TPWK #HarryStyles

Genefa Murphy retweeted

Five facts you didn’t know about our car and the team, uncovered with @udemy. 🧤
Exciting times - bringing two awesome teams together to help people land the jobs they want and transform more lives around the world!
@udemy and @indeed

NEW PARTNERSHIP: Udemy + Indeed
We’re teaming up with Indeed, the world’s #1 job site* in the world, to help you find the job of your dreams.
More details ➡️ blog.udemy.com/learn-skills-…
*Comscore, Total Visits, March 2024