

I Research Malware, Terrorism & Social Networks of Criminals for DarkTower and Intelligence For Good!
Birmingham, AL, USA
Joined May 2008
- Tweets9.8K
- Following2.2K
- Followers10.1K
- Likes2.5K


GarWarner retweeted

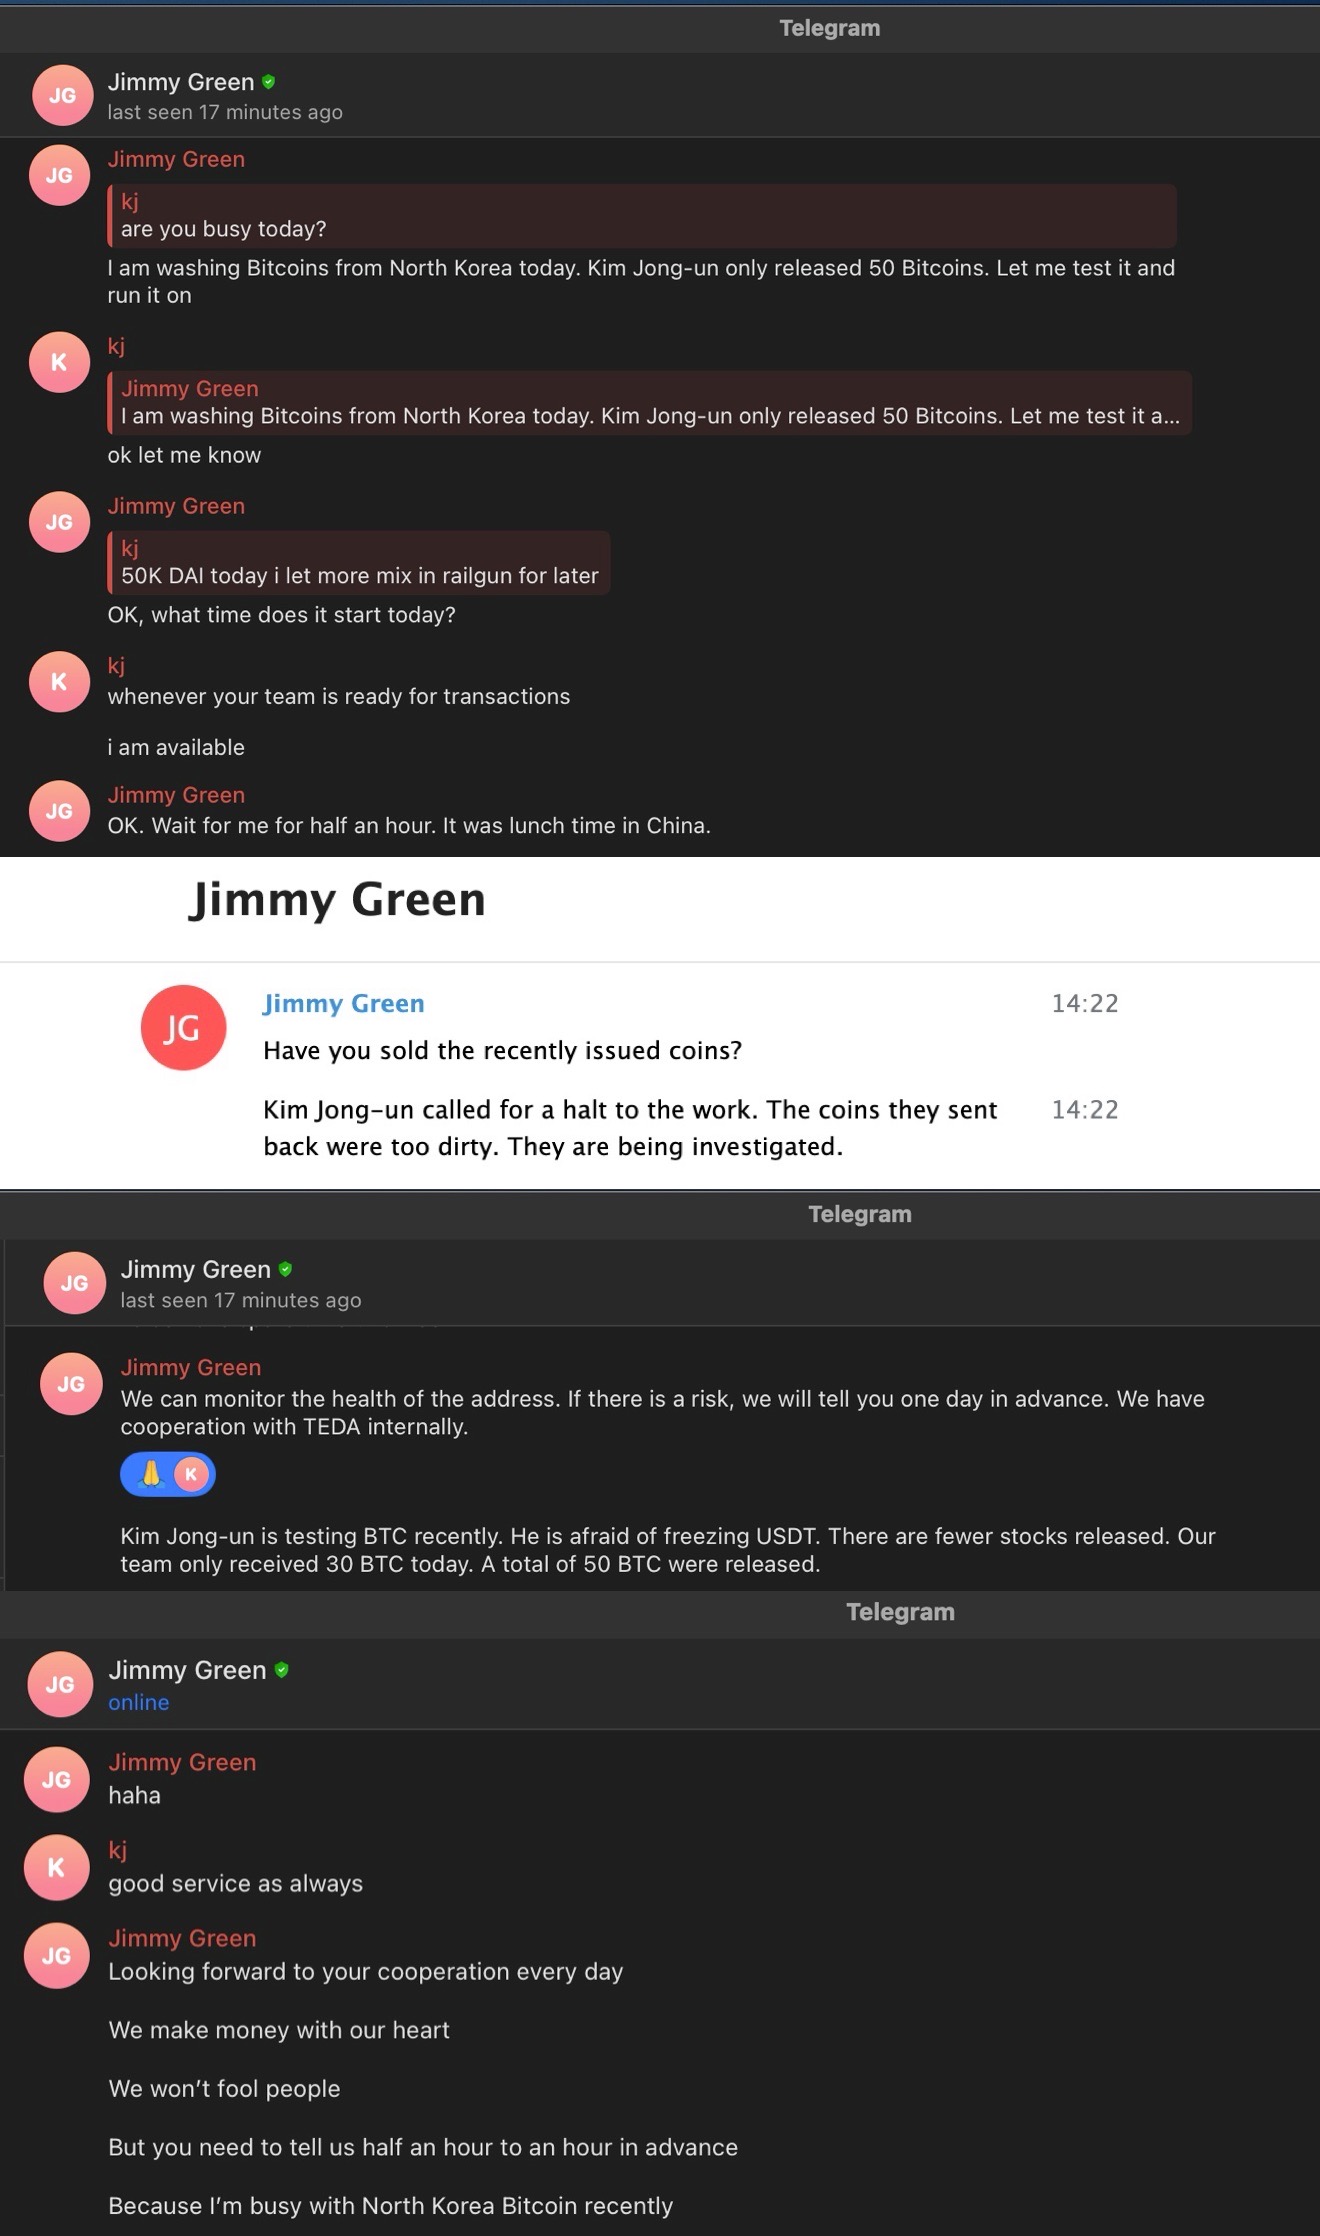
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

GarWarner retweeted

17 Iranians charged with conducting massive cyber theft campaign on behalf of the IRGC and other Iranian entities: the Mabna Institute hackers attacked systems belonging to hundreds of universities, companies, and other victims to steal research, academic and proprietary data, and intellectual property. @DOJNatSec @NewYorkFBI
justice.gov/usao-sdny/pr/17-…

GarWarner retweeted

🚨We are seeing increased targeting of PLCs in the Water and Wastewater Systems Sector. Owners, operators, & integrators should disconnect PLCs & internet-exposed OT assets ASAP to reduce risk of disruptions, configuration changes, & physical damage. 🔗 go.dhs.gov/5sC
GarWarner retweeted

【カンボジアニュース】プリンスグループ最高幹部をアメリカに強制送還、実質上の引き渡しか
朝日新聞によると、プリンスグループ最高幹部で、中国出身・キプロス国籍のフー・シー氏(44)が、出入国管理法違反の罪で略式起訴されたのち、29日にアメリカに送還されたことが関係者への取材でわかった模様です。
入管法では、退去強制による送還先は原則、国籍や市民権を持つ国とされますが、そうした国に送還できない場合は、本人の希望も聞いたうえで入管庁が決定することになっています。
米連邦捜査局(FBI) に引き渡されたと見られ、アメリカによる今後の捜査の進捗が注目されます。
写真: 7月5日にフー・シー容疑者が警視庁に入るところ(朝日新聞)


【カンボジアニュース】プリンスグループ最高幹部、罰金納付で警視庁から入管へ引き渡し
2026年7月24日、カンボジアを拠点とする複合企業プリンスグループの最高幹部の一人とみられ、東京・千代田区にある会社の代表も務める胡石(フー・シー)氏(44・中国出身・キプロス国籍)が、出入国管理及び難民認定法(入管難民法)違反の罪で東京東京地検により略式起訴されました。同日、東京簡易裁判所は罰金20万円の略式命令を出し、フー氏側はこれを即日納付しました。その後、警視庁により同氏は出入国在留管理庁に引き渡されています。
▪️日本への逃避と永住の画策
フー氏は遅くとも3年ほど前から日本への出入国を繰り返しており、2023年11月に企業経営者らに与えられる高度専門職の在留資格を取得して、2025年10月に再入国していました。しかし、今年4月以降、自己名義の在留カードを他人に提供したり、東京都中央区役所で別人に在留カードを不正に使わせて印鑑登録を申請させたりした疑いなどで、警視庁に逮捕され、今年7月5日にも再逮捕されていました。
捜査関係者やメディアの報道によると、これまでの調べに対し、フー氏は「自分や家族の身に危険が及ぶ」としてグループ内での具体的な立場を明かさなかった一方で、「いつどこで逮捕されるか、命を狙われるか分からず、安全に暮らせる場所がほしかった。そこで候補になったのが日本だった。日本が好きだ」と供述しています。海外当局の摘発などを逃れ、日本の永住権を取得するために印鑑登録や住民票を東京に移す手続きを進めるなど、日本での長期滞在を画策していたとみられています。今後は入管が退去強制事由に該当するか(国外退去強制となるか)を判断することになります。
▪️共犯者らの処分と今後の見通し
本事件では、フー氏以外にも中国籍の男女3人が逮捕されていました。東京地検は24日、郝鳳至容疑者(36)を同法違反罪で起訴し、李垠宏容疑者(31)を略式起訴しました。一方、陳暁光容疑者(49)については「起訴するだけの証拠の収集ができなかった」として嫌疑不十分で不起訴処分としました。
入管は、フー氏と同様に李容疑者と陳容疑者の2名も収容しており、退去強制の対象となるかを判断するとみられます。起訴された郝被告については、今後正式に裁判が開かれる予定です。
▪️「アジア最大級の犯罪集団」と欧米の制裁
プリンス・グループを巡っては、米国や英国政府などから「アジア最大の国際犯罪組織の一つ」として経済制裁を科されています。米財務省などによると、同グループは本社を置くカンボジアのプノンペンに巨大な専用拠点を設け、高額報酬をうたう偽求人で勧誘した各国の人々を監禁し、コールセンターを悪用して虚偽の投資話を持ちかけるなどの国際的なオンライン詐欺行為に従事させていたとされています。
米国当局は2025年10月に関係する個人・法人など146件を対象に制裁を科し、さらにフー氏が逮捕された後の2026年6月23日には関連する35件を追加制裁の対象に指定しています。世界的な包囲網が狭まるなか、日本国内での活動実態の解明が急がれています。


GarWarner retweeted

🚨 Fake IRS letters are targeting crypto holders with a QR code leading to a convincing fake "Digital Asset Compliance Portal."
It's not real. The IRS has no such program.
❌ Don't scan the QR code
❌ Don't enter any info
❌ Don't call any numbers listed
Stay safe → coinbase.com/blog/consumer-p…

GarWarner retweeted

The government’s crackdown since January appeared to have disrupted much of the visible scam compound infrastructure in Cambodia, but there was still a lack of accountability for compound owners and other key, elite-level interlocutors.
“The scam compounds are only the visible front end of the much more insidious architecture of elite impunity which gave rise to the industry in the first place,” Jacob Sims said. mekongindependent.com/2026/0…

GarWarner retweeted

Four Days to Make Each Victim Fall in Love, Powered by ChatGPT and Starlink
A trafficked worker in a Myanmar scam compound told AP he had four days to make each target fall in love. He impersonated a 28-year-old Singaporean woman, ran more than 100 chats at once while supervisors walked the desks with electric batons, and put his reach at 50,000 people from 17 countries in a single month. The tool that let him work across dozens of languages was a platform called KT, built on ChatGPT and Gemini for auto-replies, roleplay characters and translation in over 100 languages.
A new AP and FRONTLINE investigation traces American infrastructure all along the chain. One in five device connections at four sanctioned compounds ran through US-registered companies, among them Cogent, Oracle, AT&T and DigitalOcean. Starlink is the top provider in Myanmar with close to a 20% share. It has shown it can cut compounds off when it wants to, dropping 2,500 units last October and losing more than half its share, before use surged back by December.
The crackdown doesn't stick. When the military demolished KK Park and broadcast footage of dozens of seized Starlink terminals, at least seven of those same devices were online at a compound 30km away by January, according to International Justice Mission. IJM counts at least 25 sites built or grown since last fall's sweep. Washington has been asking the tech companies to cooperate, on a voluntary basis.
apnews.com/article/scams-fra…


GarWarner retweeted

NEW: BPI research reveals that a Marxist-Leninist group with documented ties to China has been a critical mobilizer in efforts that have blocked or delayed $23.6 billion in AI investment in the US.
Its scalps include 10 data center moratoria, 1 permanent data center ban, and 4 rejected or scrapped AI projects.
In Part II of our foreign influence investigation, BPI exposes the Party for Socialism and Liberation (or PSL) as the political arm of Shanghai-based Neville Singham, and lays bare a national campaign launched by the party to stop America’s data center buildout.
Singham is the subject of multiple federal investigations into his reported ties to the CCP. Our research uncovers the anti-data-center organizing of his activist vehicle, the PSL, across 21 campaigns in 14 states, in roles ranging from lead organizer to one member of a broader coalition.
This report adds to the mounting evidence that China and its surrogates are committed to stopping America’s data center buildout so that Beijing can gain the advantage in the AI race.


GarWarner retweeted
How are a group of internet scammers in Nigeria profiting off of the loneliness crisis in the West? I spoke to @CarlosBarraganT, author of the new book “The Yahoo Boys.”
GarWarner retweeted
A Japanese Scam Boss Ran a Poipet Compound Without Ever Setting Foot in Cambodia
Thai immigration officers arrested a 39-year-old Japanese man in Bangkok's Watthana district over the weekend, wanted in Japan as a leadership figure in a Cambodia-based fraud network. Police identified him only as Sasaki. He's accused of directing a call center operation out of Poipet that impersonated Japanese police officers to swindle victims back home, the kind of tokushu sagi ring where the caller poses as someone in authority, with losses estimated in the billions of yen.
There's no record of Sasaki ever setting foot in Cambodia. He lived in a luxury apartment in Bangkok and ran the operation remotely, making frequent trips to China, Malaysia, and Vietnam to keep it moving. Japanese investigators say he worked alongside Chinese managers at the Poipet compound, and that together they targeted heavily indebted Japanese nationals and trafficked them to the base to work the phones.
Nagoya District Court issued the warrant on April 1, on fraud charges. He's expected to be extradited to Japan. Thai police framed the arrest around their anti-trafficking center and the usual line about not letting the country serve as a transit point for international criminals.


GarWarner retweeted

- For those who continue to frame the #SanDiego mosque shooting as something other than neo-Nazi and white supremacist ideology, the extensive symbolism found on the suspects, their weapons, and vehicle leaves little room for doubt.
- Sonnenrad (Black Sun), swastikas, Odal runes, and the Atomwaffen Division’s trefoil clearly point to a deep ideological commitment.
- To anyone who monitors and researches violent extremist movements, this is as clear as daylight.
- I won’t go into the details of the circulating manifesto at this time, but the ideological motivation and intent are unmistakable.
- This attack appears to be rooted in accelerationism (see also the writings on the handgun)
- The Atomwaffen Division (AWD) trefoil patch visible on the arm is the symbol of a violent neo-Nazi and white supremacist terrorist group. It specifically represents “accelerationism,” the belief that modern democratic society is beyond saving and must be violently destroyed.
- The goal is to trigger a societal breakdown—often envisioned as a race war or "boogaloo"—so that a white ethnostate can be built from the ruins.
- Acts like this are not impulsive or accidental. They require deep ideological commitment, extensive preparation, and a conscious decision to cross into violence.
- The sheer volume, consistency, and specificity of the neo-Nazi symbols and references make it clear that the suspects had fully embraced accelerationist ideology and had almost certainly been planning this attack for some time.
- While there has been a documented rise in online radicalization among teenagers and young adults across various violent ideologies far-right, Islamist, nihilistic/mass shooter subcultures, etc.), what makes this case particularly rare is that 2 perpetrators aged 17 and 18 successfully conspired to carry out a lethal neo-Nazi-inspired firearm attack.


GarWarner retweeted

🚨 201 arrests in first-of-its-kind cybercrime operation in MENA region
Operation Ramz brought together law enforcement agencies across the Middle East and North Africa to disrupt phishing, malware and cyber scam networks responsible for significant financial harm.
Results of the operation included:
🔵 201 arrests
🔵 382 suspects identified
🔵 3,867 victims identified
🔵 53 servers seized
The operation also enabled the sharing of nearly 8,000 pieces of intelligence to support ongoing investigations and strengthen regional cooperation against cyber threats.
Read more ➡️🔗 interpol.int/en/News-and-Eve…


GarWarner retweeted
Sri Lanka has arrested more than 1,000 foreigners for cybercrime since January, up from 430 in all of 2024. Most are Chinese, Vietnamese, and Indian nationals. Networks pushed out of Cambodia and Myanmar are exploiting the 30-day tourist visa regime and setting up in rented villas and office complexes, with one raid this week pulling in 192 Indians and 29 Nepalis across Galle and Matara.
channelnewsasia.com/asia/sou…

GarWarner retweeted

❗️🚨 Microsoft Edge keeps every saved password in process memory as cleartext from the moment it launches. Microsoft's responsed when reported: "by design."
All of them. Including credentials for sites you won't open this session.
Researcher @L1v1ng0ffTh3L4N tested every major Chromium browser. Edge is the only one that behaves this way.
Chrome decrypts credentials on demand, and App-Bound Encryption locks the keys to an authenticated Chrome process so other processes can't reuse them.
In Chrome, plaintext surfaces only during autofill or when a password is viewed, making memory scraping far less useful.
What makes this extra weird is that Edge still demands re-authentication before revealing those passwords in its Password Manager UI, while the same browser process already holds every one of them in plaintext.
In shared environments, this turns into a credential harvest. On a terminal server, an attacker with admin rights can read the memory of every logged-on user process. In the published PoC video, a compromised admin account lifts stored credentials from two other logged-on (and even disconnected) users with Edge running.
Microsoft's official response when notified: "by design."
The finding was disclosed April 29 at BigBiteOfTech by PaloAltoNtwks Norway, alongside a small educational tool that lets anyone verify the cleartext storage for themselves.


GarWarner retweeted

U.S. businesses and individuals were targeted and hacked by Nigerian-linked fraud organizations in an email scheme that spanned 47 states and 19 countries.
In Ohio, victims were in Norwalk, Kent, Akron, Hudson, Maple Heights, Westfield Center, New Riegel, and Greenwich.
Outstanding work by our USAO federal prosecutors and FBI investigators!
CONVICTION DETAILS HERE:
justice.gov/usao-ndoh/pr/25-…
@FBICleveland

Readers added context they thought people might want to know
Nigerian-linked” is misleading given the nationality of the people convicted, and those found guilty.
3 people were convicted, 1 Nigerian, and 2 US nationals, not of Nigerian descent. 25 people were found guilty, 10 Nigerians, and 15 other nationalities, including US. justice.gov/usao-ndoh/pr/2…
GarWarner retweeted
One of the 29 Sanctioned Targets Is a Cambodian Commercial Bank
Heng Feng Cambodia Bank plc, a licensed NBC commercial bank with $382 million in total assets as of end-2024, is now on the OFAC SDN list. Treasury says the bank is controlled by Sai Aung Linn, a 40% shareholder, director, and former chairman who also sits on the board's risk and audit committees.
Sai Aung Linn is Burmese-born and obtained Cambodian citizenship while investing in the country's scam industry, per Treasury. He's also co-owner of Xihu Resort Hotel, a sanctioned Sihanoukville casino tied to Rithy Raksmei's K99 Group. The bank's own 2024 annual report lists its Preah Sihanouk forex counter as operating from the ground floor of Xihu Resort Hotel.



Ransomware Negotiator selling data to the Ransomware threat actors. Not cool.
justice.gov/opa/pr/florida-m…

GarWarner retweeted
68 Indian Nationals Arrested in Back-to-Back Pattaya Villa Raids Over $70 Million Gambling Operation
Thai police hit two luxury villas in Pattaya's Nong Prue area arresting 68 Indian nationals running online gambling operations out of rented pool villas. Combined estimated annual turnover across both sites was 2.3 billion baht, roughly $70 million.
The first villa, near Mabprachan reservoir, had been rented for over a year at 120,000 baht/month. Officers found 43 men working as admins for 23 gambling websites targeting Indian customers. The operation allegedly pulled in up to 5 billion rupees annually. A figure known only as "AK" is believed to have managed logistics. Hours later, immigration police raided a second villa where 25 more men were running three gambling sites with domain names ending in "777." That operation was generating about 5.6 million rupees per day. The garage had been converted into a sealed glass office hidden behind tarps, with generators and frozen food stockpiled so nobody had to leave.
All 68 were on tourist visas. They've been charged with working without permits. Police say they're now going after the Thai and foreign financiers behind both networks.

