

🧵 Following the rails | Transparency | 🌐 Research & bridges #XDC | Discipline = foundation | Not your eBL, not your cargo – eBLを持たなければ、貨物も持てない。
Joined November 2021
- Tweets5.5K
- Following343
- Followers206
- Likes5.6K





Pinned Tweet
PART 39 — ComTech Gold (CGO)
Unregulated Gold Token on XDC With Misleading Compliance Claims
1. Executive Summary
ComTech Gold (CGO) positions itself as a “vault-backed”, “Sharia-compliant”, and “institutional-grade” gold token on the XDC Network.
However, all available documentation — including company registration, terms & conditions, privacy policy, and responses from VARA — confirms the opposite:
CGO is an unregulated token issued by an unlicensed Free Zone entity, operating without financial supervision, without commodity licensing, and without custody approval.
Despite this, CGO is repeatedly showcased by XDC Network as part of its “RWA ecosystem”.
2. Company Structure – No Financial License
The ComTech – Company Registration Details document confirms:
• The company is registered as a DAFZA FZCO (Free Zone Company).
• No financial services license.
• No commodity trading license.
• No VARA license.
• No DMCC license.
• No regulatory approval for issuing asset-backed tokens.
➡️ CGO is legally a normal Free Zone company, not a regulated gold issuer.
VARA confirmed separately via email:
“For information regarding companies licensed by VARA, please refer to the Public Register.”
CGO does not appear on that register.
3. Token Structure – Legal Responsibility Avoidance
The CGO Terms & Conditions contain multiple red-flag clauses:
• CGO provides the token “as is”, with no warranty of value, no guarantee of redemption.
• No legal obligation to deliver physical gold to token holders.
• CGO disclaims all liability, including price risk, custody risk, operational risk, and smart-contract risk.
• The user bears all responsibility, even though CGO markets itself as “1:1 gold-backed”.
➡️ The token is not a legally enforceable gold claim.
It is a marketing representation, not a regulated financial instrument.
4. Custody & Audit – No Regulatory Oversight
CGO promotes:
• “audited vaults”
• “secure physical gold”
• “Sharia-board approval”
• “institutional grade custodian”
But:
• None of the custodians listed in the ecosystem are licensed under UAE SCA, VARA, or DMCC Gold Rules.
• Audits are private, not regulatory.
• No proof of mandatory oversight for gold-backed instruments.
• No evidence of segregated custody or insurance.
➡️ The backing is unverifiable and not subject to any regulator.
5. Data Handling – No Consumer Protection
The Privacy Policy shows:
• User data can be shared with external parties without regulatory limits.
• No reference to GDPR, DIFC DP Law, ADGM DP Law, or UAE Consumer Protection Law.
• No commitment to independent audits or secure data processes.
➡️ Even user data is unprotected, and CGO acknowledges no legal accountability.
6. High-Risk Promotion – Misleading Communication
CGO and associated influencers have repeatedly pushed:
• high-yield pools
• “gold-backed staking”
• 351% APR on XSwap
• vault-backed DeFi narratives
• insinuations of “institutional adoption”
This violates the standards that licensed gold token issuers must follow in the UAE.
7. XDC Network Ecosystem Problem
Despite the lack of licensing:
• CGO is still listed on xdc.org under “RWA”.
• No disclosure that the token is not regulated.
• No warning that gold tokens in the UAE require licensing.
• XDC Foundation presents CGO as ecosystem adoption, not as a high-risk unregulated project.
➡️ The ecosystem presentation creates the false impression that CGO is officially approved.
8. Risk Assessment
Based on all documents and regulatory context, the risk profile is:
High Legal Risk
• No enforceable gold claim
• No regulatory protection
• No investor rights
High Custody Risk
• No licensed vault operator confirmed
• No insurance required by law
High Operational & Smart Contract Risk
• CGO disclaims all responsibility in the T&Cs
High Reputational Risk for XDC
• Unregulated token promoted as RWA use case
9. Conclusion
CGO is not a regulated gold product.
It is a Free Zone token with no regulatory oversight, no enforceable backing, and disclaimers that remove all legal responsibility from the issuer.
The presentation of CGO as a compliant RWA product is misleading, especially when the issuer is unlicensed and the token offers no actual consumer protection.
This raises broader governance questions on the XDC ecosystem’s due diligence and its handling of high-risk partners.
10. Documents stored in the archive
The following PDFs support this Part:
• ComTech – Company Registration Details
• ComTech Gold – Privacy Policy
• ComTech Gold – Terms & Conditions
• CGO Whitepaper v1


knarf 👑🏴☠️ | 🪝 retweeted

Jako żołnierz Wojska Polskiego składałem przysięgę, która jest swoistym zobowiązaniem wobec naszej Ojczyzny i społeczeństwa. Przysięgałem stać na straży Konstytucji RP, bronić niepodległości i granic oraz za sprawę mojej Ojczyzny, w potrzebie krwi własnej ani życia nie szczędzić! Słowa przysięgi traktuję bardzo poważnie i nie wyobrażam sobie, aby ktokolwiek podnosił rękę na ład konstytucyjny i ustrojowy. To, co obecnie wyprawia Premier Donald Tusk, jest próbą zorganizowanego przewrotu i siłowego przejęcia kontroli nad legalnie wybranymi władzami Trybunału Konstytucyjnego. W tej chwili jako obywatel zwracam się do wszystkich porządnych ludzi, aby bronili ładu konstytucyjnego! Nie możemy pozwolić na bandyckie metody przejmowania państwowych instytucji! Ostatnia nadzieja w społeczeństwie oraz Prezydencie RP Karolu Nawrockim! Brońmy Polski! 🇵🇱

knarf 👑🏴☠️ | 🪝 retweeted

URGENTE 🚨São 300.000 patriotas poloneses nas ruas para declarar que a Polônia é um país CRISTÃO.
xitter.cf/America_1777/status/21…
The debate should not be about AI versus developers.
AI can improve security, but it cannot replace accountability.
For a company handling encrypted emails, passwords and sensitive documents, three questions matter:
Who independently verifies AI-generated code?
Can security engineers reject changes without pressure from management?
Will Proton provide verifiable evidence that security reviews are becoming stronger, not weaker?
Trust is not established by defending AI or attacking its critics.
It is established through transparent processes, independent verification and accountability.
Security must be demonstrated, not assumed.

knarf 👑🏴☠️ | 🪝 retweeted

@DCENTWALLETS / IOTRUST — WAKE UP.
@Tether_to has demonstrated that funds can be frozen through coordination with law enforcement.
@binance has channels for reporting stolen funds and handling official requests.
So what EXACTLY have YOU done for the victims?
Have you contacted @binance, @Tether_to, @circle and every relevant exchange or issuer where tracing identified exposure? Have you supplied investigators with the evidence needed to pursue freezes?
Which requests have been submitted? What funds have been located? What obstacles remain?
If you’re doing the work, SHOW US. Give victims a substantive public update with dates, actions and results
And where recovery falls short, explain your reimbursement position.
People trusted your product with their savings. They deserve urgency, transparency and accountability.
GET YOUR ASSES IN GEAR. Victims need action and answers NOW.
#DCENT #IOTrust #CryptoSecurity #CryptoVictims #Accountability
45 DAYS.
@DCENTWALLETS @IOTrust
You sell SECURITY. You sell TRUST. Yet after 45 days, your customers still have no independently verifiable explanation of what went wrong.
Security warnings are NOT accountability.
Where is the root-cause analysis?
Where is the independent forensic report?
Which wallet versions and components were compromised?
What evidence rules out hardware-wallet exposure?
Where is the verified damage assessment?
Where is the compensation plan?
Your customers trusted you with their assets — not with excuses, vague assurances, or indefinite silence.
A hardware-wallet company that cannot publicly demonstrate the security of its own products has a fundamental credibility problem.
45 days. No comprehensive post-mortem. No adequate answers.
Trust is not a marketing slogan. It must be earned through evidence.
Publish the findings. Address the victims. Take responsibility.Your failure to provide transparent, verifiable answers is no longer just a D’CENT problem.
You are undermining confidence in the entire hardware-wallet industry.
People buy hardware wallets because they are promised stronger protection for their assets. When a security company cannot publicly explain what failed, what remains secure, and why customers should trust its products, the damage extends far beyond your brand.
You are not just losing customers' trust. You are damaging trust in self-custody itself.
Publish the evidence. Explain the failures. Address the victims.
knarf 👑🏴☠️ | 🪝 retweeted

頑張れ #globiance
まだ待ってる方がいっぱいですよーーどんどん返金進めていきましょう💪🔥

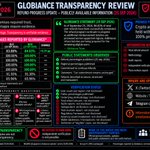
📢 Globiance Refund Progress Update 2026-09-29
✅ 84.26% of total refunds completed
Steady progress continues as additional refund batches are processed globally.
Latest update:
globiance.com/news/globiance…
Regional refund status for all supported countries:
globiance.com/transparency.h…

knarf 👑🏴☠️ | 🪝 retweeted
A huge THANK YOU to everyone who has reached out, shared information, compared transactions, and helped connect the dots.
Every message, transaction trail, screenshot, and similar case helps build a clearer picture of what happened.
The more cases we can document and connect, the harder this is to ignore.
I’m going to keep digging, keep asking questions, and keep looking for answers. If you have information that could help, please keep it coming.
This is what a community looks like. 🙏
knarf 👑🏴☠️ | 🪝 retweeted
THIS IS NO LONGER JUST A FEW D’CENT USERS ASKING QUESTIONS.
X/Grok is now aggregating reports under a story citing 12.4 MILLION XRP across 7,393 wallets — and my documentation is appearing at the top of it.
To be clear: those totals are Grok’s aggregated figures and still need independent confirmation. But the growing number of people reporting unauthorized losses cannot simply be brushed aside.
I started with one missing transaction. I followed the blockchain. I documented addresses, transaction hashes, exchange connections, support responses and other victims’ reports.
And people kept coming forward.
We don't need rumors. We need answers.
D’CENT: publish the incident timeline. Explain what happened. Identify what was affected. Explain what has been secured. And tell victims what you are doing about their losses.
Until then, KEEP THE RECEIPTS COMING.
Screenshots. TX hashes. Wallet addresses. Dates. Support tickets.
The blockchain doesn’t forget. Neither will the people who lost their assets.
#DCENT #XRP #XRPL #CryptoSecurity #CryptoWallet
This is an important point.
D’CENT publicly states that it is working with law enforcement, security experts, blockchain projects and exchanges to trace stolen assets and pursue freezing or recovery.
It makes me ask the same question about the Globiance incident:
Was there comparable cooperation with law enforcement, forensic/security specialists and the XDC ecosystem and if so, what were the results?
More than a year later, we still have no detailed public post-mortem explaining what happened. Refunds are important, but refunds are not an incident investigation.
@globiance @XDCNetwork @XDCFoundation
🤖 Made with AI


NEW D’CENT UPDATE:
D’CENT now confirms the investigation is still ongoing and that they are working with law enforcement, security specialists, blockchain projects and exchanges to trace stolen assets and seek freezes/recovery.
Also important: they did not say the incident is solved. They said they have not identified evidence “to date” that it originated from D’CENT hardware wallets.
This is exactly why victims need to keep documenting transactions, tracing funds and reporting where those assets landed. The investigation is not over.
Thanks for all the congratulations.
But this isn’t just about me getting my XDC back.
Some users are still waiting for their funds. They should not be forgotten.
And even for those who have been refunded, the documented questions surrounding the incident, the refund process and what happened remain.
Refunds do not replace transparency and answers.
The questions remain.
🤖 Made with AI

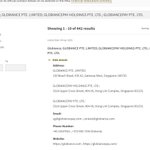
Globiance remains listed on the Monetary Authority of Singapore (MAS) Investor Alert List.
The entry was originally listed on 4 April 2025 and is still searchable on the official MAS website as of 17 September 2026.
This is not a new MAS warning — it confirms that the existing Globiance entry remains active on the list.
#Globiance #MAS #InvestorAlert #Crypto


#InvestorAlert: White Deer Club (operated by New Omaten Productions Technology Pte. Ltd.) ; has been listed on our #IAL mas.gov.sg/investor-alert-li…

knarf 👑🏴☠️ | 🪝 retweeted
XDCScan’s current Daily Transactions CSV shows:
July: 27.735M
August: 33.603M
So August was indeed a record month, but not at the stated 27.7M figure.
Which dataset, block range and counting method did XDC Network use?
For comparison, the same CSV shows:
February: 18.800M
March: 22.420M
July: 27.735M
August: 33.603M
That is +47.5% from February to July and +49.9% from March to August.
What generated the 33.6M transactions?
Please publish the top senders, contracts, transaction types and unique active addresses, plus the shares attributable to named applications, validator system activity and other recurring automated calls.

knarf 👑🏴☠️ | 🪝 retweeted

Blockchain forensics splits across two parties:
A blockchain analytics provider builds the dataset: making attributions about addresses and grouping addresses that share an owner. That work runs continuously, independently of any particular case.
The investigator works on top of it. Following the funds, deciding which branch to take where they mix with other funds, following them onto other blockchains, finding the point where the trail meets a regulated business and documenting the result along the way.
Our new article covers all six steps that make blockchain forensics work: hubs.la/Q04v9bN10

Interesting timing.
ESMA is focusing its supervisory action on CASP custody — including governance, key/storage management, transaction controls, and incident detection & response.
These are precisely the areas where transparency matters after a major incident.
In the Globiance case, fundamental questions remain unanswered:
Who investigated the incident? What actually failed? Who is legally responsible for custody? And where is the post-mortem?
More than a year later, these are reasonable questions.
@ESMAComms @globiance

#ICYMI |🔎 ESMA has launched a common supervisory action on how authorised #crypto-asset service providers manage #digital operational resilience risks linked to custody activities → link.europa.eu/mTpxvR

knarf 👑🏴☠️ | 🪝 retweeted

直ちに補給してください。1日でも早く返すために。もし本当に返す気があるなら、ちまちまやらずにスパッと気持ちよく返しましょう!#globiance#XDC#SBI XDC#SBIVCトレード
This quoted post is unavailable.
Elliptic is not raising new questions. It confirms why the questions repeatedly raised in the Globiance Transparency Review matter: due diligence does not end with KYC or a questionnaire. It requires on-chain verification and continuous monitoring.


🏦 Financial institutions assess new counterparties by asking them questions. For most counterparties, a bank cannot independently observe how they handle the flows they describe, so the bank verifies what it can and takes the rest on the counterparties' word.
For virtual asset service providers, or VASPs, there is more to work with, as much of their activity sit on a public ledger. A bank can test an applicant's account of itself, both the controls it claims to run and the risk profile it claims to have.
The due diligence questionnaire is still where you start. It just isn't where the assessment has to end. hubs.la/Q04tHnt90
