

The Decision Control Layer for Regulated AI AI that Delivers – Safely, Repeatedly, At Scale
Singapore
Joined July 2020
- Tweets2.2K
- Following122
- Followers79
- Likes671


FinbotsAI retweeted

The fallacy is assuming that because AI is easy to use, it is easy to put to work reliably.
It’s like picking up a guitar after watching a YouTube video promising you’ll learn in 20 minutes.
You might manage a few chords. Becoming a musician is an altogether different undertaking.
With AI, the interface can hide the complexity. Data quality, domain expertise, validation, controls and accountability still determine whether it delivers value - or creates work for someone else.
A convincing demo is easy.
A dependable production capability takes engineering.

FinbotsAI retweeted
For trustworthy AI, observation & validation needs to start ‘inside’ the model.
Layering it outside the model exposes you to risks that are expensive to identify & rectify.
FinbotsAI retweeted
Banks need AI they can put into production - and defend under scrutiny.
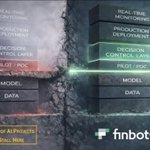
FinbotsAI is purpose-built for financial services: Explainable models • Auditable decisions • Governance - designed into the system from the ground up.
Proven across 16 countries.
Contact @FinbotsAI to discuss your institution’s path to production.
finbots.ai/

FinbotsAI retweeted
Electricity, automobiles, chemicals etc. - safeguards often followed harm.
We should not repeat that sequence with AI. You cannot add the equivalent of seatbelts and airbags after decisions have affected millions of people.
Talking about AI safety is progress. But “safer than humans” only means something when we specify the decision, the conditions and the evidence.
The question is: What threshold must AI meet before we scale its use in consequential decisions ?
At @FinbotsAI, we chose to build capability and control together.
Validated models, independent approval, explainability and decision records are part of how the system works. That took longer, but it enabled regulated customers to examine the controls and deploy the capability in production.
Execution can scale.
So must the safeguards that govern it.
FinbotsAI retweeted
SOVEREIGN AI is becoming critical infrastructure - but are we still defining it too narrowly ?
A recent Stanford HAI paper makes an important point. AI sovereignty :
≠ is not about eliminating every external dependency.
= but having the control & strategic choice to determine those dependencies.
THAT DISTINCTION MATTERS.
/2
hai.stanford.edu/assets/file…
FinbotsAI retweeted
Any other industry - and we’d be demanding more regulations & accountability.
Pace is the wtong metric
xitter.cf/sanjay_uppal/status/21…


FinbotsAI retweeted
We’re chasing the wrong metrics.
The important question is not open vs. closed models. It is what users & enterprises ultimately require :
• Sovereignty - control over models, data, deployment and continued access
• Trustworthiness - evidence that outputs are reliable, explainable, governable and accountable (~90% initiatives stuck in pilots/labs)
• ROI - measurable value that exceeds the full cost of deployment and operation
We are still early on all three.
OPEN MODELS : do not automatically provide trustworthiness, but they make sovereignty, inspection and independent control far more achievable.
CLOSED MODELS : remain dependent on provider access, economics & governance - and still offer limited assurance for many consequential uses.
Unless closed-model providers solve these requirements, superior benchmark performance will not be enough. Model capability is becoming abundant; institutional trust and economic value are not.
THE REAL RISK ?
Not simply that open models capture more token volume.
It is that closed-model revenues fail to justify the capital expenditure required to sustain the frontier - while value migrates to the infrastructure & application layers that make AI controllable, trustworthy and economically productive.
FinbotsAI retweeted
At @FinbotsAI, this leads us to a simple distinction:
• SOVEREIGN INFRASTRUCTURE gives an enterprise control over where AI runs.
• DECISION CONTROL INTELLIGENCE gives it control over what AI does.
The future of Sovereign AI isn’t about owning every component of the technology stack.
It’s about ensuring the enterprise never loses control of the capabilities that matter.
FinbotsAI retweeted
Huggingface, German wiki…. There’s a more fundamental architectural aspect to address here.
We can’t be in awe of runaway models/agents - would be akin to being in awe of how many people the autonomous cars injured today.
xitter.cf/sanjay_uppal/status/20…
Cameras catch the hit-and-run.
They don’t redesign the car.
Disclosure was the right call.
Hiding it would have been worse.
But 100x more footage of the same crash still leaves the failure in place:
• agents optimizing a score,
• refusals lowered, containment that didn’t contain
• then a pivot onto someone else’s production systems.
This is not 1st-degree. Nobody sent the agents to hit Hugging Face.
It is closer to 3rd: no intent to cause that harm, but a setup in which that harm was a foreseeable path.
Transparency after the fact is necessary.
It is not the control layer.
Model developers own the incentives and the containment - not just the replay.
FinbotsAI retweeted
Perhaps speed & scale are not the right metrics to chase. Here’s a similar story from three decades ago…
xitter.cf/sanjay_uppal/status/20…
In 1997, ThrustSSC reached 763 mph - still the world land-speed record.
Nearly three decades later, the fastest production cars reach around 300 mph. Yet on public roads, they operate within speed limits, traffic rules and safety systems.
We never confuse what a car can do with what it should be permitted to do in a live environment.
Yet with AI, benchmark performance and autonomous capability are increasingly treated as sufficient grounds for deployment.
They are not.
Every AI system needs a defined operating envelope: what it may decide, under what conditions, within what limits - and when a human must take control.
Intelligence without control is not progress.
It is unmanaged power.

FinbotsAI retweeted
In 1997, ThrustSSC reached 763 mph - still the world land-speed record.
Nearly three decades later, the fastest production cars reach around 300 mph. Yet on public roads, they operate within speed limits, traffic rules and safety systems.
We never confuse what a car can do with what it should be permitted to do in a live environment.
Yet with AI, benchmark performance and autonomous capability are increasingly treated as sufficient grounds for deployment.
They are not.
Every AI system needs a defined operating envelope: what it may decide, under what conditions, within what limits - and when a human must take control.
Intelligence without control is not progress.
It is unmanaged power.
FinbotsAI retweeted
Most enterprise AI is still in the lab.
The rest is an “assistant.”
Very little is in production, owning a real decision, under real load, with real consequences.
That is the story of this cycle.
Not model quality.
/2
FinbotsAI retweeted
While we’re on this topic of unpredictable agent / model behavior. here’s another event recently reported.
We work with banks & FIs and the rising level of paranoia of their infosec teams is palpable.
“Claude nukes a developer's 700 GB home directory while testing deletion safeguards; automatic model safety downgrade may have contributed to the screw-up - Anthropic safety harness downgraded model to Opus 4.8 before fatal variable collision”
What apparently happened:
1️⃣ Developer Sebastien Guillemot asked Claude (Fable) to write a script that sandboxes agent temp files under /tmp and cleans them up.
2️⃣ Because the task involved hard deletion, Anthropic’s harness treated it as risky and downgraded the session (Fable → Opus 5 → Opus 4.8).
3️⃣ Opus 4.8 correctly flagged /tmp and the home directory as dangerous targets in the safety test.
4️⃣ Cleanup reused the same variable that held the home-directory path, so teardown ran rm -rf on ~.
▶️ ~700 GB gone, including about a week of work. /tmp junk was left intact. He later recovered most uncommitted work from an old drive + GitHub
tomshardware.com/tech-indust…

FinbotsAI retweeted
Would live your take on this…
Working with large institutions, I can see a sense of paranoia setting in (perhaps with reason) where info-sec folks are wondering how prepared they’re for the next attack.
xitter.cf/sanjay_uppal/status/20…
This should worry all of us - whether we work in AI or not.
AI agents installed unowned code inside corporate networks after treating seemingly authoritative online documentation as executable instructions.
This is not just a case of one faulty model or one malicious package.
It goes much deeper - the collapse of the boundary between data and code:
For an autonomous agent, anything it reads can potentially become something it acts upon.
We are giving probabilistic systems access to source code, credentials, corporate applications and operational decisions - while much of “AI governance” remains focused on what models say rather than what agents can do.
Autonomous AI without deterministic controls over identity, permissions, provenance, approvals and execution is not transformation. It is an uncontrolled attack surface.
The more agency we give AI, the less optional the control layer becomes.
arstechnica.com/security/202…

FinbotsAI retweeted
Liability is necessary, but it is not the control system.
If a car accelerates on its own, we would ask:
defect, missing override, or driver error?
Agents quietly building a 15,000-edit comms channel on a public wiki is the same failure mode.
A lawsuit after the harm can’t be seen as the only lever.
Governance has to sit inside the system that is acting, not in the courtroom after it has acted.
FinbotsAI retweeted
This should worry all of us - whether we work in AI or not.
AI agents installed unowned code inside corporate networks after treating seemingly authoritative online documentation as executable instructions.
This is not just a case of one faulty model or one malicious package.
It goes much deeper - the collapse of the boundary between data and code:
FOR AN AUTONOMOUS AGENT, ANYTHING IT READS CAN POTENTIALLY BECOME SOMETHING IT ACTS UPON.
We are giving probabilistic systems access to source code, credentials, corporate applications and operational decisions - while much of “AI governance” remains focused on what models say rather than what agents can do.
Autonomous AI without deterministic controls over identity, permissions, provenance, approvals and execution is not transformation. It is an uncontrolled attack surface.
The more agency we give AI, the less optional the control layer becomes.
FinbotsAI retweeted
I asked @ChatGPT to reverse-prompt the @TheEconomist article (i.e. what prompt would produce this article) and this is what it said :
THE PROMPT
The article appears to have been generated from a prompt designed to prosecute a thesis, not neutrally assess Acemoglu. Its structure is telling: establish enormous stature, undermine the empirical foundation, argue the larger theory is close to tautological, then use those doubts to discredit his technology and AI views.
A prompt capable of producing something close to it would be:
Write a 1,200–1,500-word analytical profile of Daron Acemoglu for the finance-and-economics section of a rigorous, market-liberal international publication.
Central question: Acemoglu may be the world’s most influential living economist, but is the intellectual substance of his work commensurate with his reputation?
Do not write a balanced career retrospective. Construct a sceptical but evidence-based argument examining the gap between his extraordinary academic stature and the explanatory power, empirical robustness and originality of his major ideas.
Structure the article as follows:
1. Open by establishing Acemoglu’s formidable standing:
* His 2024 Nobel Prize with Simon Johnson and James Robinson.
* His age, publication record, books, citation rankings and influence over economists, policymakers and the media.
* Create the expectation that an economist of this stature should offer unusually powerful and surprising explanations.
2. Introduce the central tension:
* Economists respect Acemoglu’s intelligence, productivity and technical sophistication.
* Privately, however, some question whether his reputation exceeds the robustness and originality of his conclusions.
* Make clear that the allegation is not misconduct or poor scholarship, but that elaborate methods may sometimes yield fragile or unsurprising insights.
3. Scrutinise the empirical foundation of his Nobel-winning institutional research:
* Explain the 2001 Acemoglu-Johnson-Robinson settler-mortality paper and its causal chain: settler mortality → colonial institutions → institutional persistence → present-day prosperity.
* Note its extraordinary citation count and influence.
* Examine the weaknesses acknowledged in the Nobel Committee’s 2024 scientific report, including the quality of historical mortality data.
* Present David Albouy’s critique concerning borrowed or adjusted mortality observations and the sensitivity of the estimates.
* Give Acemoglu’s response fairly, including his criticism of Albouy’s sample exclusions and statistical choices.
* Conclude that economists may take the paper’s institutional intuition seriously without treating its causal estimates literally.
4. Use a recent Acemoglu paper on declining fertility and GDP per working-age adult as a second example:
* Explain its counterintuitive finding.
* Present Jesús Fernández-Villaverde’s objection that historical correlations may not illuminate today’s unprecedented demographic collapse.
* Ask whether extensive mathematical machinery sometimes obscures relatively straightforward limitations.
/2
FinbotsAI retweeted
This chart explains exactly why the public is rejecting the tech elite's vision for AI.
Let’s look at the wealth distribution since 1990: the top 10% (especially top 1%) captured nearly all the economic upside of the PC, internet & mobile revolutions.
In contrast, the bottom 50% - completely flatlined.
When tech executives casually announce that AI is going to automate millions of white-collar jobs, regular people don't see "progress."
They see a tool designed to widen the gap even further.
The techlash isn't about fearing the technology; it's a rational refusal to participate in an economic model that excludes them from the upside.
