






Is @wiglenet queue processing down? My upload from two days ago is still in its same queue position


This has a be a troll


FiberMoose retweeted

A person representing themselves in court hid a prompt injection attack in a filing asking an AI system to side with them. Really good stuff here
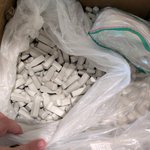
In my defense, the person running around yelling shenanigans and tagging people was POST me p̶a̶w̶n̶i̶n̶g̶ ̶t̶h̶e̶s̶e̶ ̶o̶f̶f̶ ̶o̶n̶ donating 1,000 58khz tags to the #tamperevidentvillage
I hope many more responsible hackers learned how these work, and how to bypass them! #defcon


Contact at 26k ft over San Marcos/North San Antonio
Also confirmed contacts with Leander/North Austin while at 10k ft over southern Austin
FiberMoose retweeted

Bringing a radio to @DEFCON this year? Visit conham.radio/dc to see all the active frequencies this year and get on the air!
#HamRadio #AmateurRadio #defcon33

ALT A promotional image for ConHam. The name "ConHam" is written in the center in a large, white, dashed-line font styled to look like ASCII art. The background is a dark green gradient with a faint grid pattern, creating a retro computer terminal aesthetic. In the top-right corner, text reads, "Presented by N1CCK &," followed by the Ham Radio Village (HRV) logo. At the bottom of the image, a line of text provides communication details: "Simplex: 146.580 MHz | conham.radio | SSTV: 447.800 MHz".


FiberMoose retweeted

During a recent incident response case, we observed the following file access: \\localhost\C$\@ GMT-2025.06.21-10.53.43\Windows\NTDS\ntds.dit
This is a clever method of accessing a Volume Shadow Copy (VSS) snapshot. Many EDR and detection systems typically monitor for commands such as 'vssadmin list shadows', and may trigger alerts based on their use.
However, by leveraging the "Previous Versions" feature in Windows (see screenshot), attackers can select a snapshot, view its properties, and enter the '@ GMT' path directly in Explorer. This allows them to browse the snapshot's contents without needing to use the command line.
Because this technique doesn't rely on typical shadow copy commands, it may evade detection by your EDR or SIEM solution. You might want to test it in your environment to identify and close this potential detection gap 🦸♂️🦸♀️
