





I created a nifty script that runs through all our customers Sonicwalls and generates a report on wide open port forwarding.
Waiting for permission to publicly publish on Github.

TBH I created a whole Powershell module to interact with Sonicwall devices in bulk and it's amazing.
Wanna enable a specific eventlog to email/syslog? With ~ 3 lines of code it's done.
Matching will be done by hashing every row content and comparing the hashes with unmatched hashes means new entries and will be appended to the list.
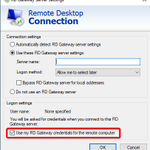
I RDP into my computer using Entra Auth (WAM). On subsequent RDP into my computer from that client no password is needed.
Only nuking Microsoft.AAD.BrokerPlugin from %localappdata% seems to work.
CAP doesn't seem to help.
How am I supposed to prevent this?
@NathanMcNulty
Am I the only one that hates using server manager or the RemoteDesktop powershell module to manage RD collections? I feel they have a lot of arbitrary limitations (possibly for good reasons🤷♂️) and throw weird inconsistent errors (looking at you - collection certs).
Tip 3: Static user to RDSH assignment
Invoke-CimMethod -Namespace root\cimv2\rdms -ClassName Win32_RDMSDesktopAssignment -MethodName AddDesktopAssignment -Arguments @{CollectionAlias="<>";DesktopName="<>Server FQDN";userdomain="<Netbios domain name>";username="<samaccountname>"}
Abe Felds retweeted

BREAKING: Wright brother’s forced to make emergency landing just 12 seconds after takeoff.


SpaceX loses Starship rocket as it returns to Earth on.ft.com/3v7ThwF


I was looking everywhere for the vm2dmp utility from Microsoft. A tip from twitter lead me to github.com/CSS-Windows/Windo…… which showed the package was removed, apparently someone doesn't know git [history]. so here you go github.com/CSS-Windows/Windo…
Based on documentation, if exchange logs show auth protocol as negotiation that means we are using Kerberos. But how can we be using Kerberos when there is no SPN configured for WEB/FQDN?
I did some wiresharking and it seems Kerboros magic is happening somehow via LDAP.
How?
Of course I understand that outlook might be relying on LDAP to get exchange information and it's not acting as authentication carrier. Question is then how does authentication happen?