




FaLcon Intelligence retweeted

Post Compromise Active Directory Checklist
pwndefend.com/2021/09/15/pos…
FaLcon Intelligence retweeted

Exploit code released for three iOS 0-days that Apple failed to patch - @serghei
bleepingcomputer.com/news/se…


FaLcon Intelligence retweeted

#Sodinokibi / #REvil #ransomware is back and not just their sites. The latest variant from today: virustotal.com/gui/file/ab0a…


FaLcon Intelligence retweeted
Windows CVE-2021-40444 defenses bypassed as new info emerges - @LawrenceAbrams
bleepingcomputer.com/news/mi…

FaLcon Intelligence retweeted
#MSHTML RCE Vulnerability #CVE-2021-40444
#DFIR How to find mhtml object:
1) Unzip the MalDoc
2) Navigate to *\word\_rels\*
3) open document.xml.rels
4) Screech for: Target="mhtml:
Sample:
bazaar.abuse.ch/sample/d0e1f…

FaLcon Intelligence retweeted

We’ve found #UnderminerEK has the following modules and can exploit a whopping 11 different vulnerabilities including #PrintNightmare.


#UnderminerEK is back! Now dropping #Amadey
(CC: @malware_traffic, @jeromesegura)
tria.ge/210907-pfppgsfgbq/be…


FaLcon Intelligence retweeted

Fortinet FortiWeb OS Command Injection [‼️0-day]
[PoC]
POST /api/v2.0/user/remoteserver.saml HTTP/1.1
...
...
Content-Disposition: form-data; name="name"
`touch /tmp/vulnerable`
rapid7.com/blog/post/2021/08…


FaLcon Intelligence retweeted

Proofpoint reports an increase in malicious use of Cobalt Strike in threat actor campaigns. Cobalt Strike is currently used by more cybercrime and general commodity malware operators than APT and espionage threat actors. proofpoint.com/us/blog/threa…

FaLcon Intelligence retweeted

ラッキービジター詐欺で不正サイトへのリダイレクトに悪用されるドメインを掲載するレポジトリを公開しました。新しい不正ドメインが観測された際は、こちらに掲載されますので、ご活用ください。 ^ST
github.com/JPCERTCC/Lucky-Vi…

2021年5月に観測したPurple Foxのランディングはこちらです。
#PurpleFox(#PurpleFoxEK)


FaLcon Intelligence retweeted

New blog post! #nccTrojan is a RAT used by #TA428 in attacks targeting East Asian defense and aviation organizations. Please see the analysis result of nccTrojan v1 and v2😆
insight-jp.nttsecurity.com/p…
2021-02-17
#Malvertising -> #RIGEK -> #loader -> #BrowserAssistant
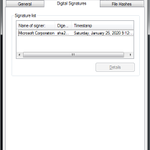
The loader had Microsoft digital certification, which has been identified as an invalid signature.
app.any.run/tasks/0b345b26-e…
virustotal.com/gui/file/660f…

2021-01-29
#Malvertising -> #RIGEK(#ExploitKit) -> #Smokeloader -> #Ursnif(#Dreambot)
location:Japan
SerpentKey=78347829JSDUKLHG
Version:250161
id=8005
tria.ge/210128-mlthgt7r1n/
app.any.run/tasks/2f03c307-a…

2021-01-28
#Malvertising -> #RIGEK(#ExploitKit) -> #Buer(##BuerLoader)
app.any.run/tasks/00911cec-c…
tria.ge/201109-k5prgaf7c2/be…

2021-01-20
#Malvertising -> #RIGEK(#ExploitKit) -> #Dridex OR Unknown malware
It seems that the malware that infects depends on the location.
app.any.run/tasks/50ae4c7f-6…
tria.ge/210120-y331pgwt4x/
app.any.run/tasks/b06331f4-9…
tria.ge/210120-v29hj1wrce/
analyze.intezer.com/analyses…


2020-12-08
#Malvertising(#Makemoney) -> #RIGEK(#ExploitKit) -> #Taurus
Sample
app.any.run/tasks/19d0b239-0…
tria.ge/201207-6lzldmdycn/
Reference
blog.malwarebytes.com/malwar…
