

ElcomSoft's Official Twitter. Password recovery, mobile & cloud forensics.
Joined March 2009
- Tweets7.3K
- Following2.4K
- Followers10.9K
- Likes3.5K






ElcomSoft retweeted

Please share this far and wide. As far and wide as you can. NIST Password Guidelines for 2024 are in the process of being updated.
This is a HUGE pet-peeve of mine (when vendors in particular are still operating like its 2017 and keep changing passwords every 60 days, STOP DOING THIS, it's outdated and has been shown to put you MORE at risk than less -- NIST explains why it does in this document, meticulously outlining user behavior**) so I'm sharing this in the hopes all of you will pass it along to your bosses.
The Special Publication series governing passwords is SP 800-63 "Digital Identity Guidelines".
The 2024 version is 800-63-4.
Here: pages.nist.gov/800-63-4/
The companion docs are also on that link. They are 800-63A, 800-63B and 800-63C. These are different documents for different scenarios in play at your org.
The previous update was in2020.
The changes in the 2020 version from the 2017 version were numerous but one of them was that the password verification method should NO LONGER require passwords be changed at specific intervals (i.e. every 60 days) but in the following circumstances instead:
1. After a breach/compromise
2. User request
2024 repeats this and adds a bunch more guidlines but here is a screenshot of page 13 of the new 800-63-4 (note the # 4 after it) which outlines how your systems should now and moving forward, be handling passwords.
This goes for Active Directory, too. All your systems which have passwords should align with these guidelines provided there isn't another standard or framework you must adhere to which overrules this.
Most frameworks, however, have moved away from arbitrary password resets and complexity rules.
**We cybersec researchers and hackers use wordlists from breaches in a variety of different ways. Hackers use them in tooling to crack passwords whereas researchers use breach dumps to see the kinds of passwords users are creating and the psychology behind them.
Using complexity rules gets you the user psychology of:
Password1
Password2
and so on
Use phrasing instead and allow for spaces, which is important. Humans type phrases with spaces. They also mention phish-resistant methods and most vendors are on-board with MS going to be turning off all Legacy Auth next month, across all free accounts and tenancies.
I'm so excited for the new changes!
Ok I'm off my soapbox.
Share the love! Thank you!


ElcomSoft retweeted

Just performed a FFS Extraction on an iPhone 14 with iOS 16.6.1 via the new release. It was easy and quick. Awesome job as always @ElcomSoft
ElcomSoft retweeted

Last blog post of the year: "Has the user ever used the XYZ application? aka traces of application execution on mobile devices"
blog.digital-forensics.it/20…
#dfir #mobileforensics
ElcomSoft retweeted
SCOOP: Russian Hackers’ Lawsuit Reveals Weaknesses In Apple’s iOS 16 trib.al/ss9Rc52 by @iblametom
ElcomSoft retweeted
iOS 15 Image Forensics Analysis and Tools Comparison - Browsers, Mail Clients, and Productivity apps
blog.digital-forensics.it/20…
#DFIR #mobileforensics
ElcomSoft retweeted

iPhone 14 running iOS 16? No problem thanks to @ElcomSoft agent-based acquisition. #DFIR

ElcomSoft retweeted

😎We are excited to welcome back Elcomsoft @ElcomSoft as our 🖋️Signage Sponsor
Checkout latest talks, CTF & lots more ➡️bit.ly/3VWR8g6
#NullconGoa2023 #Infosec #Conference

ElcomSoft retweeted

Ang. seneste afsnit af SMS-gate: Jeg har talt med en ekspert i gendannelse/efterforskning af data fra mobiler, @v_katalov fra @elcomsoft. Tl;dr, det er meget lidt sandsynligt at gendanne de famøse beskeder, selv hvis alle de mange hvis'er var på plads. Lidt længere:


ElcomSoft retweeted

Fantastic case study by Chris Collins (linkedin.com/in/christopher-…) about how different iOS artifacts can help tell a story.
Path of a Murderer: Location revo4n6.com/blog-posts/f/pat…

ElcomSoft retweeted
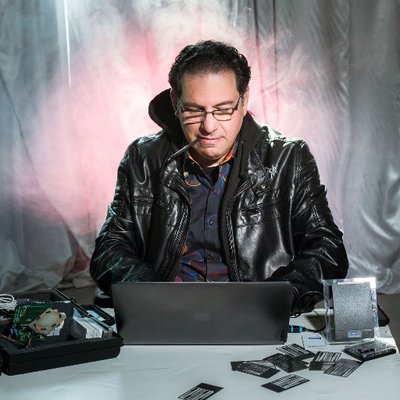
This is my new bad ass password cracker.
I have 24 4090's + 6 2080's all clustered running Hashtopolis.
Thanks to the awesome team at @KnowBe4 that set up and configured the servers for me.
Now to go crack some hashes :-)))))))


ElcomSoft retweeted
Forensic Analysis of Apple IoT Devices (Apple TV, Watch, HomePod, HomeKit)
Hope to see you there next week!
#dfir #RSAC2023 #RSAC @RSAConference @sansforensics
rsaconference.com/USA/agenda…
ElcomSoft retweeted
A curated list of iOS Forensics References
Blog post: blog.digital-forensics.it/20…
GitHub: github.com/RealityNet/iOS-Fo…
#dfir #mobileforensics #FOR585

ElcomSoft retweeted
My learning lab on "Forensic Analysis of Apple IoT Devices (Apple TV, Watch, HomePod, HomeKit)" is ready!
See you at @RSAConference on April 26th!
#DFIR #IoTForensics
rsaconference.com/USA/agenda…
ElcomSoft retweeted
🙌We are glad to Welcome back @ElcomSoft as our 🤝Community Partner at #NullconBerlin
👊Checkout all the tracks, activities & grab your tickets👉bit.ly/3Tq3Em2
#NullconDE2023 #Infosec #Conference


