

Bug Bounty Hunter | Finding Bugs
Somalia
Joined November 2020
- Tweets827
- Following2.3K
- Followers839
- Likes22.2K


Mohamed Yusuf retweeted

@Bugcrowd triagers are insanely fast! Assessed 3 reports, built the rig, and validated 10 files in under 3 minutes. Marked not reproducible, but that speed? Just wow!
I wonder how they did that, whatever tech and setup you are using is out of world. ;)
Mohamed Yusuf retweeted

After all those duplicates and a lot of waiting, things finally started paying off. 🫡
$19,550 in bug bounty rewards from September through October.
More to come. 🚀
#bugbounty #Bugcrowd

Mohamed Yusuf retweeted

My biggest bounty so far🥹 Never expected it to be a P1... Thank you, God.. 🙏
Tip: Learned from @Assass1nmarcos report titles... understood the concept with ChatGPT.. then gave my AI a detailed prompt. It found this bug in just 9 hours.. ❤️
#ItTakesACrowd


Mohamed Yusuf retweeted
Huge respect to @Masonhck3571 👏 We hope more @Bugcrowd triagers adopt this level of transparency and clear communication when handling reports. Researchers deserve to understand the technical reasoning behind every decision :) 💯


Mohamed Yusuf retweeted

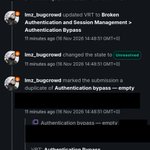
I found a bug on bugcrowd that has a misconfigured security header on payment that an attacker can use to exfil payment card data but I can't find the exact vrt category so I picked the closest which was p5, 20 minutes later, they closed the bug as informational...
Mohamed Yusuf retweeted

Bugcrowd is much better before when JasonH and Ryan is leading the triage team. But now, it's a complete mess, a lot of incompetent analyst. 🫣

Triaging experience at @Bugcrowd is extremely bad, even the valid demonstrated findings with POC and high - critical impacts are being marked N/A with templated comments.
Mohamed Yusuf retweeted

mixed for me, 290 reports in and 107 came back dupes
80 paid out for $131k tho so i keep showing up
Mohamed Yusuf retweeted

I wonder if Bugcrowd’s customers still think they’re getting good value from the platform somehow.
Are there some researchers having a consistently good experience there?

I also want to share my experience with @Bugcrowd, since it seems I'm not the only one:
Initial context
Since incorporating AI into my workflow, I've been able to significantly increase the number of vulnerabilities I discover and report while spending roughly the same amount of time on Bug Bounty as before.
Instead of simply doubling my submissions to HackerOne, I wanted to diversify and give Bugcrowd a try. It was a platform I was barely familiar with (in terms of how they operate, what programs they offer, etc.), but I found it interesting because of the well-known companies running programs there and bounty tables comparable to those on H1
My experience with the platform
Since August this year, I've been submitting reports with genuine enthusiasm and confidence about starting my journey here. Unfortunately, the experience has been nowhere near what I imagined.
Here are my main issues and criticisms:
1/4 🧵
Mohamed Yusuf retweeted
I know triaging reports is part of your job, bro, but to a researcher on the other side, your time and decisions are part of a much bigger learning experience. Thank you for every report you reviewed. I genuinely miss those days 🐐
@Bugcrowd #Bugcrowd #BugBounty

Mohamed Yusuf retweeted
Person_Bugcrowd is one of the best triagers at Bugcrowd, recognized for strong technical expertise and a deep understanding of vulnerability assessment and validation thank you Man 🔥
@Bugcrowd #Bugcrowd #bugbounty

Mohamed Yusuf retweeted

This is how you complain about triage and get listened too by the way, no naming individuals, focus on your experience, professional etc
• Triage is extremely slow or practically nonexistent: This is something affecting all platforms, and from what I understand, Bugcrowd has recently expanded its triage team, which seems like a positive step. It's also true that, since my account is "new", I probably don't get much priority in the queue. But even so, the delays are honestly ridiculous.
• Reports get closed with canned responses such as:
‣ "We were unable to reproduce your issue" → OK, fair enough, but can we discuss what went wrong? Why immediately close it as N/A and call it a day?
‣ "If you still believe that this issue is valid after your review, please create a new submission" → So the solution is to keep flooding the triage queue instead of keeping the entire discussion in a single report? Am I supposed to submit the same issue X times until I finally get a triager who can reproduce it?
‣ (This one is probably my favorite lol) "This is all theoretical with no actual valid proof of concept as this submission only contains text-based claims" → What exactly do you mean by "theoretical" and "no PoC"? Isn't source code, raw HTTP requests, and step-by-step reproduction instructions a PoC? Does the vulnerability suddenly cease to exist? Or, put differently, if I fill my report with screenshots and pretty decorations, does that suddenly make me a super hacker? (This is a made-up example: Do I really need to attach a screenshot of alert(1) so you don't have to test the vulnerable request that triggers that same alert(1)?)
• I open blockers (= requests for Bugcrowd's intervention, somewhat similar to mediation on H1) and, of course, nobody from Bugcrowd responds.
Examples
• In one report, the company's own staff opened a blocker requesting Bugcrowd to assess the impact. Since Bugcrowd never responded, the company had to handle the entire report and pay the bounty without any assistance from the platform (which, I assume, they're paying for...). And here's the cherry on top: once the company had already paid, the vulnerability had been fixed, and everything was resolved, Bugcrowd finally showed up!!! And what for, you might ask? Well, to update the report status and award me some internet points (Very useful!!! Please note the sarcasm.)
• I gained access to a company's Dropbox through a leaked API key exposed on a subdomain associated with one of its programs. A pretty serious impact, in my opinion, and certainly not the kind of access you'd want a real attacker to have. Well, the solution was simple: N/A. Because, of course, since the subdomain wasn't explicitly listed in scope, we should apparently understand (sarcasm again) that we can't act ethically and report unauthorized access to a service because, oops, I happened to inspect the source code of an OOS subdomain... (As if the root issue in my report were a vulnerability in that subdomain rather than an API key leaked through whatever means.)
2/4 🧵

Mohamed Yusuf retweeted
The issue is not bugcrowd … it that shit handler Tal_bugcrowd
He said one of my p1 is duplicate with cve , but the team already fixed that and mine was new one.
And the site is currently had the issue
They are marking duplicate if our findings are similar instead same